
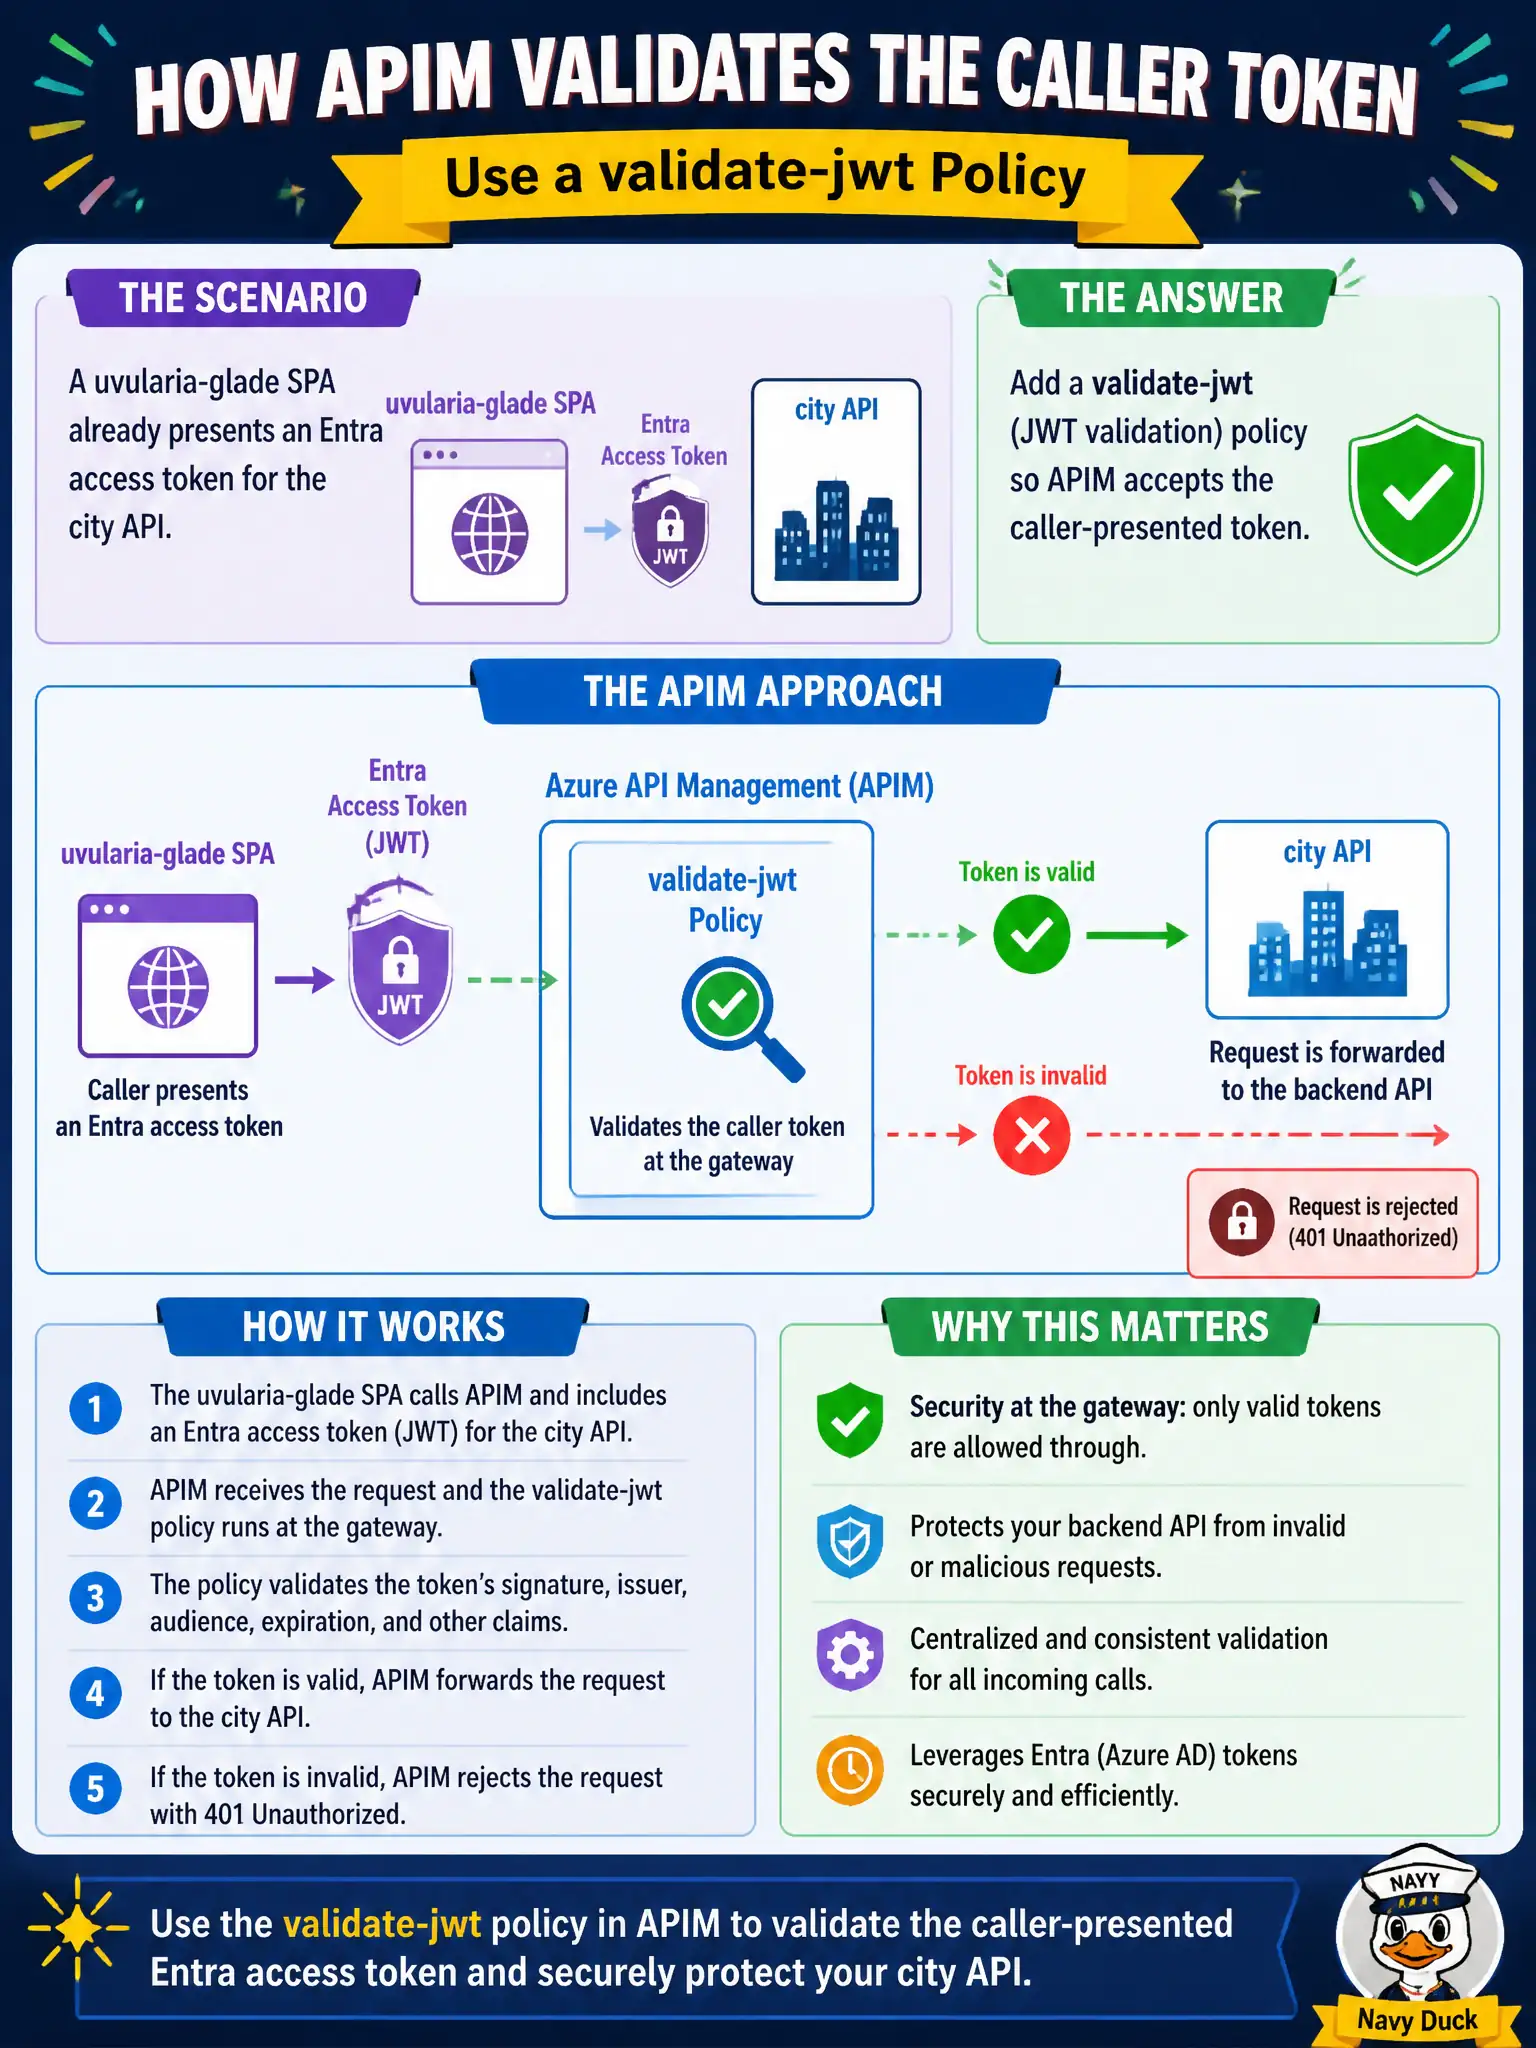
A uvularia-glade SPA already presents an Entra access token for the city API. Which APIM approach validates that caller token at the gateway?
Select an answer to reveal the explanation.
Short Explanation
SPA already has an Entra access token? Validate it with validate-jwt at APIM—subscription key alone is the wrong shape for that uvularia-glade flow.
Full Explanation
When a uvularia-glade SPA already presents an Entra access token for the city API, add a validate-jwt (JWT validation) policy in API Management so the gateway checks issuer, audience, signature, and required claims before forwarding. That aligns the facade with the bearer token the SPA already obtains.
Requiring only a subscription key and ignoring the SPA’s Entra token fails to validate caller identity in the token-based flow the app already uses (keys may still be layered, but they do not replace JWT validation here). Issuing a new storage account key on every page load is unrelated to Entra access tokens and is an anti-pattern. Moving token validation into a Logic Apps HTTP webhook outside APIM abandons the native gateway policy designed for this purpose.
Exam caveat: subscription keys and JWT validation often appear together in real designs, but when the question focuses on validating a caller-presented Entra token, validate-jwt is the specific APIM policy.
Operational check: configure validate-jwt with the Entra openid-configuration/issuer and expected audience, call the API with a valid SPA token and confirm success, then retry with a missing or wrong-audience token and confirm the gateway rejects before the origin sees the request.