
Amazon Inspector reports a critical CVE in packages on instances launched from a warehouse gold AMI. A teammate expects GuardDuty to scan that AMI and clear the CVE. What removes the finding's cause?
Select an answer to reveal the explanation.
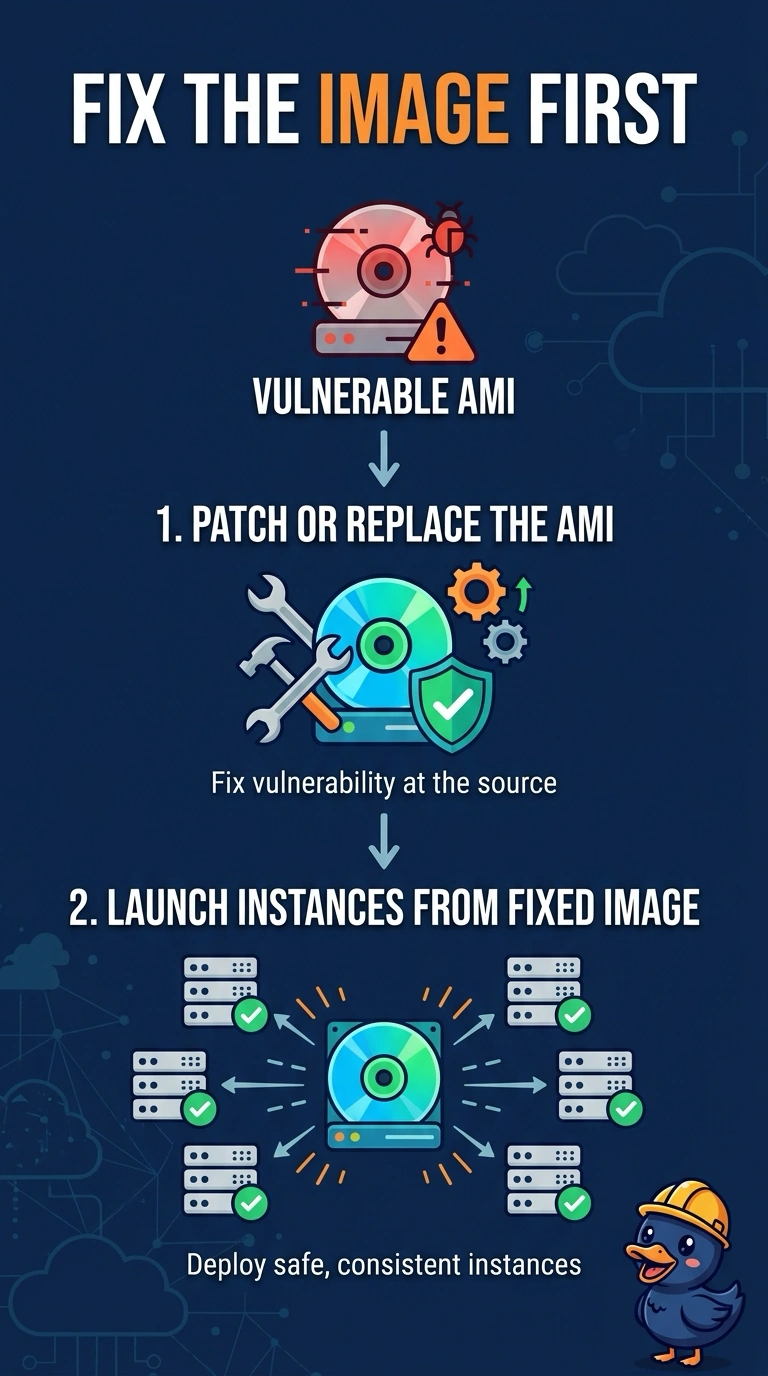
Short Explanation
You’ve found the right fix: patch the vulnerable packages or replace the gold AMI, then launch instances from that fixed image. GuardDuty detects threats, not AMI package CVEs, while deleting an Inspector finding or enabling VPC Flow Logs leaves the vulnerable packages unchanged.
Full Explanation
Amazon Inspector reports package vulnerabilities, including CVEs, on the workloads it scans. To remove the finding’s cause, patch the vulnerable packages or replace the gold AMI, then launch instances from the fixed image so new instances do not inherit those packages. GuardDuty detects threats such as suspicious API activity and malicious network behavior; it does not scan an AMI for CVEs or patch packages, so waiting for it leaves the cause in place. Deleting an Inspector finding changes the record, not the installed packages, and a later scan can report the same CVE. VPC Flow Logs record network flows; accepted traffic neither updates a package nor clears a vulnerability finding. Caveat: instances already running from the old AMI remain vulnerable until they are patched or replaced, even after the image is fixed. Practical check: after patching or creating the replacement image, launch a test instance from the fixed AMI and confirm Inspector no longer reports the critical CVE.