
A security review wants one place that shows this account's GuardDuty threat findings and Inspector vulnerability findings together. An operator opens only the GuardDuty console. What does that approach miss?
Select an answer to reveal the explanation.
Short Explanation
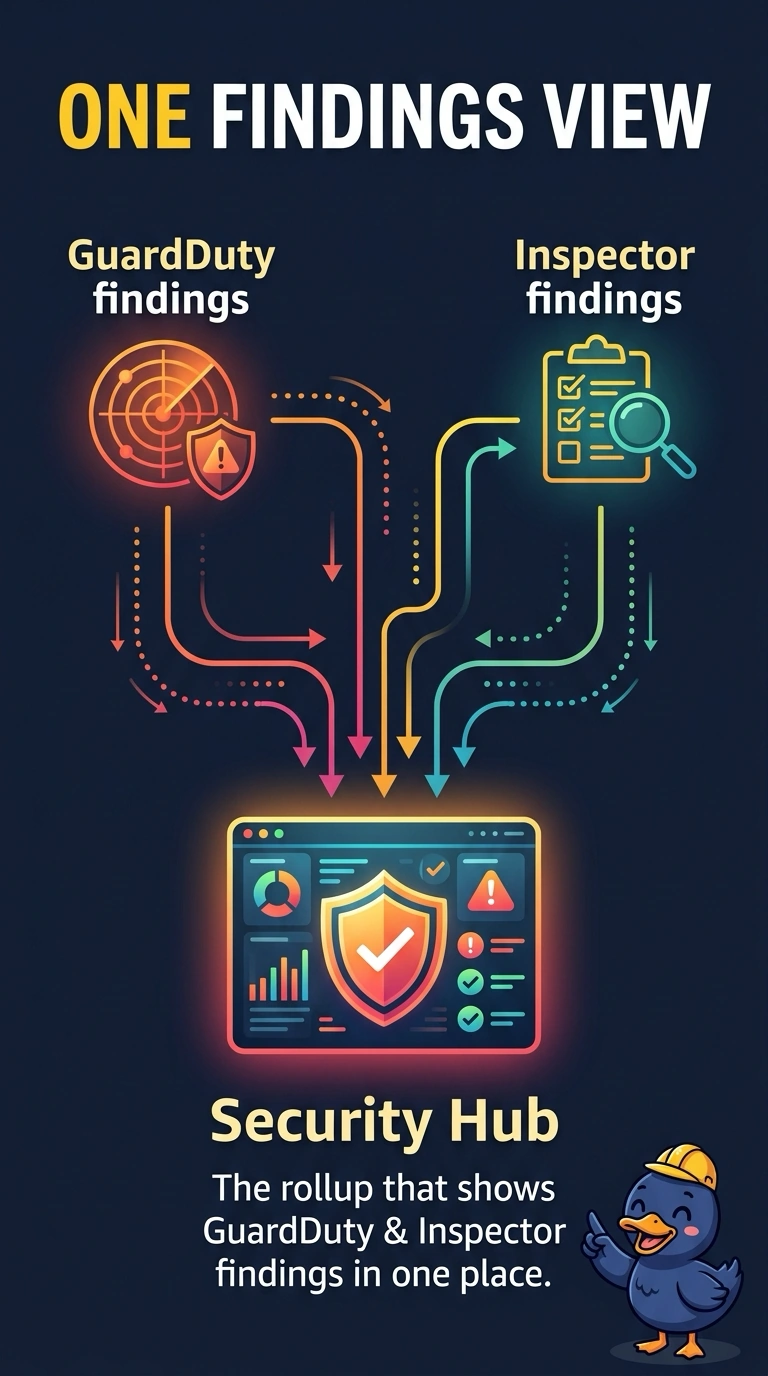
You opened one drawer of a cabinet that has a master index on the door. GuardDuty's console shows GuardDuty findings, not the Inspector findings the review also asked to see beside them. Security Hub is the rollup that holds both once Security Hub is enabled, and CloudTrail event history is an API log rather than that combined view.
Full Explanation
GuardDuty and Inspector produce different findings. GuardDuty reports threat behavior, and Inspector reports vulnerabilities and unintended network exposure. Each product's console shows its own findings. The review asked for both in one place, which is what Security Hub is for: it ingests findings from those products and lists them together. Opening only GuardDuty cannot satisfy that, because GuardDuty does not display Inspector's findings. Turning Inspector off would remove the vulnerability findings the review wants. It does not make them appear inside GuardDuty. CloudTrail event history records API calls. It is not the combined findings list for GuardDuty and Inspector, and reading it does not roll the two products up. Caveat: both GuardDuty and Inspector must themselves be enabled to generate findings, and Security Hub must be enabled in the account and Region; the service integrations are on by default once Security Hub is enabled. Operational check: open Security Hub, filter to this account, and confirm both a GuardDuty finding and an Inspector finding are present for the same review.