
A public certificate requested through the default ACM path shows in the console that it cannot be exported. The team wanted that certificate installed on one EC2 web server. How should TLS for the site be terminated?
Select an answer to reveal the explanation.
Short Explanation
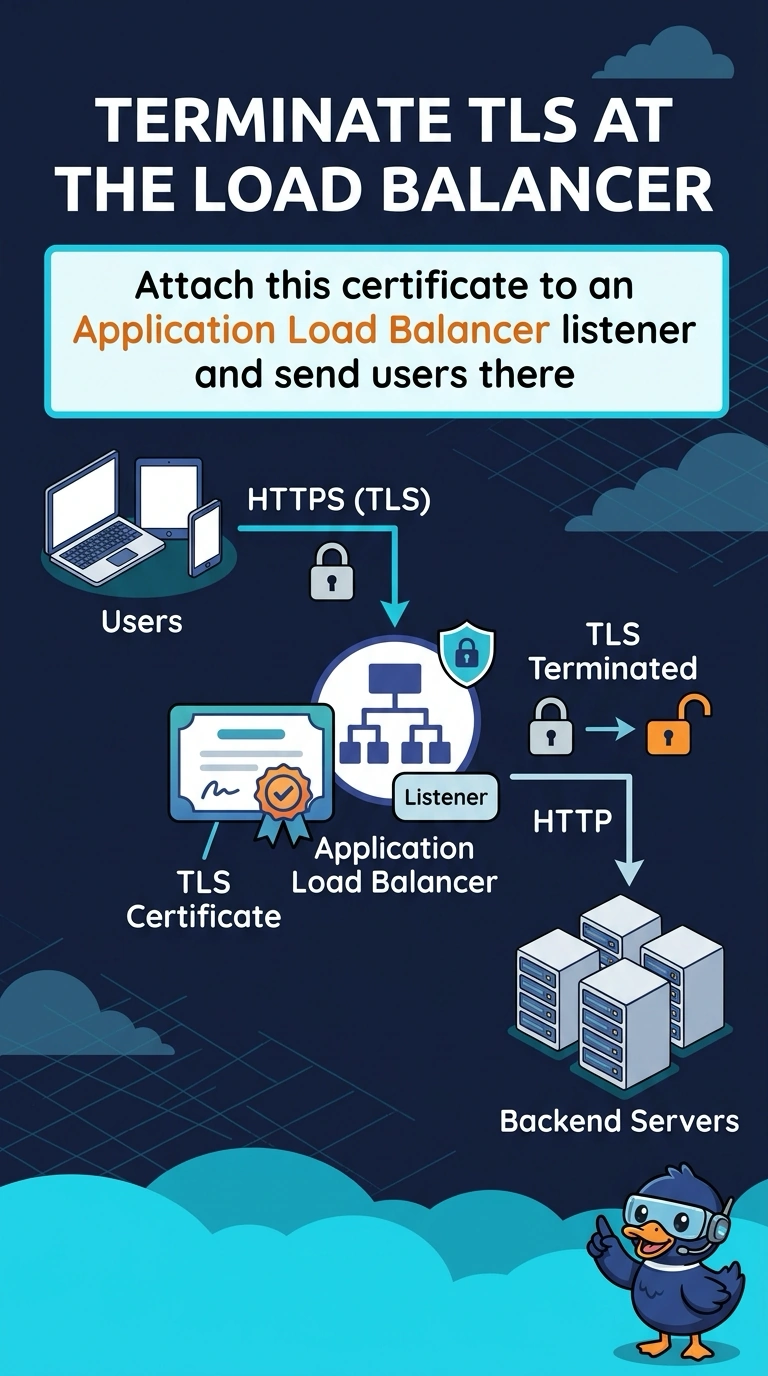
This certificate is a badge the console will not let you carry outside. You terminate TLS on an Application Load Balancer and attach the certificate to your listener. Exporting it onto one instance is the move the console already refuses.
Full Explanation
This certificate was requested on the default ACM public path, and the console shows it cannot be exported. There is no private key to download and install on the single EC2 instance. An Application Load Balancer can use this ACM certificate on an HTTPS listener, which terminates TLS for users without an export. Exporting the certificate and its private key is the action the console already refuses, so that install path is not available for this certificate. The certificate body does not contain the private key. Putting that body in user data cannot recreate a key that stayed inside ACM. IAM does not issue this public certificate and then offer its private key for download. An IAM server certificate is a certificate you upload, and it is a different object. Caveat: some ACM public certificates can be requested so that they are exportable. This certificate's console status says it cannot be exported, so the load balancer is the path for this one. Operational check: attach the certificate to an HTTPS listener, send users to the load balancer, and confirm a browser shows that certificate on the site name.