
IAM Access Analyzer reports that a log bucket policy allows a foreign account to call s3:GetObject. The security team thought the finding was about an expired password. What is the finding actually about?
Select an answer to reveal the explanation.
Short Explanation
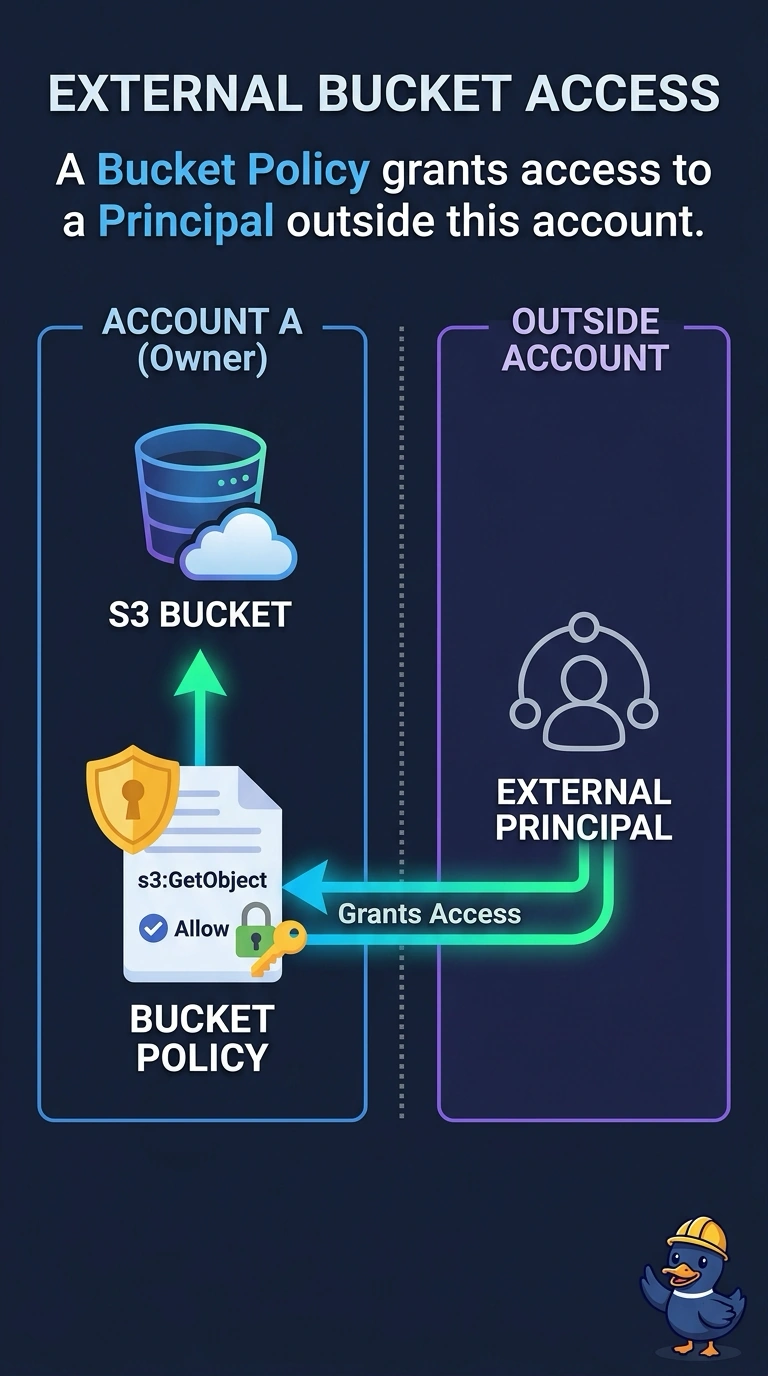
Access Analyzer is waving at a bucket policy that lets another account in. That is external access, not a password. You read the policy it names and take the foreign grant back, because an expired password would not show up as this finding.
Full Explanation
IAM Access Analyzer reviews resource policies for access from outside the zone of trust, such as another account. A bucket policy that allows a foreign principal s3:GetObject is exactly that kind of finding. It is not an IAM password check, a NACL drop, or an alarm state. The remediation is to change or remove that bucket-policy statement if the foreign account should not read the logs. Caveat: a finding can be archived when the external access is intentional, and archiving is not the same as fixing a mistake. Operational check: open the finding, confirm the bucket and the foreign principal, and resolve it only after the policy no longer grants that access or the grant is documented as intended. The finding names the resource, the external principal, and the action. A foreign account principal, or a star principal, is the line to remove or restrict with a condition. Archiving is for access you intend to keep, and it should include why. An expired password would be an IAM credential report, not this analyzer result. After the policy change, a rescan should drop the finding.