
A records bucket should be readable only through one gateway VPC endpoint. The bucket policy allows the application role and has no condition on the endpoint. Calls from the public internet still succeed when the role's keys are used. What should the policy add?
Select an answer to reveal the explanation.
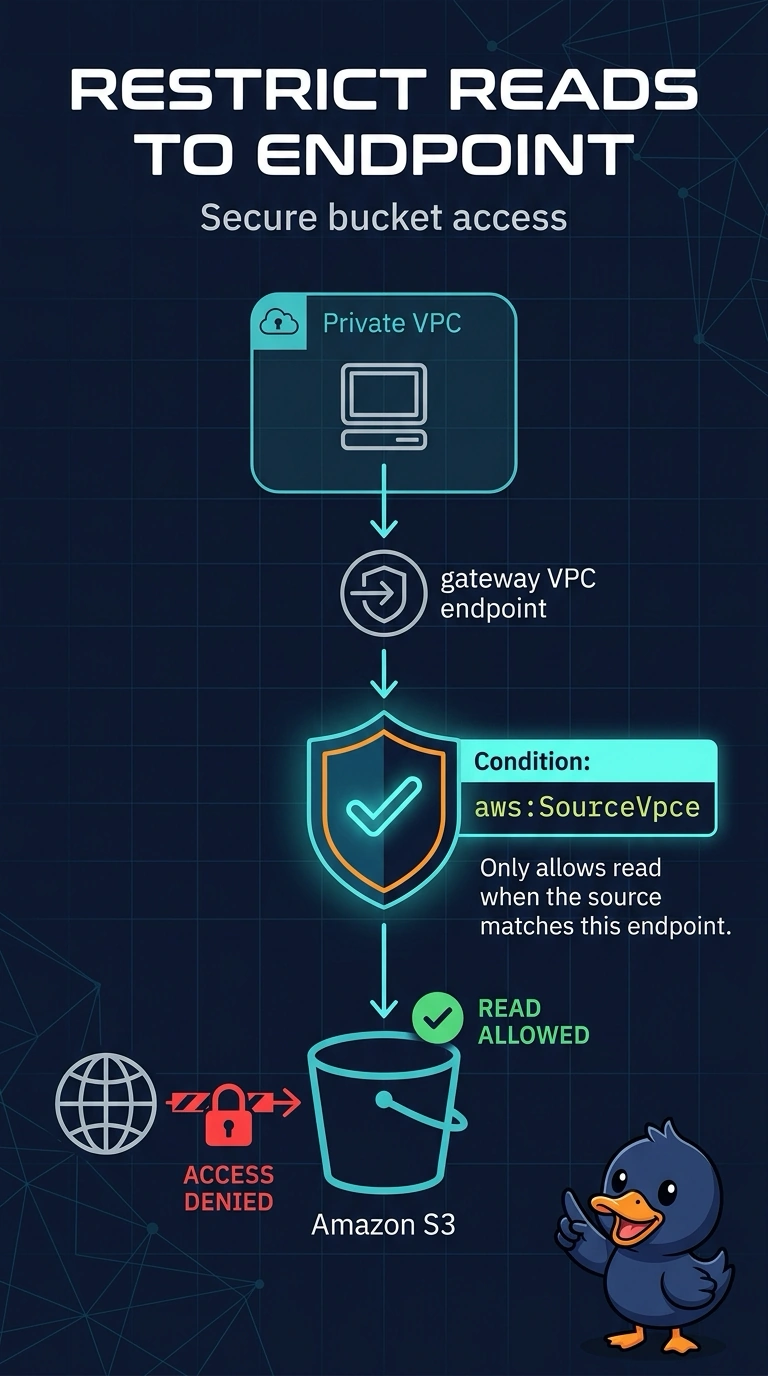
Short Explanation
Your role is allowed to read, but the policy does not require the request to use the gateway endpoint. Add an endpoint condition so the read is allowed only through that endpoint; a public-read ACL cannot enforce this.
Full Explanation
aws:SourceVpce identifies the VPC endpoint that handled the request. Requiring this key to equal your gateway endpoint in the bucket policy allows the application role to read through that endpoint but denies the same role when it calls over the public internet. Requiring a public IP would favor the path you need to block. An object ACL granting AllUsers read would expose the object and cannot limit access by endpoint name. A lifecycle rule expires objects; it does not authorize or restrict requests. Caveat: an explicit Deny for a missing or different aws:SourceVpce is harder to bypass than an Allow that another policy statement might supplement, so prefer a Deny for other sources when the bucket must remain private to the endpoint. You can use StringNotEquals for that Deny, or StringEquals in an Allow that requires your endpoint ID; a Deny is safer when other Allows exist. The endpoint ID has a vpce- prefix, and the gateway ID is not the value for this condition. As a practical check, test a read with the role from a host using the endpoint and from one outside the VPC: the first should succeed and the second should be denied. CloudTrail can show the denial for a call that still uses the public path.