
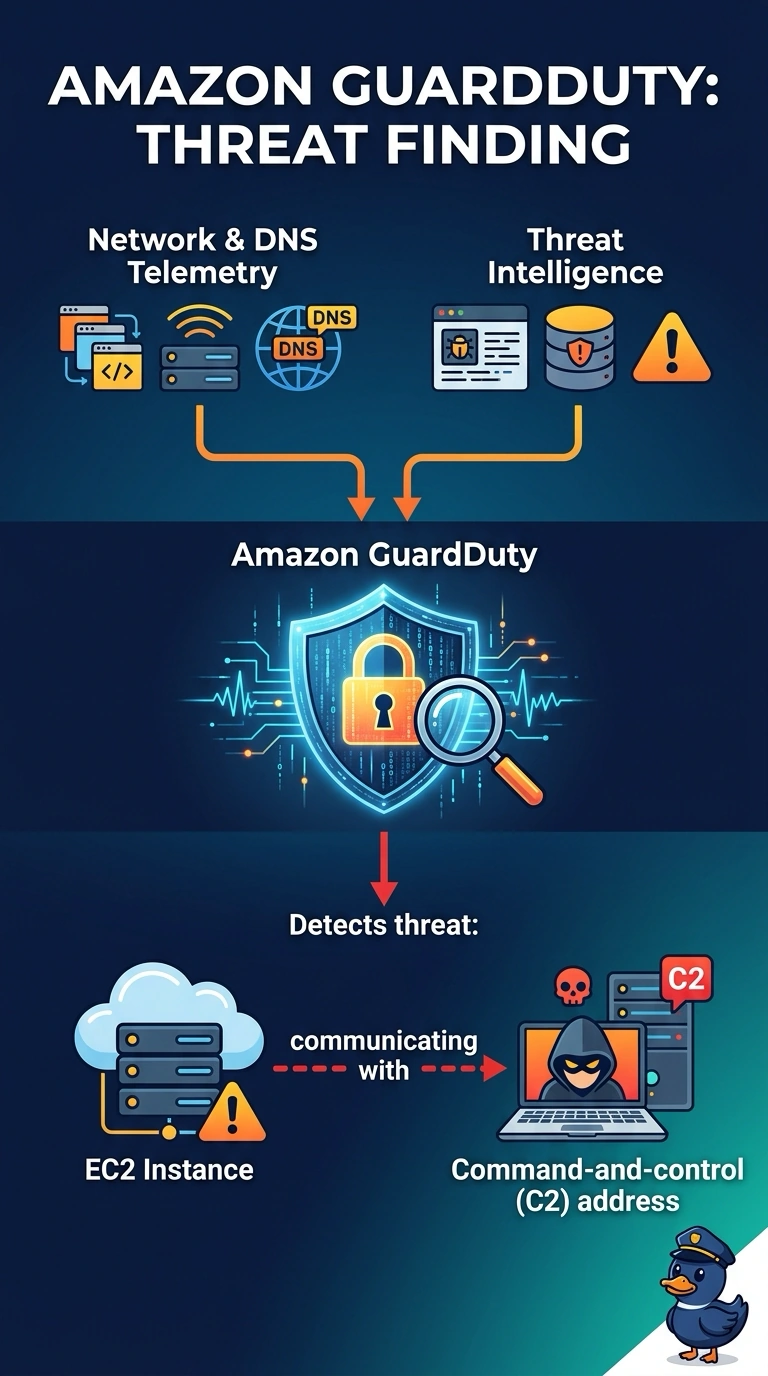
A hospital wants a finding when an EC2 instance communicates with a known command-and-control address. Which service is built to raise that threat finding?
Select an answer to reveal the explanation.
Short Explanation
GuardDuty is the lookout watching who the instance is calling. A known command-and-control address is a threat finding, which is that lookout's job. Inspector tells you the window latch is weak; it does not tell you a call already went to a bad address.
Full Explanation
GuardDuty analyzes VPC Flow Logs, DNS logs, and CloudTrail and raises findings when traffic matches threat intelligence, including command-and-control destinations. That is the signal the hospital asked for. Config continuously compares resource configuration to rules; it does not identify a malicious peer address. Macie looks for sensitive data inside S3, not for live instance traffic. Inspector looks for vulnerabilities and unintended network exposure; a CVE on a package is a different finding from an observed call to a command-and-control host. Caveat: GuardDuty must be enabled in the Region, and its findings describe the behavior rather than patching the instance for you. Operational check: enable GuardDuty in the account and Region, then confirm a sample finding or a real finding appears with the instance as the resource.