
A game studio sees REJECT entries in VPC Flow Logs for clients that never reach an API. An engineer wants the HTTP status code those clients received. What do those REJECT entries show?
Select an answer to reveal the explanation.
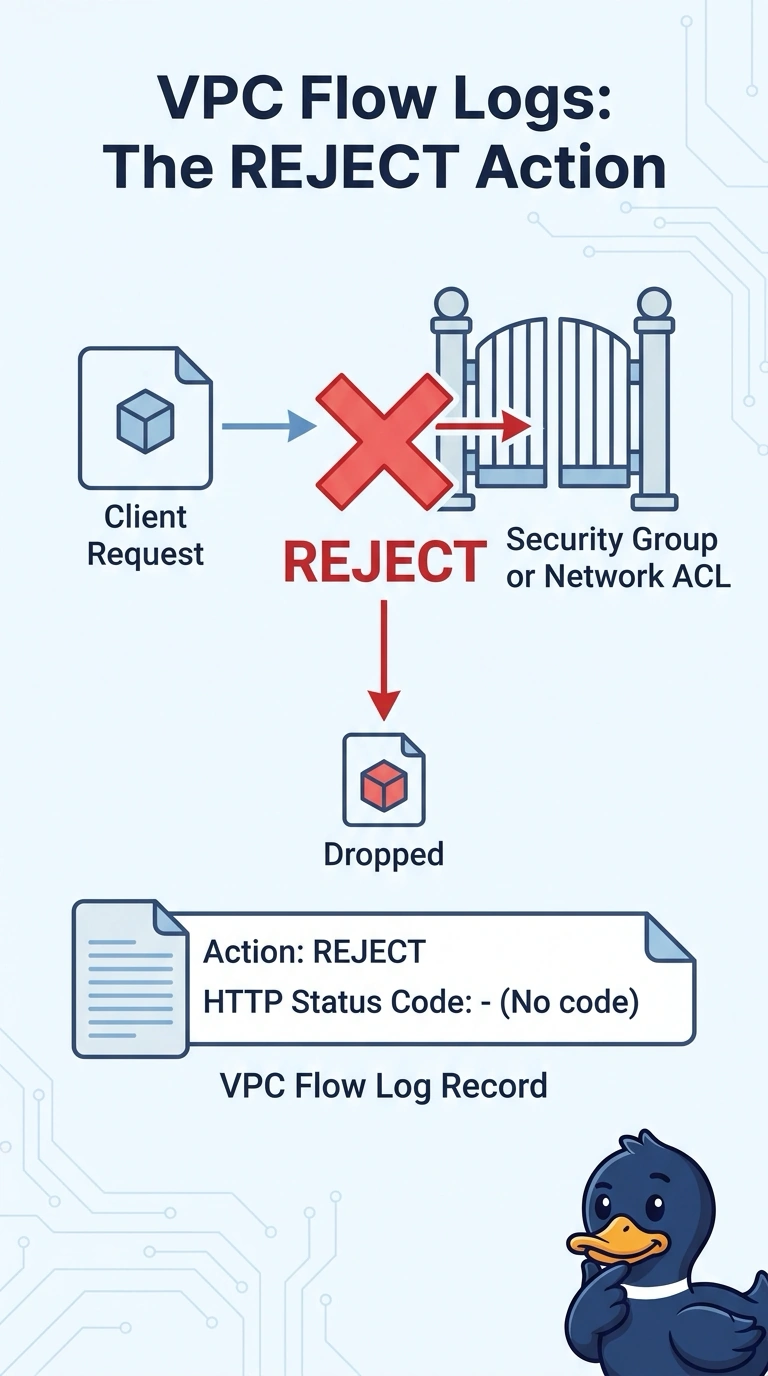
Short Explanation
You can read REJECT as a network drop by a security group or network ACL, not as an HTTP response. That entry has no HTTP status code or reason phrase for you to retrieve.
Full Explanation
VPC Flow Logs describe network traffic and record whether a flow was accepted or rejected; they do not report HTTP responses. A REJECT entry means a security group or network ACL dropped the traffic, so there is no HTTP status code or reason phrase in that record. The option claiming the application returned an HTTP status and reason phrase is wrong because the rejected traffic did not reach an HTTP response. A target status code is recorded by a load balancer for an HTTP request it handled; it is not a field in the flow-log record. A CloudTrail error name describes an AWS API call, not the network rule that rejected this traffic, and it does not identify an HTTP response. Exam caveat: REJECT identifies a rejection but does not distinguish whether a security group or a network ACL caused it. Practical check: compare the flow's addresses and port with the relevant security-group rules and subnet network ACL rules to determine which rule matches; do not expect an HTTP status code in the REJECT entry.