
A logistics security review asks which DNS names instances in a VPC resolved last Tuesday, including names that were blocked. VPC Flow Logs are already on. Where is that name evidence?
Select an answer to reveal the explanation.
Short Explanation
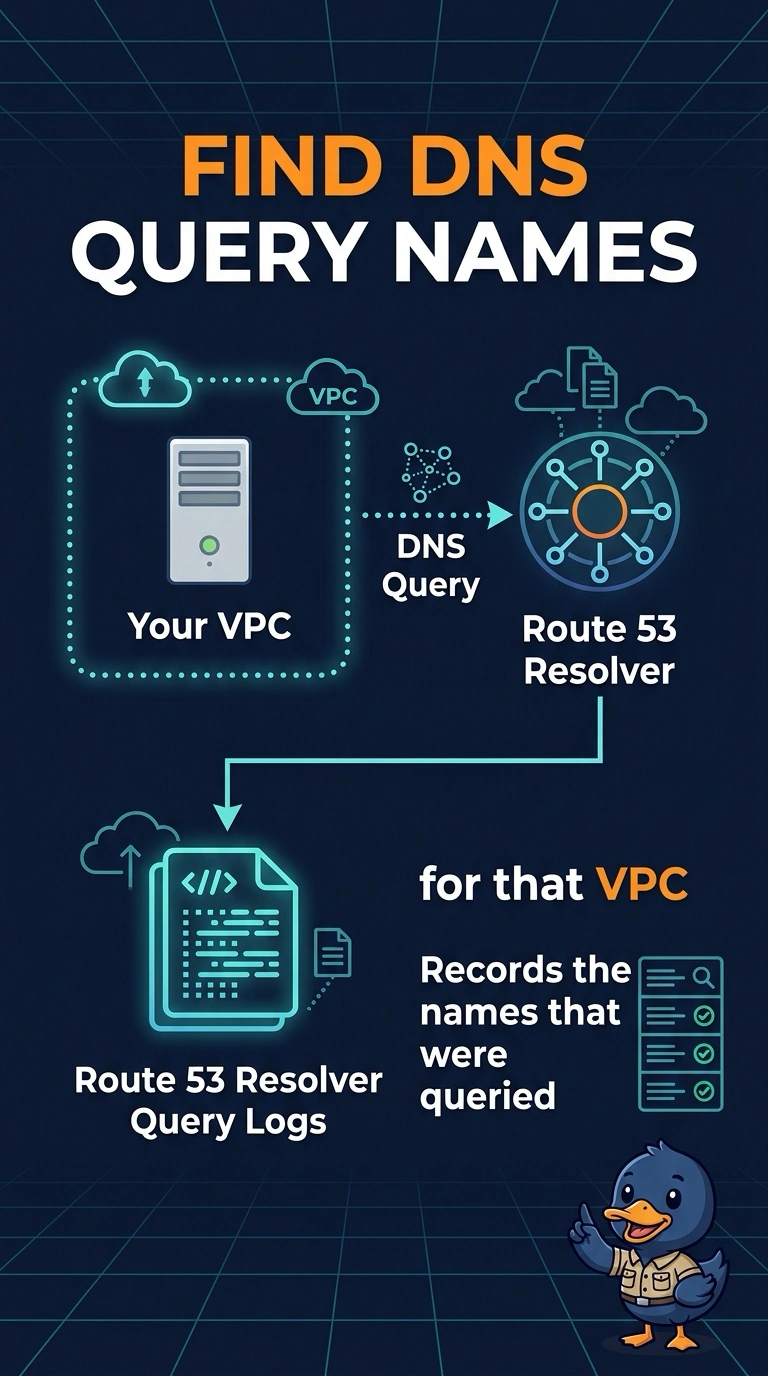
Flow logs are the highway cameras, and they never write down the question the driver asked DNS. You want Resolver query logs, which record the names the VPC asked Route 53 Resolver to resolve. The flow record can show an address and a port, not the name that was looked up.
Full Explanation
Route 53 Resolver query logging writes the DNS queries that instances send to the VPC Resolver, including the name, the response code, and whether a rule handled the query. That is the evidence for last Tuesday's lookups, including names a DNS Firewall rule blocked before any connection existed. VPC Flow Logs record network flows: addresses, ports, protocol, and whether the flow was accepted or rejected. They do not contain the DNS query name. CloudTrail data events record data-plane API calls you have enabled, such as object-level S3 calls. Guest DNS lookups are not EC2 data events. Load balancer access logs record HTTP requests that arrived at that load balancer. Instances resolving names on their own never appear there. Caveat: query logging starts when you turn it on, so Tuesday is visible only if logging was already enabled then. Operational check: query the log group for one known instance address and one known name, and confirm the log line shows that name and the answer code.