
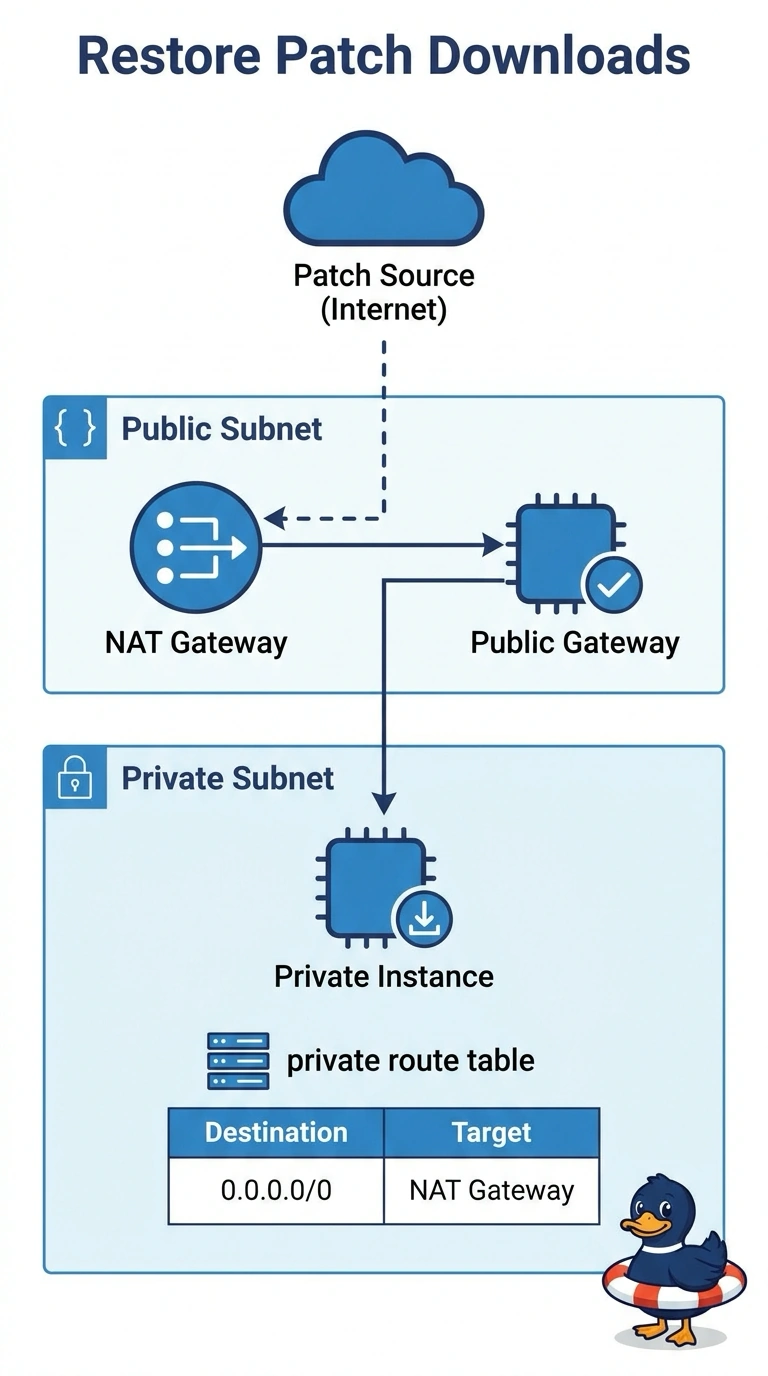
A factory's private-subnet instances cannot download patches. Their route table has no route for 0.0.0.0/0. A NAT gateway is already up in a public subnet whose route table sends 0.0.0.0/0 to an internet gateway. What should the operator add first?
Select an answer to reveal the explanation.
Short Explanation
The NAT gateway is the door to the street, and the private subnet never got a hallway to that door. You add a default route that targets the NAT gateway. A second internet gateway is not something you hang on a private subnet.
Full Explanation
Private instances reach the internet through a NAT gateway, and only if their route table sends 0.0.0.0/0 to that gateway. The NAT gateway is already in a public subnet that has a route to an internet gateway, so the missing piece is the private subnet's route. An internet gateway attaches to the VPC, once, and a route to it from a private subnet would require public addressing the stem is not using; you do not attach it to a subnet. An inbound rule for port 80 does not create outbound patch downloads. A VPC cannot be peered to itself, and peering would not provide internet egress. Caveat: the instances also need outbound security group rules and a NACL that allows the return ephemeral ports, but the stem's missing default route is the first break. Operational check: after the route is in place, confirm a private instance resolves and reaches a patch host, and confirm the NAT gateway still has its own default route to the internet gateway.