
Operators must see a CloudWatch dashboard of the production fleet. They must not be able to edit the dashboard or administer the account. What should they be given?
Select an answer to reveal the explanation.
Short Explanation
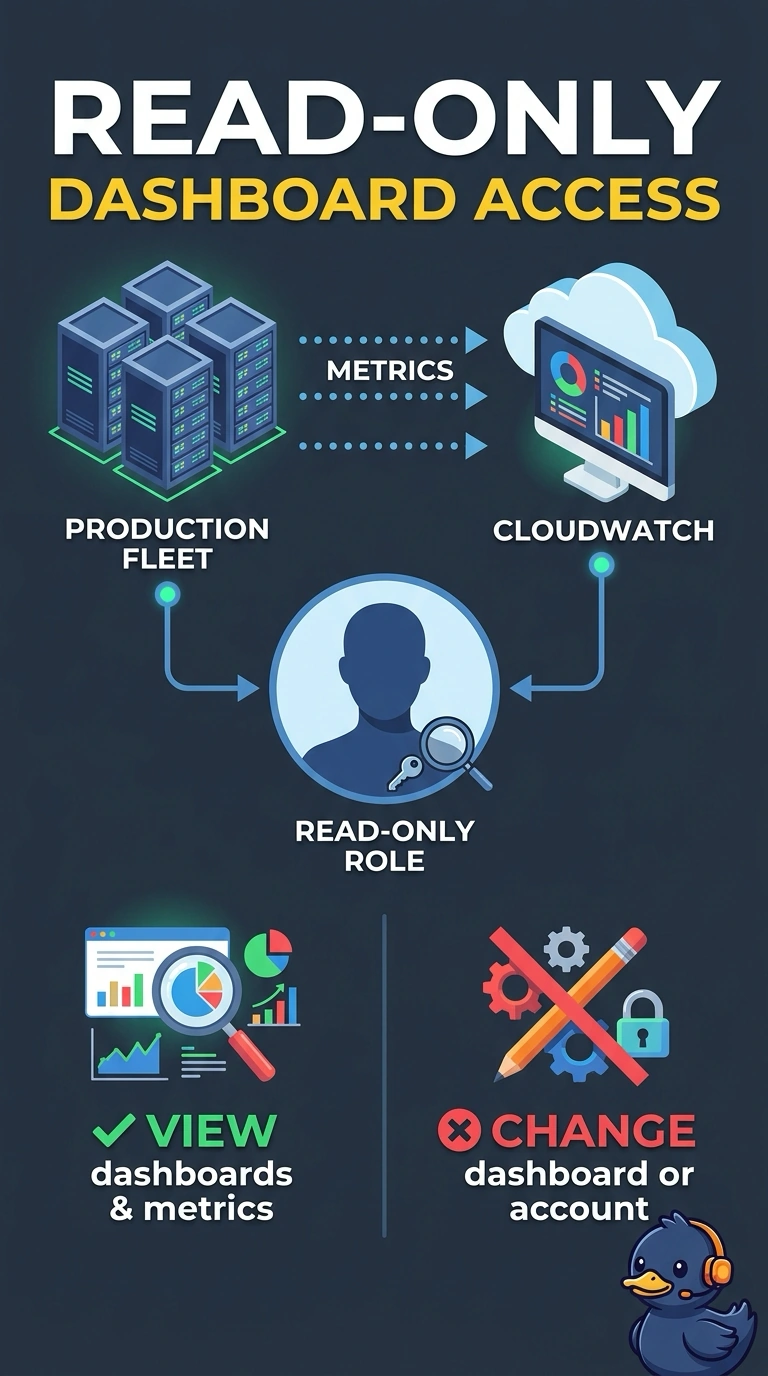
Looking at a board is not the same as owning the building. You give the operators permission to read the dashboard and the metrics on it. AdministratorAccess and the root password are the keys to the building, which is what you were told not to hand out.
Full Explanation
IAM can allow cloudwatch:GetDashboard, ListDashboards, and the read calls for the metrics on the widgets without allowing PutDashboard, DeleteDashboards, or account administration. That matches view-only operators. AdministratorAccess can view the dashboard and can also change everything else. The root password is not an operator credential. Permission to delete without permission to view is the reverse of the request. Caveat: a dashboard that uses a metric math expression or Logs Insights also needs the read actions for those sources, or the widgets render empty for an otherwise correct role. Operational check: sign in as an operator, open the dashboard, and confirm a save or delete is denied. A small identity policy with the CloudWatch read actions is enough. Include GetMetricData and the logs read actions if the widgets use Logs Insights. Deny or simply omit PutDashboard and IAM administration. The operator test is: the dashboard opens, the graphs have data, and an attempt to save the dashboard is denied. Root and AdministratorAccess both fail that test by being far too strong.