
An auditor asks a city for every s3:GetObject against a records bucket last week. The trail logs management events only. Lookups for those object reads return nothing. What should be enabled?
Select an answer to reveal the explanation.
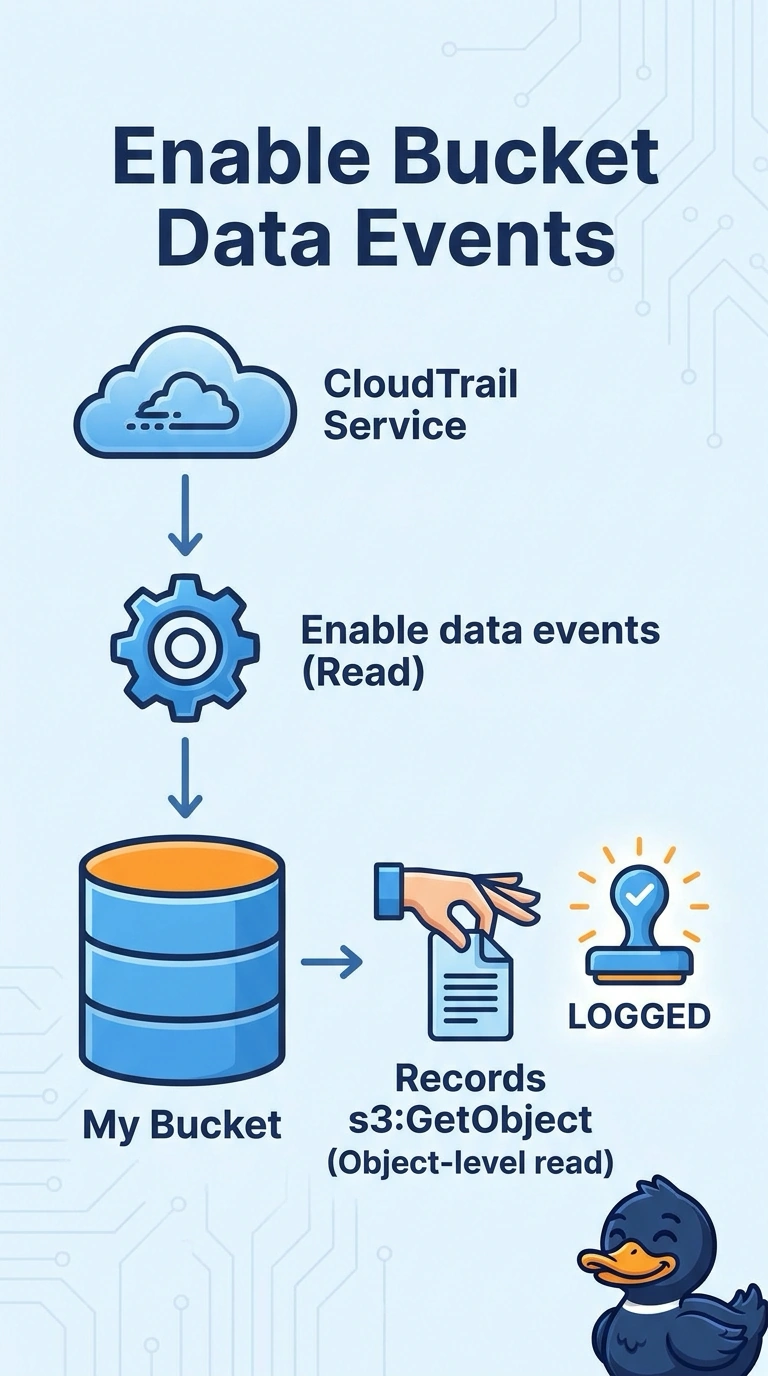
Short Explanation
Management events are the lobby sign-in sheet. Reading an object is a data event, and that sheet never had a line for it. You turn on data events for the bucket, and a flow log will not grow an API name just because you wish it would.
Full Explanation
CloudTrail management events cover control-plane calls such as creating a bucket. Object-level s3:GetObject is a data event and is not logged until data events are enabled for that bucket or for S3. That is why the auditor's lookup is empty. Detailed monitoring changes EC2 metric periods and does not list S3 API calls. A size alarm watches bytes stored, not who read them. VPC Flow Logs record network tuples, not the GetObject event name or the principal. Caveat: data events are high volume; scope them to this bucket and the read event rather than every data event in the account if the audit is this narrow. Operational check: after data events are on, perform a test read and find that event in the trail with the principal and the object key. Data events are configured on the trail, with a selector for the bucket ARN and for read, write, or both. A test GetObject from a known role should then appear with that role in userIdentity and the key in requestParameters. Management events stay on for bucket-level changes such as PutBucketPolicy; they are not a substitute for this selector.