
A research lab's inventory lists a compiler package that the build standard does not allow. The team wants the service that produced that package list. Which service is it?
Select an answer to reveal the explanation.
Short Explanation
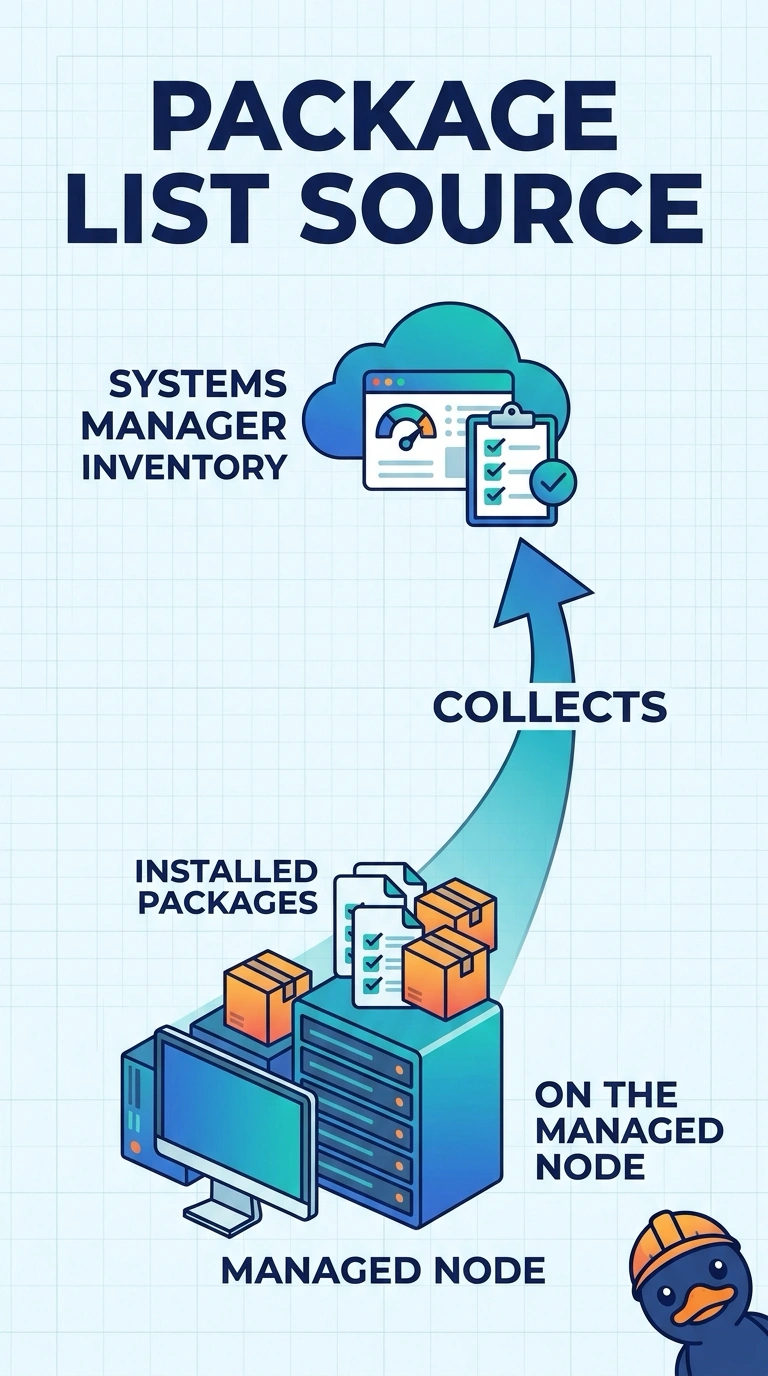
The shelf list in the stockroom is an inventory, not a burglar alarm. You are looking at Systems Manager Inventory, which collected the packages on the managed node. GuardDuty would be a threat finding, and it does not catalog an unexpected compiler.
Full Explanation
Systems Manager Inventory collects configuration data from managed nodes, including the applications and packages installed on them. An unexpected compiler in that list is inventory data, not a threat finding. GuardDuty reports suspicious behavior such as malicious API calls or dangerous network activity. It does not raise a finding for each package that is absent from a build standard. CloudTrail data events record data-plane API calls you have enabled. Installing a package inside the guest is not stored as a package-name field on those events. VPC Flow Logs record network tuples and an accept or reject action. They have no field for installed software. If the inventory collection for installed applications is not enabled, the compiler can be on the instance and still missing from this list. Caveat: Inventory only includes nodes the agent can report, and the application inventory has to be part of what that account collects. Operational check: open Inventory for the instance, find the compiler in the application list, and confirm GuardDuty has no finding that names that package.