
A hospital's CloudFormation stack is stuck rolling back because it cannot delete a security group that is still attached to a network interface an operator created outside the stack. What should the operator do?
Select an answer to reveal the explanation.
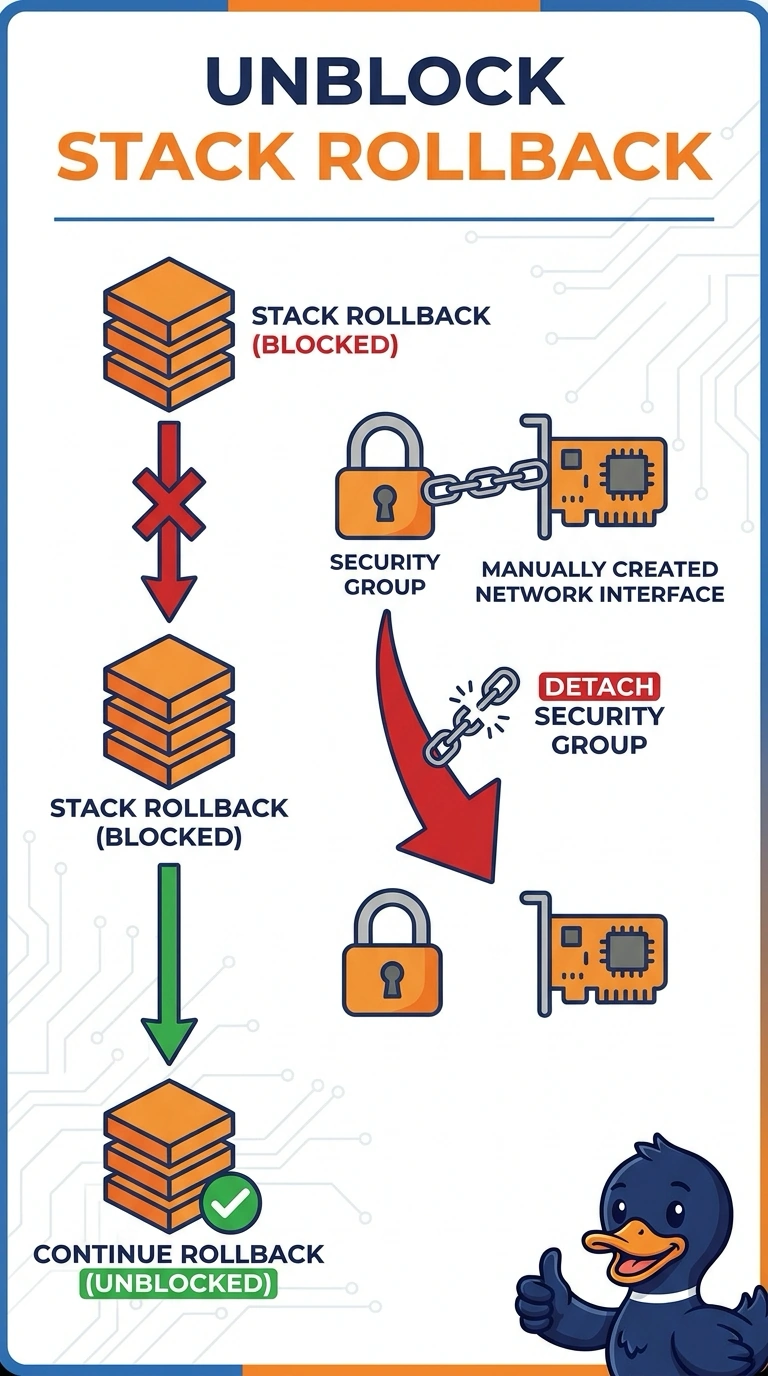
Short Explanation
You can clear the rollback blocker by detaching the security group from the network interface created outside the stack, so CloudFormation can delete it and continue. Deleting VPC route tables, changing termination protection or using the organization management account, or creating a second stack with a renamed group will not release that outside attachment.
Full Explanation
CloudFormation cannot delete a security group while a network interface still lists it, including an interface created outside the stack. Detach the security group from that interface, then continue the rollback so CloudFormation can remove the group; if the interface is no longer needed, deleting it also removes the attachment. Deleting VPC route tables does not clear this security-group dependency and could black-hole the rest of the VPC. Turning off termination protection only removes a stack-deletion safeguard, while deleting from the organization management account does not detach an interface in a member account. Launching a second stack to import the instance and recreate the group under a new name leaves the original group attached to the outside interface, so the failed rollback remains stuck. Caveat: a requester-managed interface must be released by its owning service, and a forced delete will fail if AWS still reports the interface as in use. Practical check: confirm the interface no longer references the security group, then watch the stack event to verify that the group leaves the failed rollback state.