
A CloudFormation stack fails while creating an instance. The event says the deployer is not authorized to perform ec2:RunInstances. A teammate wants to pick a smaller AMI first. What should be fixed?
Select an answer to reveal the explanation.
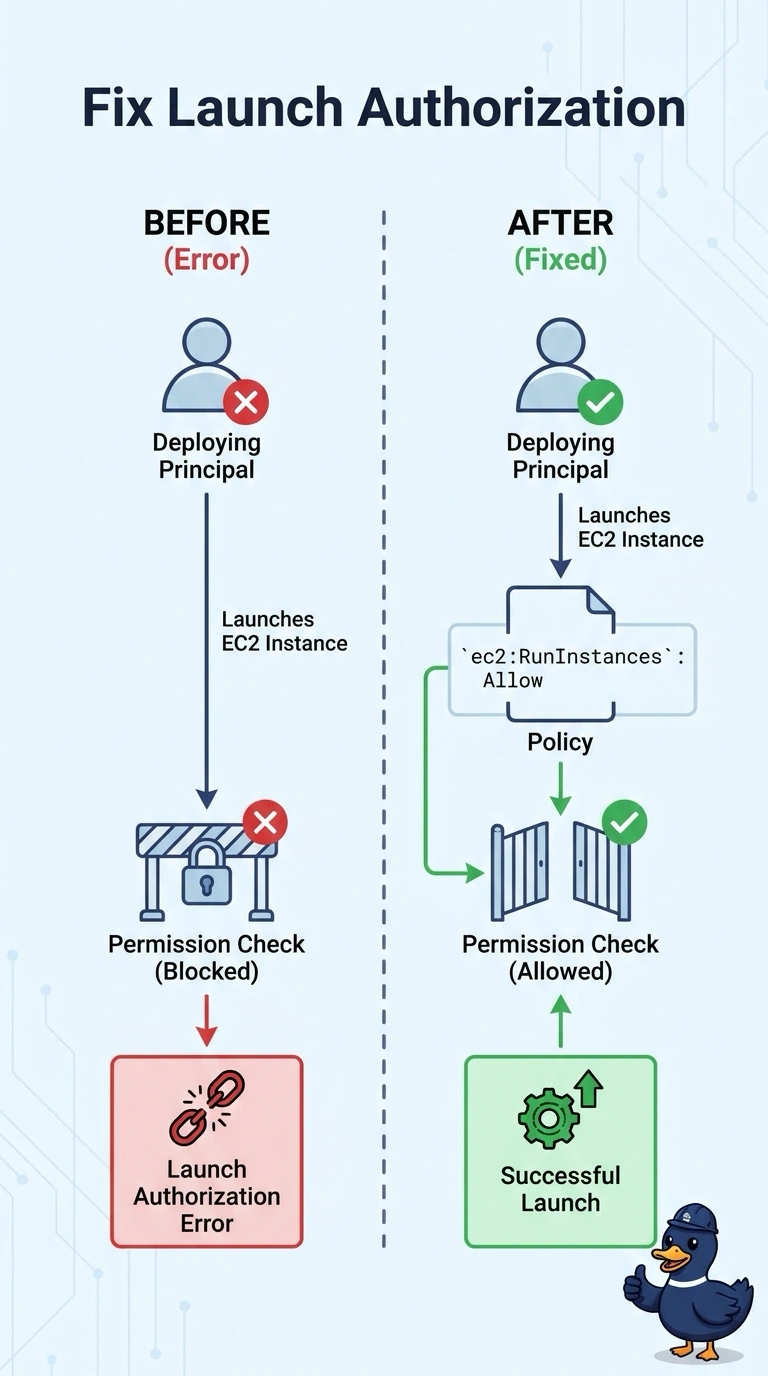
Short Explanation
Unauthorized means the deployer is not allowed to launch, not that the image needs a diet. You grant ec2:RunInstances to that principal, within the boundary and the SCPs. Swapping the AMI does not answer an authorization error.
Full Explanation
The status reason names ec2:RunInstances and an authorization failure. The identity policy, permission boundary, or an SCP is denying the deployer. Fix that permission and retry. The AMI's size is unrelated to UnauthorizedOperation. RunInstances is an EC2 API, not a route-table lookup. S3 versioning does not gate instance launches. Caveat: if an SCP in the organization denies ec2:RunInstances, an allow in the member account will not win; the deny has to be lifted there. Operational check: the simulator should allow ec2:RunInstances for the deployer, and the stack event should get past the instance resource. Read the encoded authorization message or the simulator to see whether the identity policy, the boundary, or an SCP produced the deny. Add only ec2:RunInstances and the related volume and network-interface permissions the launch actually needs. A smaller AMI fails the same way. When the simulator allows the call, update the stack and expect the instance event to move past CREATE_FAILED.