
A parent CloudFormation stack shows the nested stack resource as failed and nothing else useful. The workload that broke is defined in the nested stack. Where is the resource error?
Select an answer to reveal the explanation.
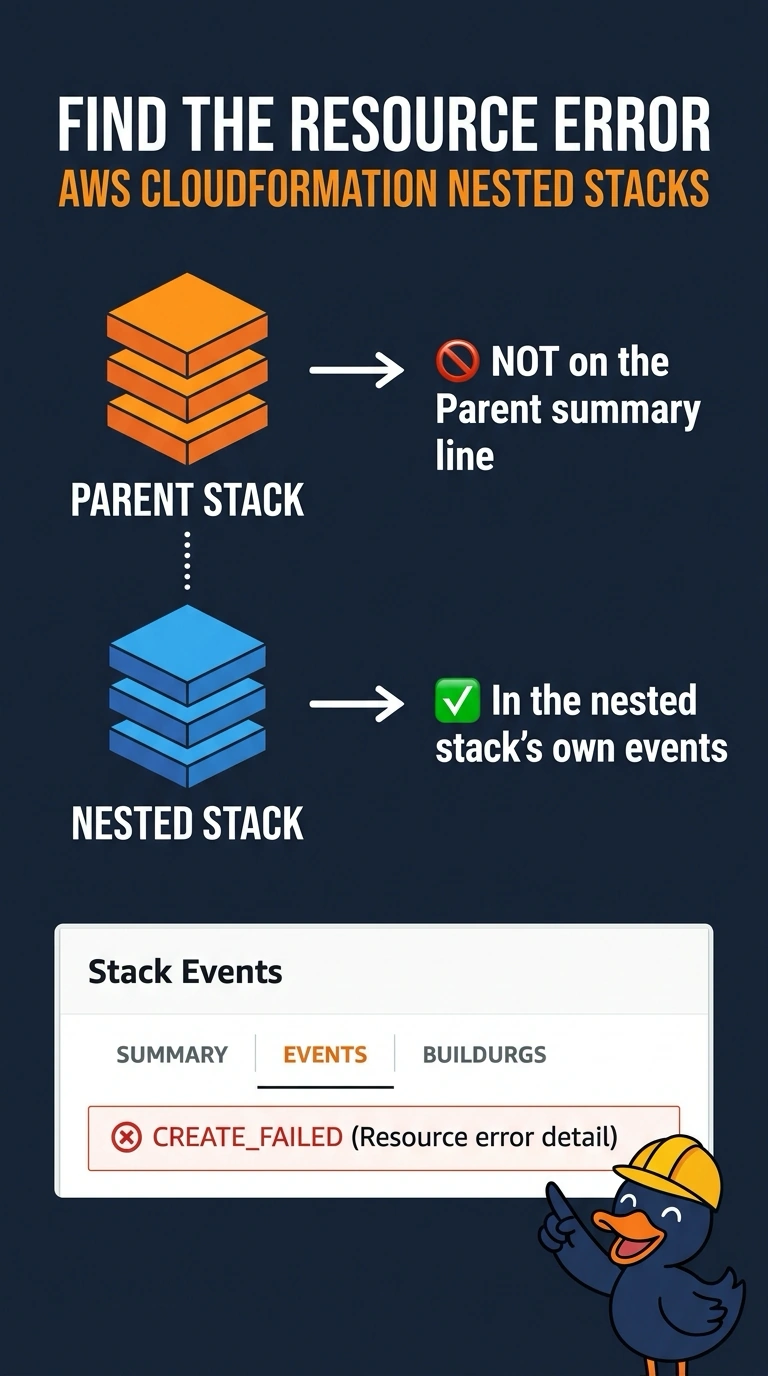
Short Explanation
The parent stack only knows that the nested stack stumbled. You open the nested stack and read its events, the way you would open the inner box instead of staring at the shipping label. The label will never grow the real error.
Full Explanation
A nested stack is its own stack. The parent event usually says the nested stack failed and stops there. The status reason for the security group, the role, or the bucket is on the nested stack's events. The parent template description is not rewritten with that error. The AMI catalog and a DNS query log do not record stack failures. Caveat: if several nested stacks failed, open each one that the parent marks failed; the first one in the parent's events is the place to start. Operational check: from the parent event, follow the nested stack id and read the earliest CREATE_FAILED or UPDATE_FAILED there. The parent resource is AWS::CloudFormation::Stack, and its status reason is often just the nested stack ARN and the word failed. Copy that ARN into the console or the describe-stack-events call. Fix the nested template or the nested parameters, then update the parent so it retries the nested stack. Editing only the parent description does not push a corrected nested template. Open every nested stack the parent marks failed, starting with the earliest one.