
Employees assigned an IAM Identity Center permission set receive Unexpected SSO failures after a scope change, while direct IAM users still sign in successfully. The team must pinpoint whether the failure is federation, permission set, or directory sync. Which troubleshooting sequence should the engineer follow to isolate the authentication failure?
Select an answer to reveal the explanation.
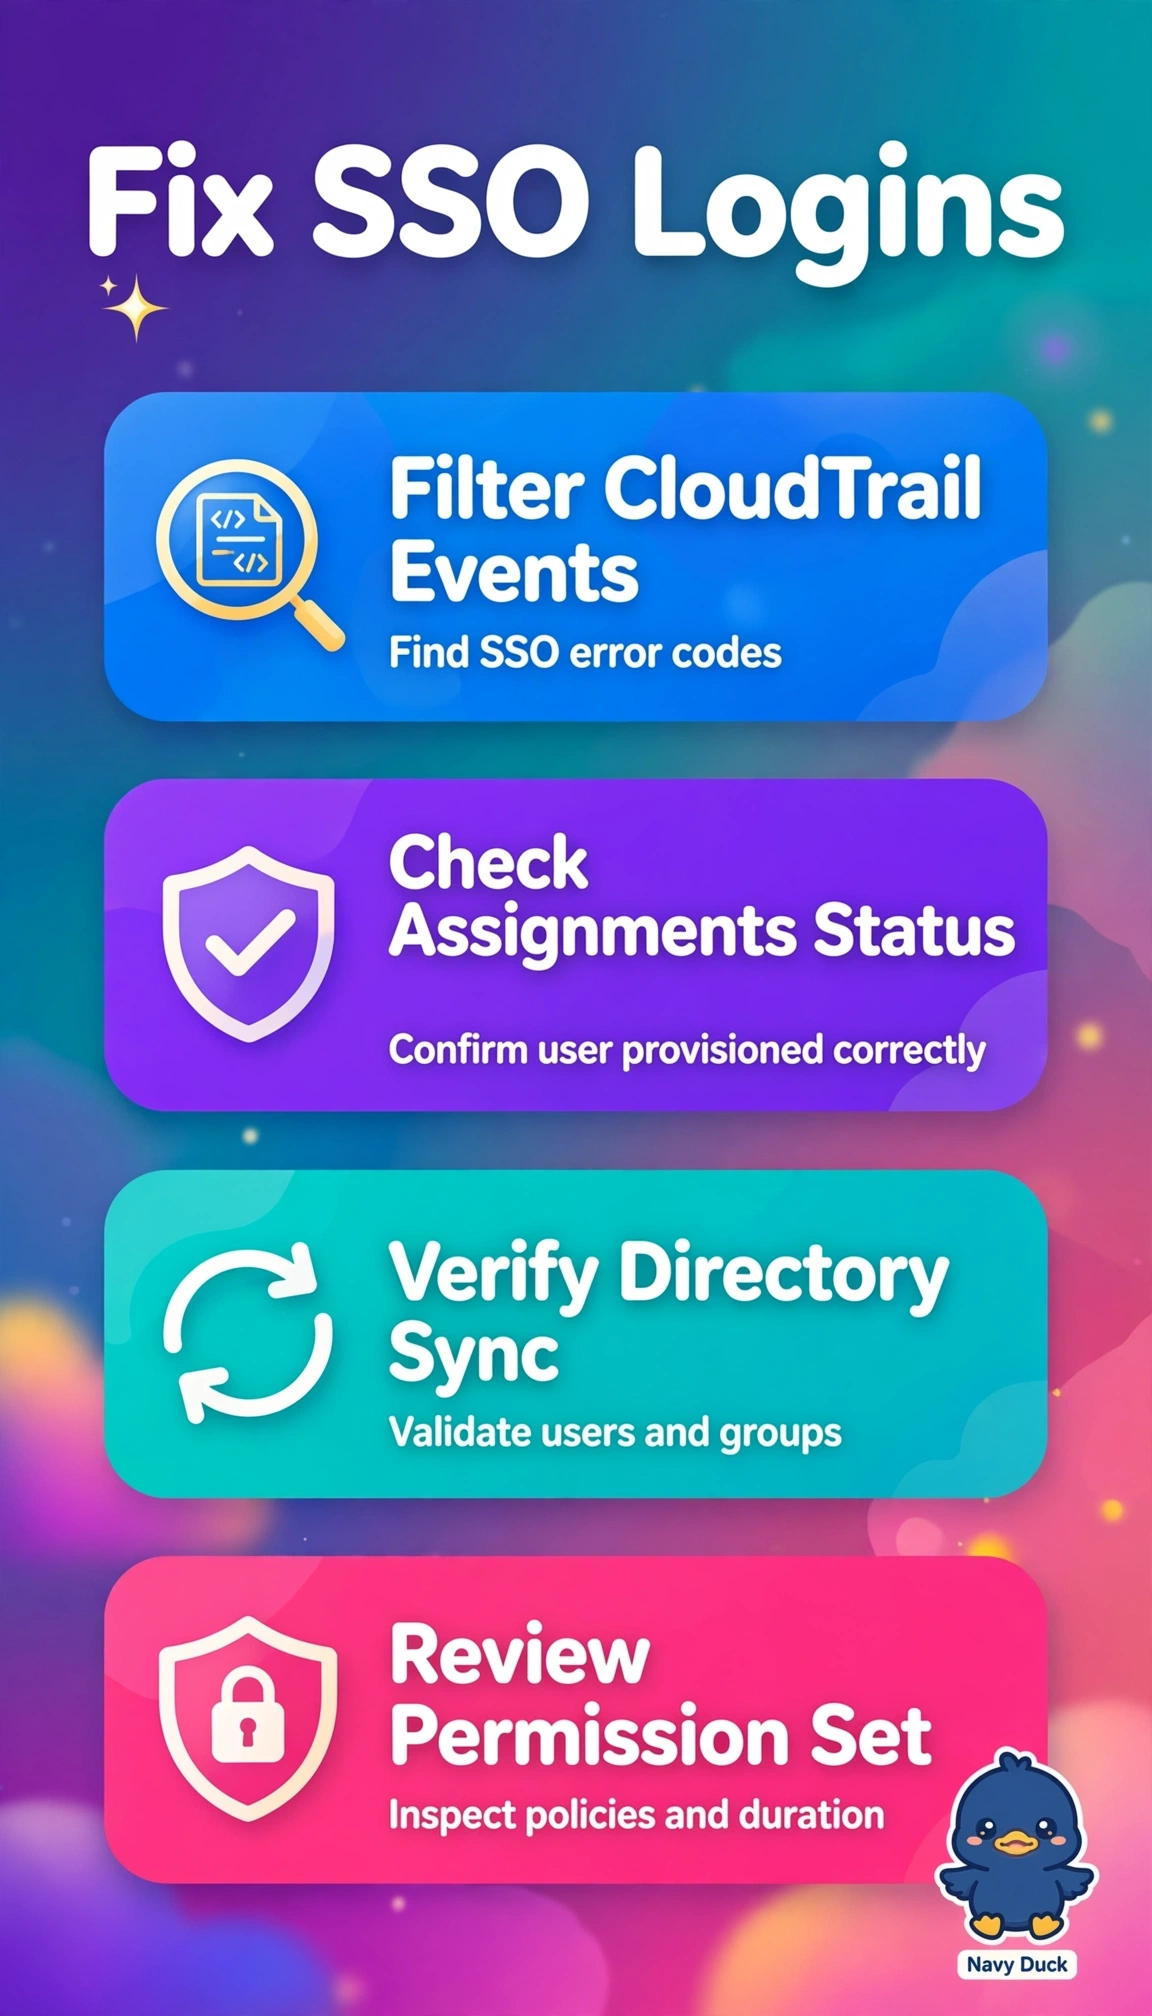
Short Explanation
Login errors hide in the handshake details. Correlation lets you trace the SSO trail from click to directory to permission.
Full Explanation
The correct sequence succeeds because continued direct IAM user logins prove IAM itself is healthy, leaving federation, provisioning, and directory as the fault domains, and correlating CloudTrail SSO events with assignment logs while verifying Directory Service sync and permission set policies tests each domain distinctly with CloudTrail revealing SAML and token failures, assignment logs revealing undelivered permission sets after the scope change, sync status revealing missing users or groups, and policy review revealing over-scoped denies. The delivery-focused sequence examining assignment status, sync health, and inline policies fails conceptually because absent CloudTrail authentication evidence it cannot separate IdP federation errors from authorization denies. The event-plus-sync sequence examining CloudTrail, sync health, and permission policies fails conceptually because absent assignment delivery logs it cannot detect successful authentication that never provisions to the account. The error-plus-assignment sequence examining CloudTrail errors, assignment logs, and certificate validity fails conceptually because absent directory sync validation it misattributes removed group membership from the narrowed scope to SAML trust. As an exam caveat, scope changes typically break group membership and provisioning before certificates expire, so prioritize sync and assignment evidence over certificate checks. As a practical check, verify last Directory sync time, confirm the user remains in scope, filter CloudTrail for SSO failures, and confirm the assignment appears in the target account.