
A university portal uses Amazon Cognito user pools federated to on-premises Active Directory for student logins. After an AD trust change, students report invalid-token and refresh failures, helpdesk sees Cognito authentication errors but no clear cause, and admins changed app client settings recently. Directory sync appears stale. Which troubleshooting sequence should the engineer follow to diagnose the federated authentication failures?
Select an answer to reveal the explanation.
Short Explanation
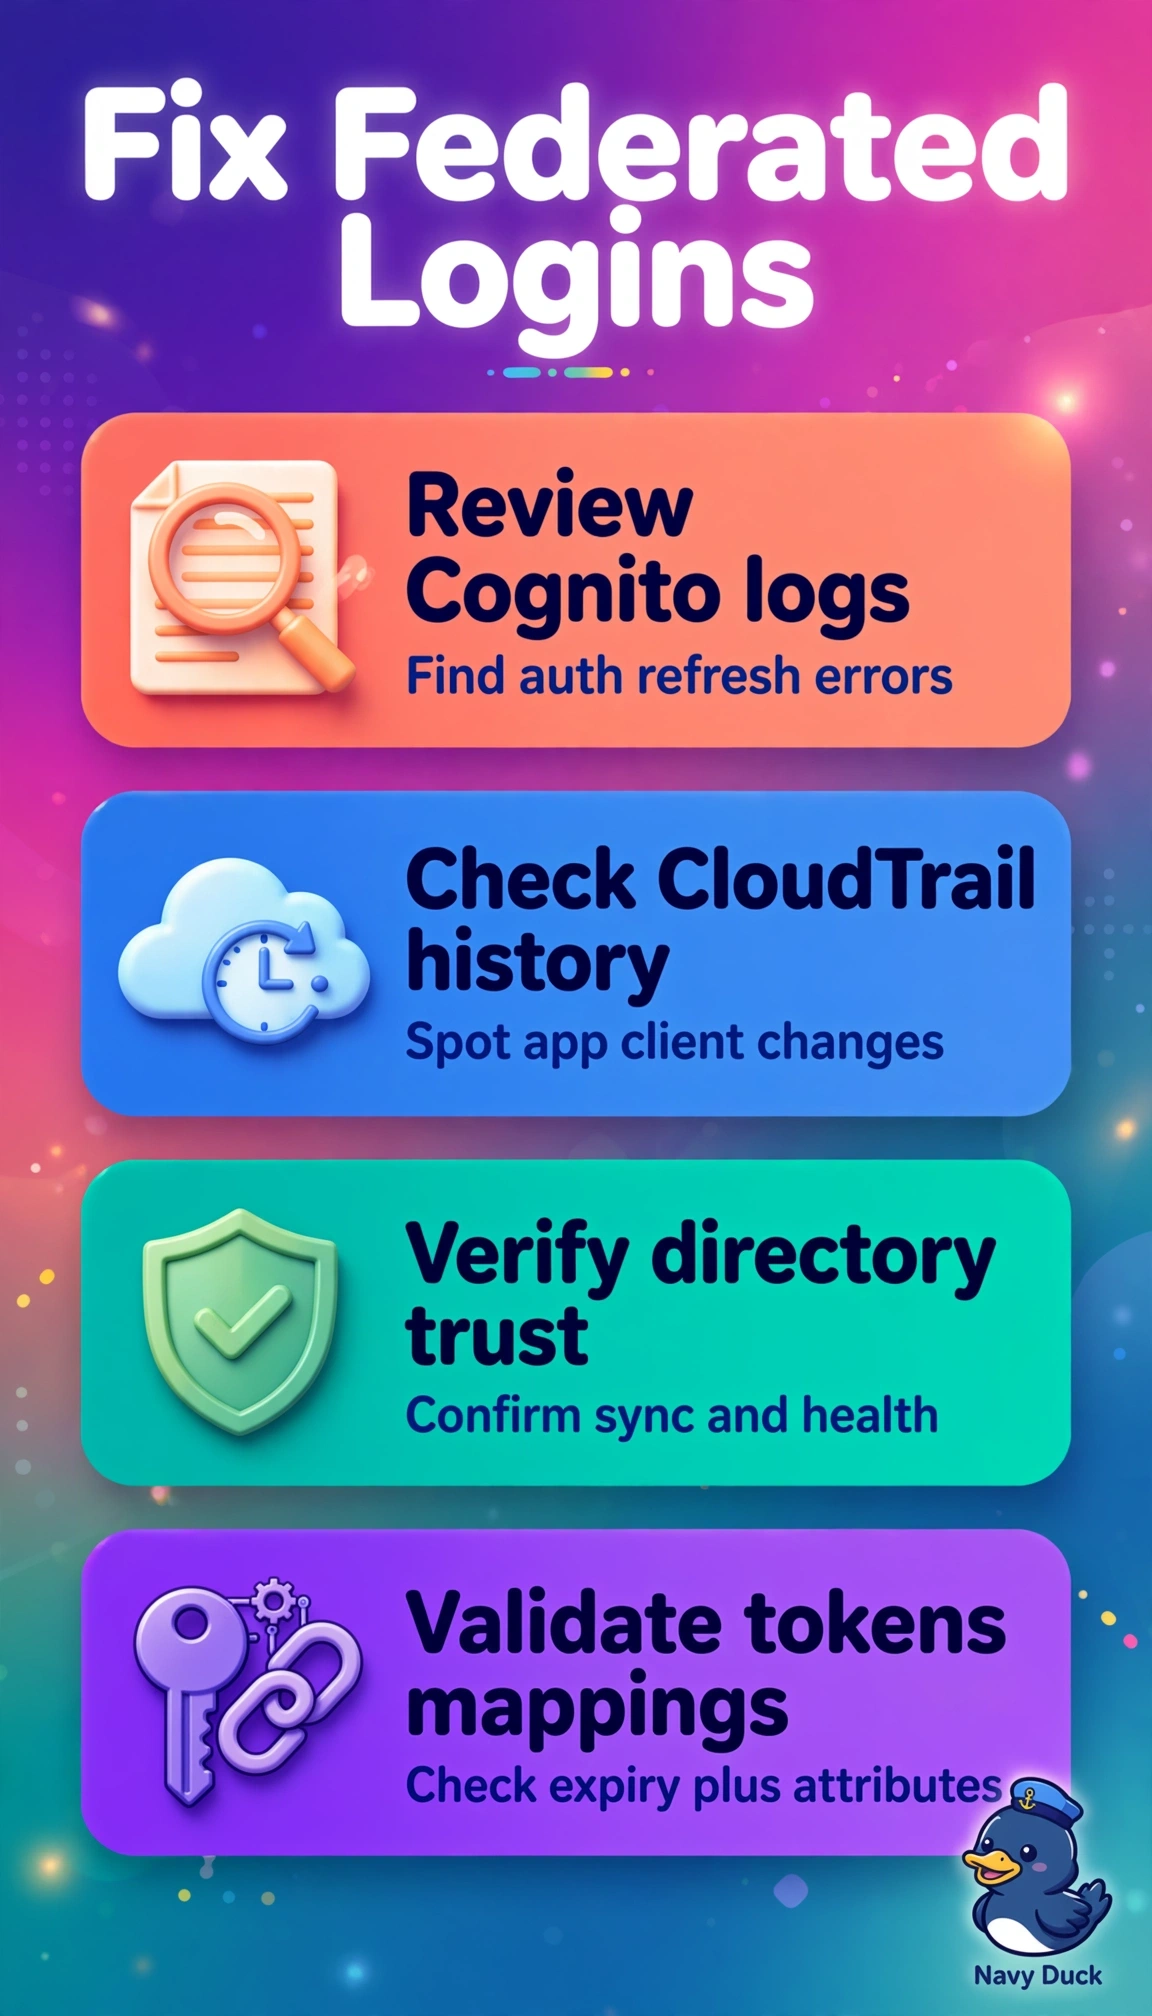
Good troubleshooting follows evidence before fixes. You trace CloudTrail config changes and Cognito errors, then confirm directory trust and mappings.
Full Explanation
Correct troubleshooting must correlate identity and config planes before remediation: Cognito logs pinpoint invalid-token and refresh error patterns, CloudTrail isolates recent app-client changes, verifying the federation trust between the user pool and the AD identity provider (SAML or OIDC metadata and signing certificates) addresses the AD trust change, and checking token expiry plus attribute mapping accounts for stale sync and portal expectations. The distractor analyzing logs, app-client history, trust and token lifetimes fails on identity mapping because healthy trust and valid lifetimes still yield rejected tokens when AD attributes no longer map to required Cognito claims. The distractor correlating logs with trust, sync, expiry and mapping fails on change management because without CloudTrail it cannot detect the admin app-client edit that is a stated suspect and may fix directory health while leaving misconfiguration active. The distractor linking logs, app-client changes and trust to mappings and sync fails on token lifecycle because invalid-token and refresh failures directly implicate expiry, clock skew and revoked grants that mapping resync alone cannot resolve. On exams, avoid assuming directory resync or token lifetime tuning alone fixes federation when both IdP trust and relying-party configuration changed. Practically, verify the IdP trust, metadata and signing certificate, query CloudTrail for UpdateUserPoolClient events in the incident window, and decode a failing token to confirm issuer, exp and student attributes.