
A bank with 60 AWS accounts in Organizations must retain all management events for 7 years, prevent member admins from disabling logging, and centralize trails in a dedicated log archive account with KMS encryption. Auditors will verify completeness across regions. Which CloudTrail design should the team configure to ensure tamper-resistant organization coverage?
Select an answer to reveal the explanation.
Short Explanation
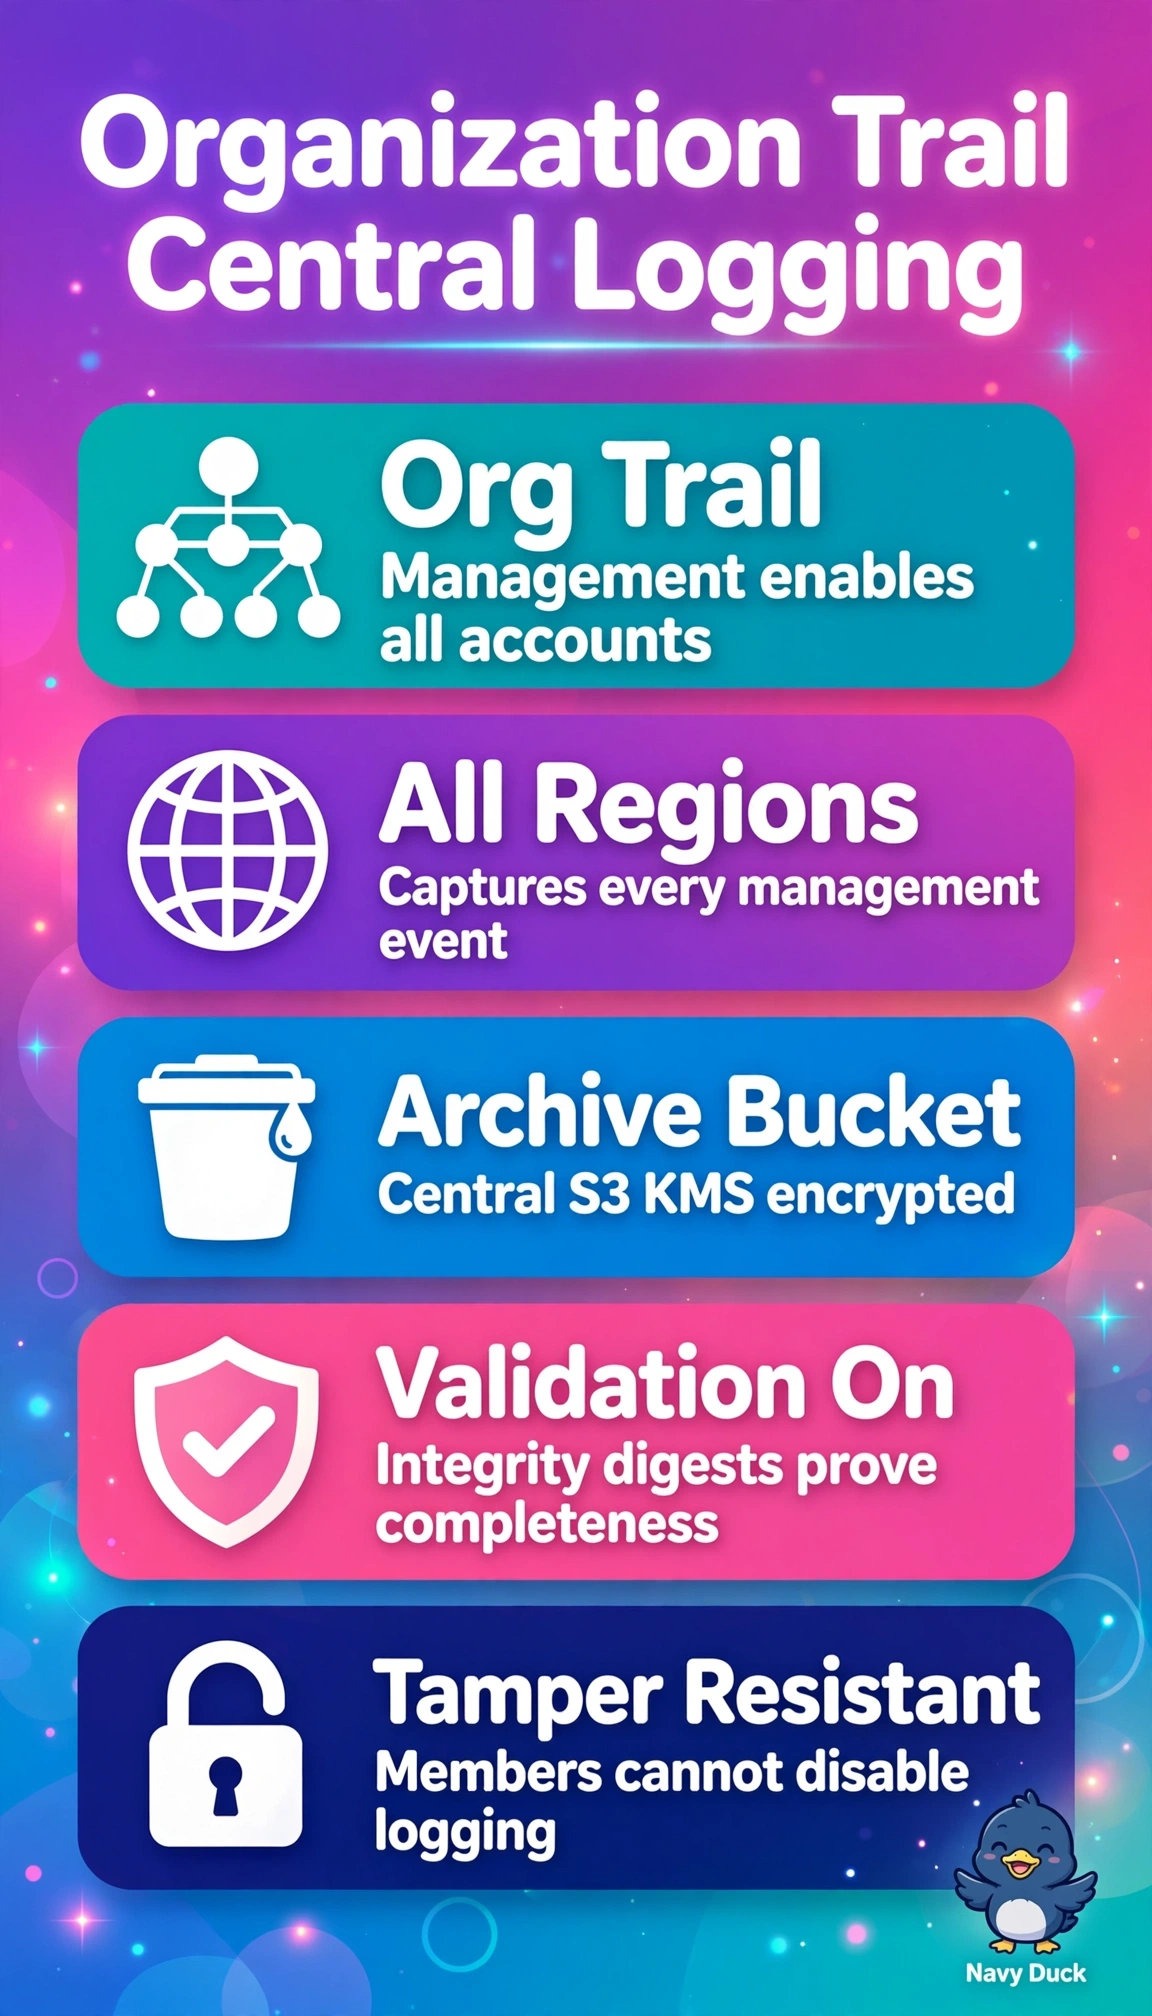
You'll get tamper-proof coverage like a security camera you can't unplug. Set up your organization trail as multi-Region from the management account with KMS encryption and log file validation into your archive bucket.
Full Explanation
The correct design works because an organization trail created in the management account automatically applies to all current and future accounts, captures management events in all Regions, and delivers to one bucket in the log archive account encrypted with KMS, while log file validation produces signed digests that prove no files were altered or omitted, satisfying centralization, tamper resistance, and auditor verification for seven-year retention with S3 lifecycle rules. The single home-Region organization design fails coverage by recording only one Region, so activity elsewhere is invisible to auditors despite proper archiving, encryption, and validation. The account-level trail design fails governance because each member account owns its trail and a member administrator can still stop or modify logging even when delivery is centralized with KMS and validation, whereas only an organization trail removes that local control. The multi-Region organization design without validation fails assurance because without digest files there is no cryptographic proof of completeness, which auditors require for regulated financial data. On the exam, distinguish logging scope from logging protection, since multi-Region, organization enforcement, KMS encryption, and validation are independent settings that must all be present here. In practice confirm the trail status as organization-enabled and multi-Region, check the archive bucket policy and KMS key allow CloudTrail writes, verify digest files arrive, and validate lifecycle archiving meets the seven-year requirement.