
A healthcare SaaS has 800 employees using Microsoft Entra ID and 50,000 patients needing self-registration with MFA and social login for a mobile app backed by API Gateway. Both groups need audited access without long-lived credentials in code. Which identity architecture should the engineer establish to separate workforce and customer authentication?
Select an answer to reveal the explanation.
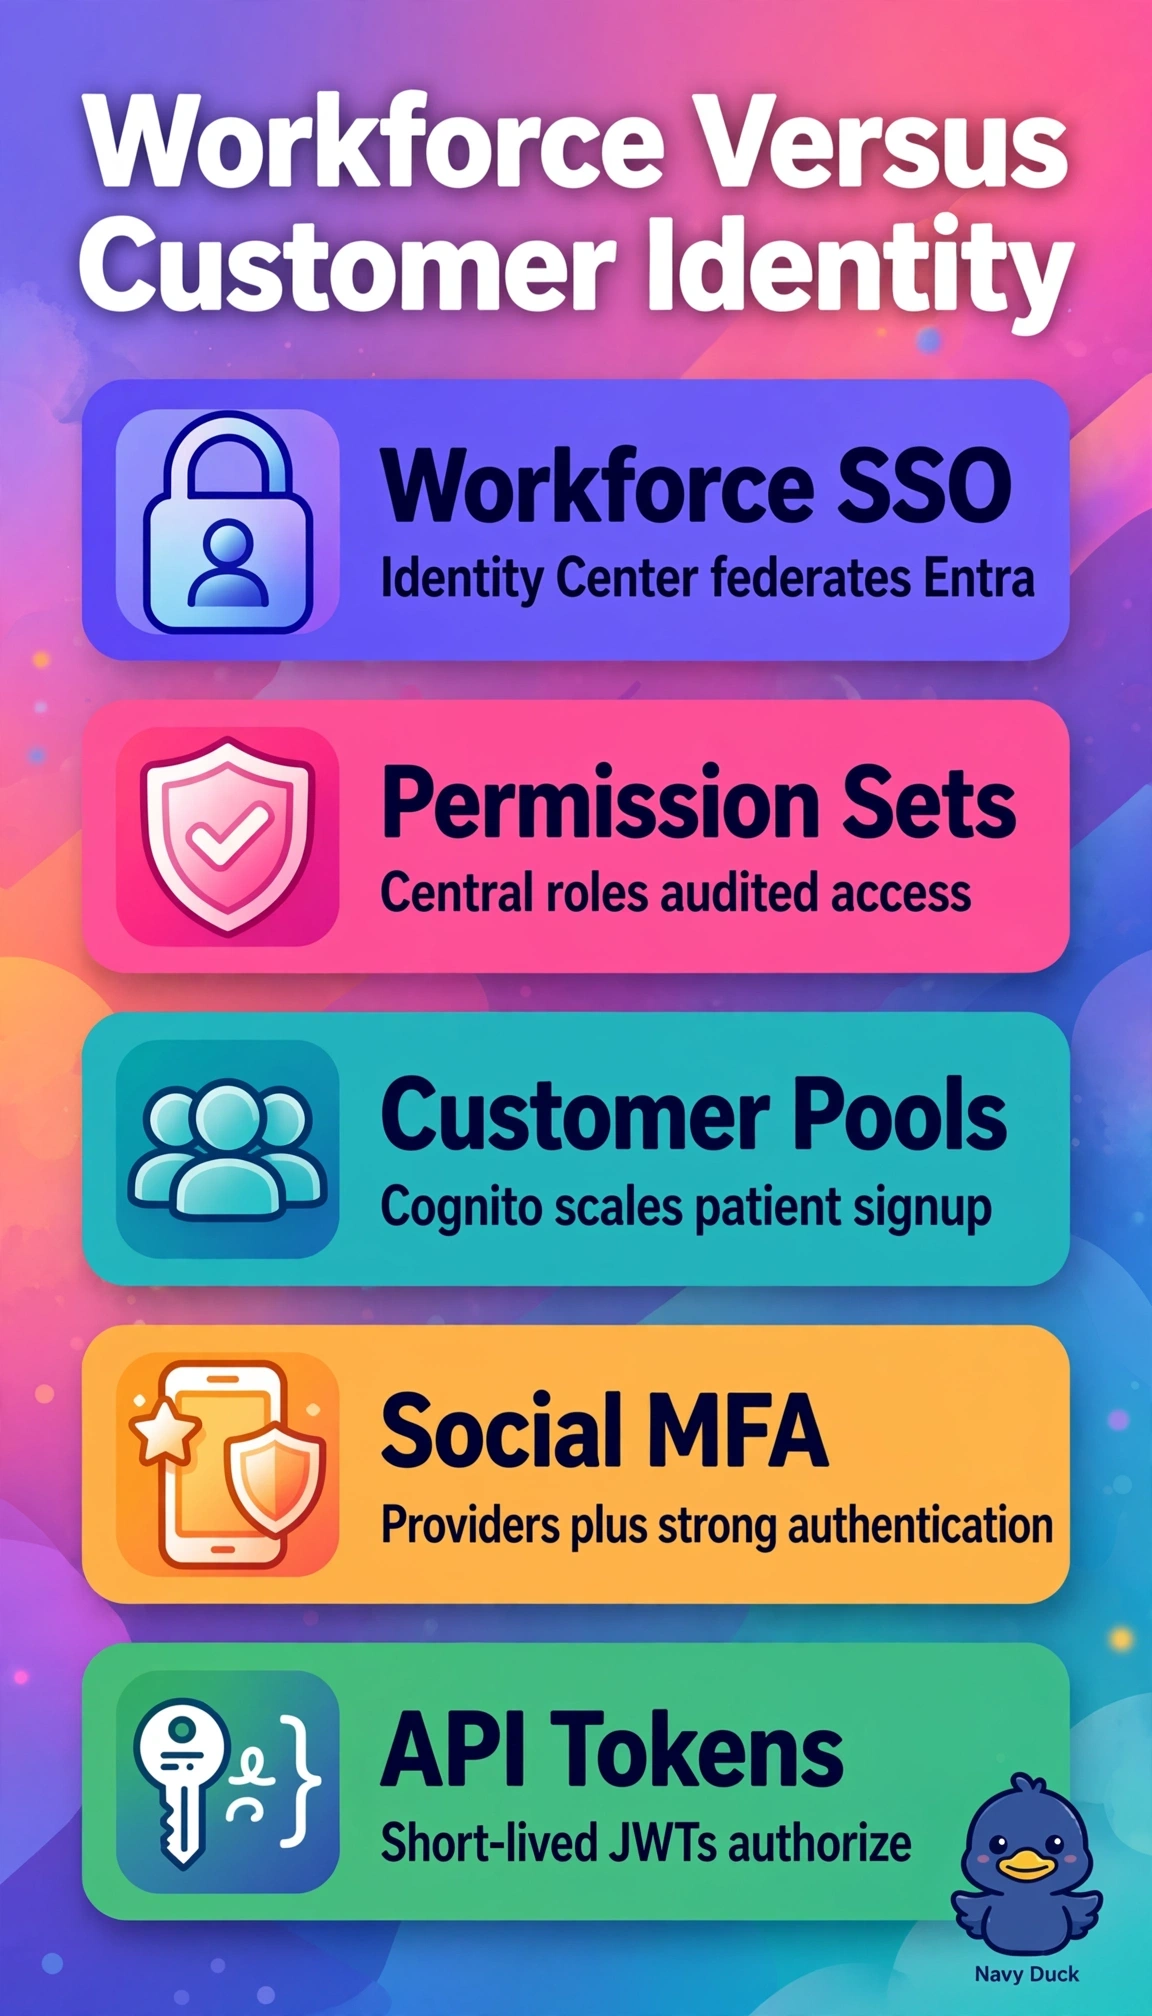
Short Explanation
Workforce and customers live in different identity worlds, so split them cleanly. Cognito handles patient scale, MFA, and social login beautifully. Identity Center gives your staff federated single sign-on with full audit trails.
Full Explanation
The correct architecture separates planes because IAM Identity Center federated to Microsoft Entra ID gives 800 employees short-lived, CloudTrail-audited access to AWS accounts and roles without IAM users or embedded keys, while Cognito user pools give 50000 patients exactly what the mobile scenario demands: self-registration, MFA enforcement, social providers, and app clients that issue JWTs validated by API Gateway authorizers with no long-lived secrets in code. Consolidating everyone into Cognito user pools federated to Entra ID fails by collapsing that separation and losing centralized workforce governance, permission sets, and audited management access that Identity Center is built to provide for staff. Using Cognito identity pools with IAM roles for patient APIs fails by confusing authentication with authorization because identity pools vend temporary AWS credentials for SDK access to AWS services rather than user-pool JWTs for API authentication and do not natively deliver self-service signup with social login and MFA for consumers. Inviting patients as Entra ID B2B guests for mobile login fails by stretching a workforce collaboration model to consumer scale, blocking self-registration and social login, inflating licensing and lifecycle load, and mixing staff and customer audit trails. Exam caveat is to distinguish user pools for user authentication with JWTs from identity pools for AWS credential vending, and Identity Center for workforce AWS access from Cognito for customer application access. Practical check is to confirm staff assume short-lived Identity Center permission sets via Entra ID and that API Gateway validates tokens from dedicated Cognito app clients with MFA and social providers enabled and no static keys shipped in the app.