
A SaaS company with 40 AWS accounts must demonstrate alignment to AWS security best practices for SOC 2, with prioritized remediation tracked by workload owners across business units. Reviews must be repeatable each quarter without hiring external assessors. Which control should the auditor test first to confirm architecture compliance with security best practices?
Select an answer to reveal the explanation.
Short Explanation
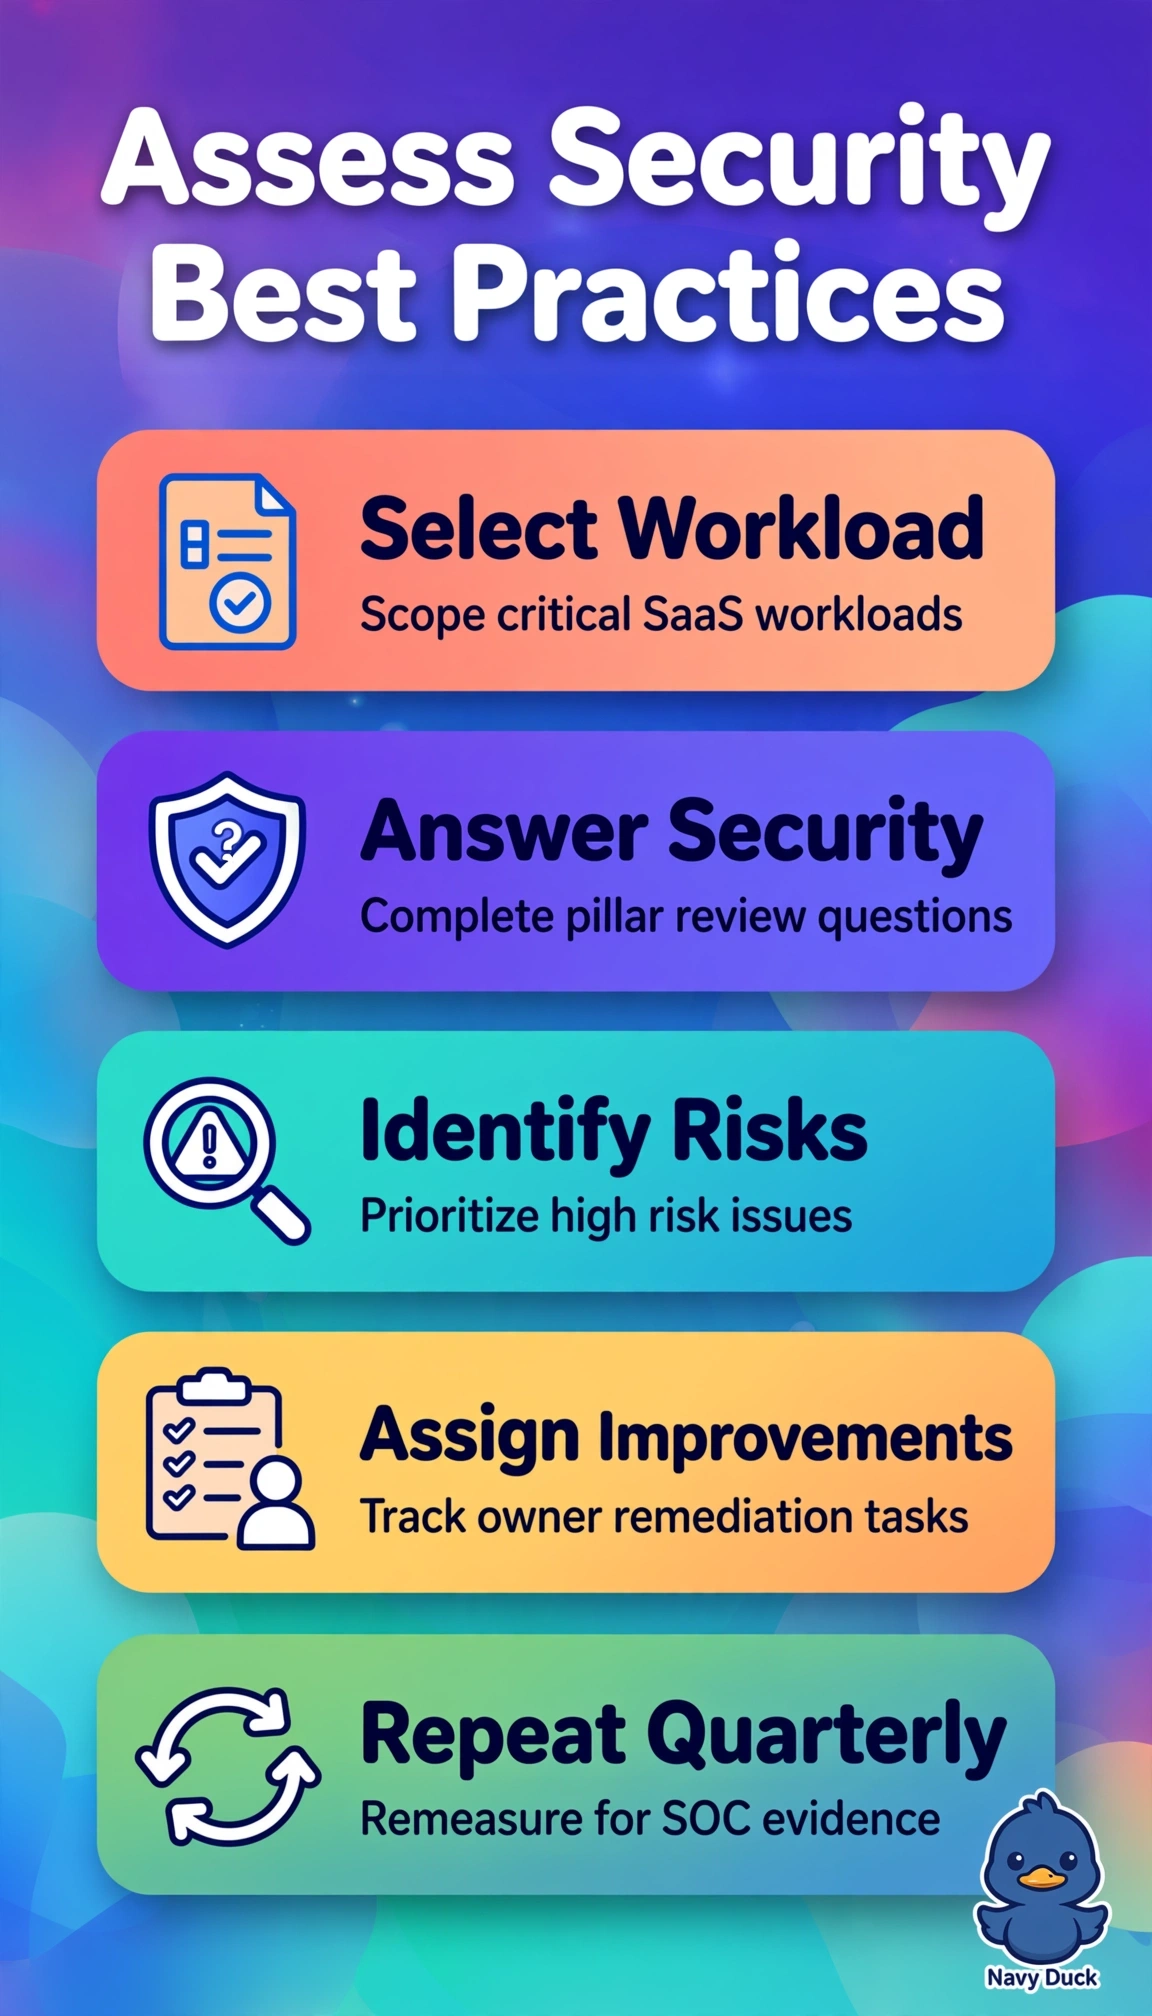
You need repeatable self-assessment with owner accountability. The Well-Architected-Tool review turns best practices into tracked risks and improvements.
Full Explanation
The Well-Architected Tool structures evaluation around the Security pillar questions, captures answers per workload, generates high and medium risks, and creates improvement plans that can be assigned, tracked, and re-measured quarterly for audit evidence. That workflow directly evaluates architecture against AWS best practices with accountability. Artifact provides AWS global compliance reports and certificates that prove platform assurance but do not assess customer architecture decisions. Inspector exports find package and code vulnerabilities that represent one technical input, not a comprehensive best-practice governance review with milestones. Cost Explorer rightsizing addresses spend efficiency rather than security control design. For the exam, distinguish platform attestations from customer design reviews. In practice, integrate the Tool with Jira tickets and re-run reviews after remediation to close risks.