
A fintech startup builds a Java microservice with AWS CodePipeline and CodeBuild from GitHub pull requests. Auditors require SAST for code vulnerabilities and hardcoded secrets on every pull request, with developer-friendly fix guidance before merge. Builds already scan container images. Which pipeline scan configuration discovers and remediates code vulnerabilities earliest?
Select an answer to reveal the explanation.
Short Explanation
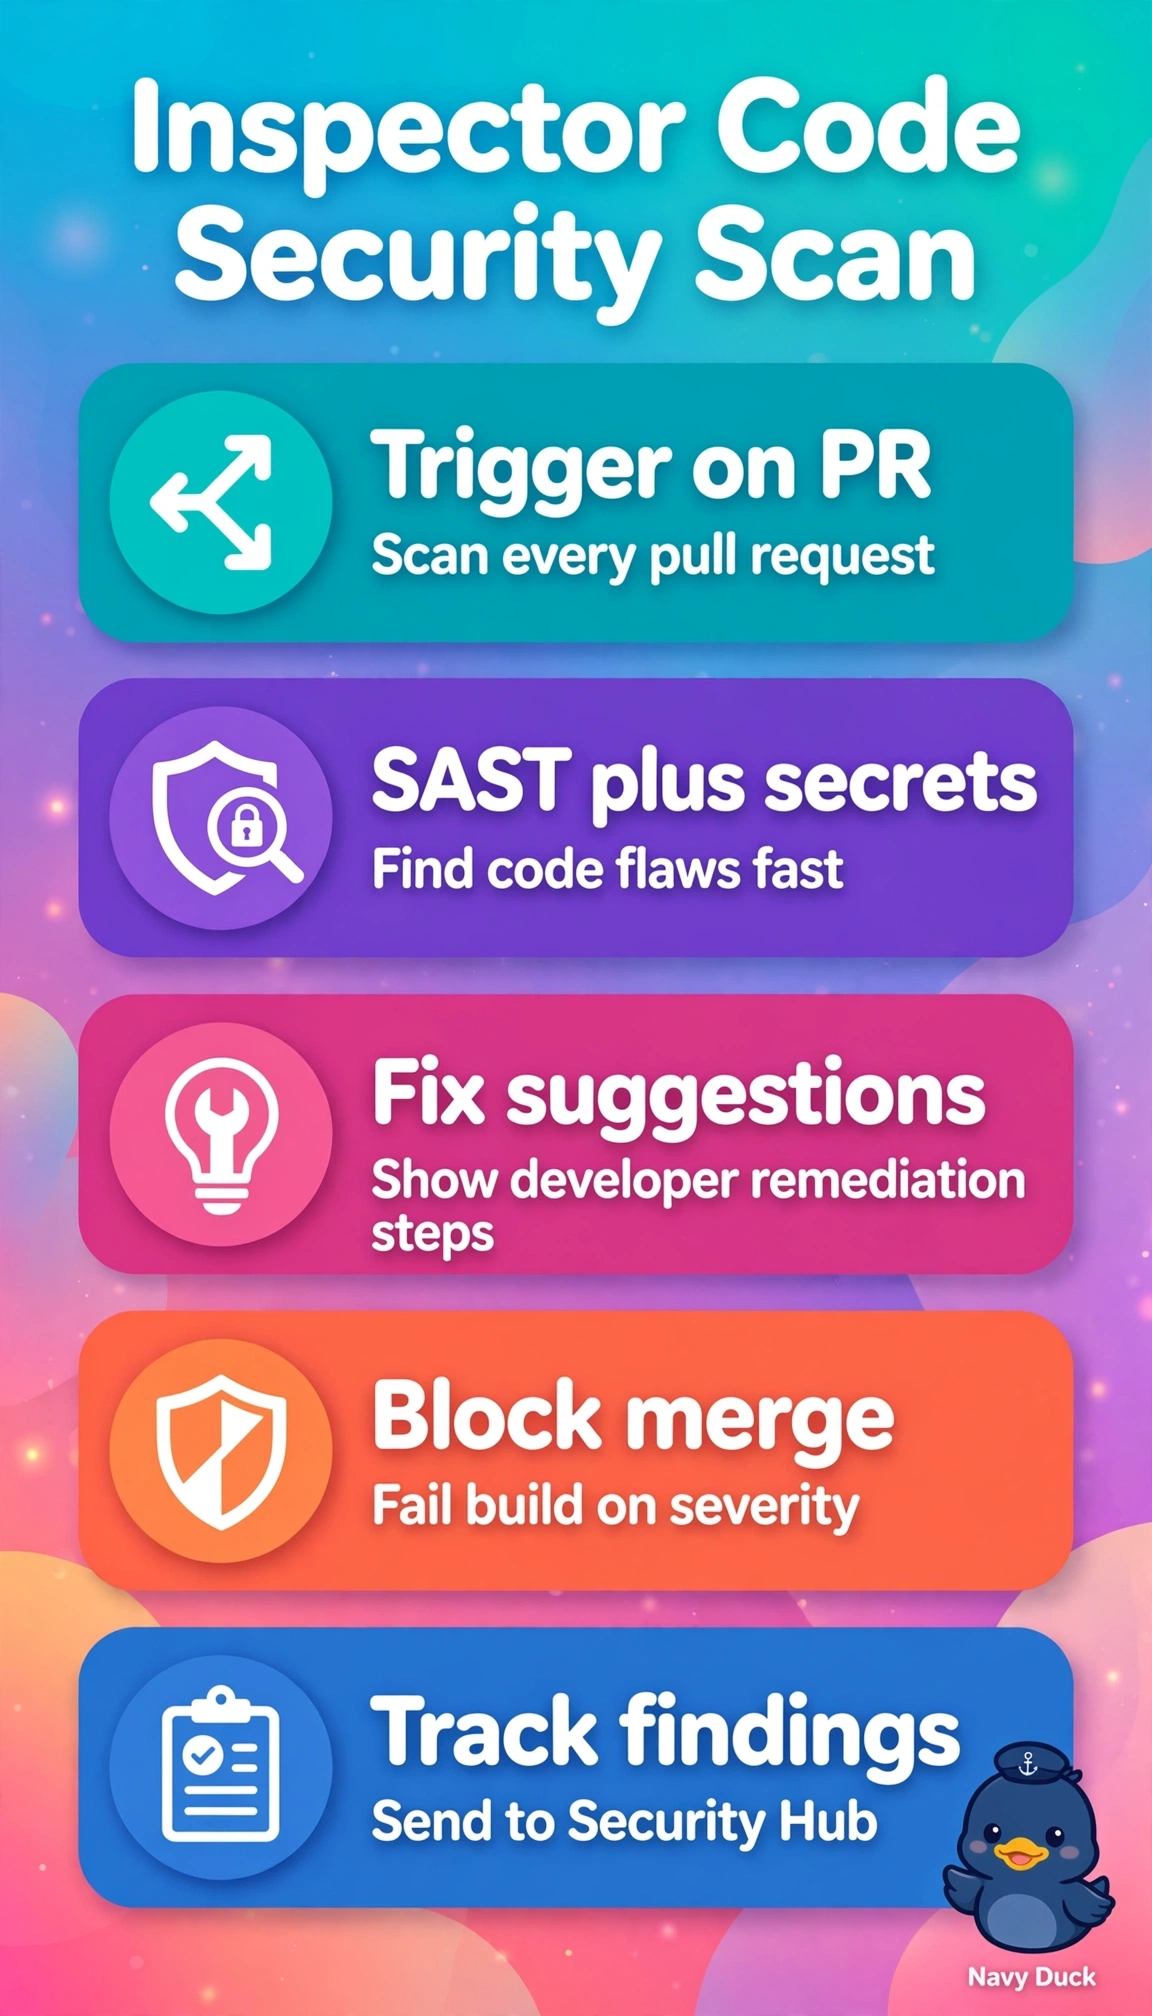
You catch flaws at their cheapest point: in the pull request, before code merges. Inspector code security checks for risky code and hardcoded secrets, then gives developers fix guidance they can act on.
Full Explanation
Amazon Inspector code security is the right configuration because it performs SAST on application source and detects hardcoded secrets in the pull-request workflow. Running these scans on every pull request with blocking findings and fix recommendations satisfies the audit requirement, gives developers actionable guidance before merge, and discovers issues at the earliest stage. Enabling only SAST scans for Java vulnerabilities with blocking findings and recommendations meets the frequency and enforcement requirements, but omits secrets detection, so hardcoded credentials can escape the required scan. Running full code security scans with recommendations in non-blocking advisory mode provides visibility, but does not stop vulnerable or secret-bearing code from merging, contrary to the required pre-merge control. Scanning container images built from pull requests with blocking findings and recommendations is a useful artifact-level control, but it analyzes images rather than source code, duplicates the existing image scans, and misses the earliest source-level feedback. For exams, distinguish code security scans from container image scans: only code security covers both SAST and secrets detection. In practice, verify that each CodeBuild pull-request build triggers code scanning, that a test secret and SAST finding block the merge, and that developers can see actionable fix recommendations in the pull request.