
A data platform runs ETL jobs on EC2, nightly Glue transforms scheduled by EventBridge, and ECS Fargate tasks pulling from ECR and S3. Each workload overuses one shared IAM role and auditors demand scoped credentials with automatic rotation. Which role assignment should the engineer apply to authorize compute workloads?
Select an answer to reveal the explanation.
Short Explanation
You're sharing one badge for three different jobs and auditors rightly hate it. Proper role separation gives each workload its own keycard that only opens its assigned rooms.
Full Explanation
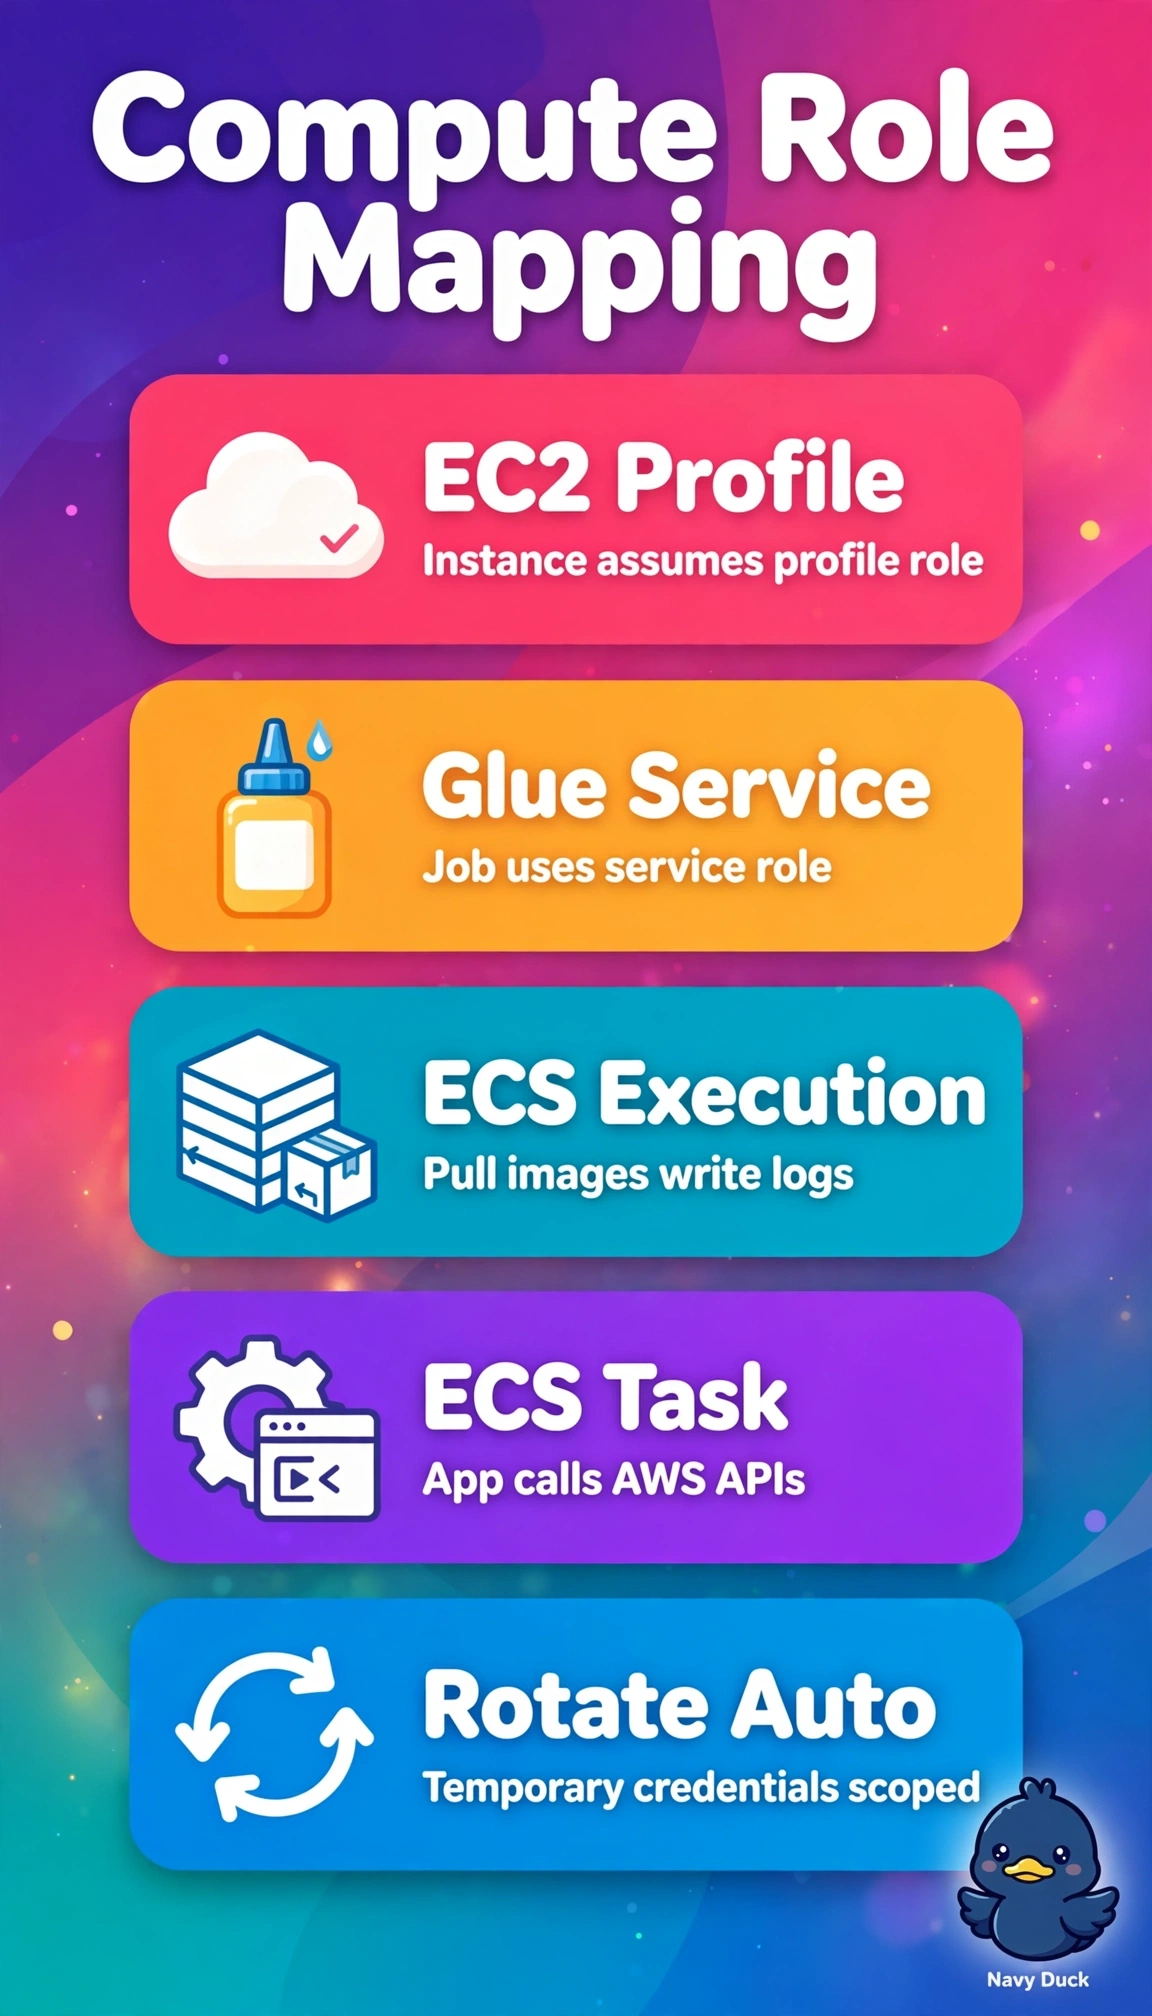
The correct assignment succeeds because every workload receives scoped short-lived credentials via STS with automatic rotation using its native mechanism: EC2 instance profiles deliver temporary credentials through instance metadata with no stored keys, Glue assumes a dedicated service role trusted by the Glue service for S3, Data Catalog, logging and job APIs when EventBridge invokes StartJobRun, and ECS Fargate splits responsibilities between an execution role for ECR pulls, log delivery and secrets retrieval and a separate task role for application SDK calls to S3. The scheduler-role approach fails on trust relationship because the EventBridge scheduler role is assumable only by the scheduler to trigger invocations and lacks Glue service permissions for data transformation. The task-only approach fails on container lifecycle because Fargate cannot pull private ECR images or publish logs without an execution role, so tasks stop before application code runs despite correct S3 permissions. The execution-only approach fails on least-privilege scoping because using one role for both infrastructure operations and in-code S3 access over-privileges the runtime and violates the audit demand for isolation. An exam caveat is to distinguish invoker versus performer and infrastructure versus application permissions rather than choosing any role-based answer. A practical check is to delete static keys, verify AssumeRole in CloudTrail, and test each workload launch while validating effective permissions with IAM Access Analyzer.