
A financial services group operates 150 AWS accounts with strict regulators requiring consistent detective controls and no local security opt-outs. They designated a security tooling account and use Control Tower. They must enforce GuardDuty, Inspector, and Security Hub everywhere from one place. Which delegated-administration strategy enforces centralized security service control?
Select an answer to reveal the explanation.
Short Explanation
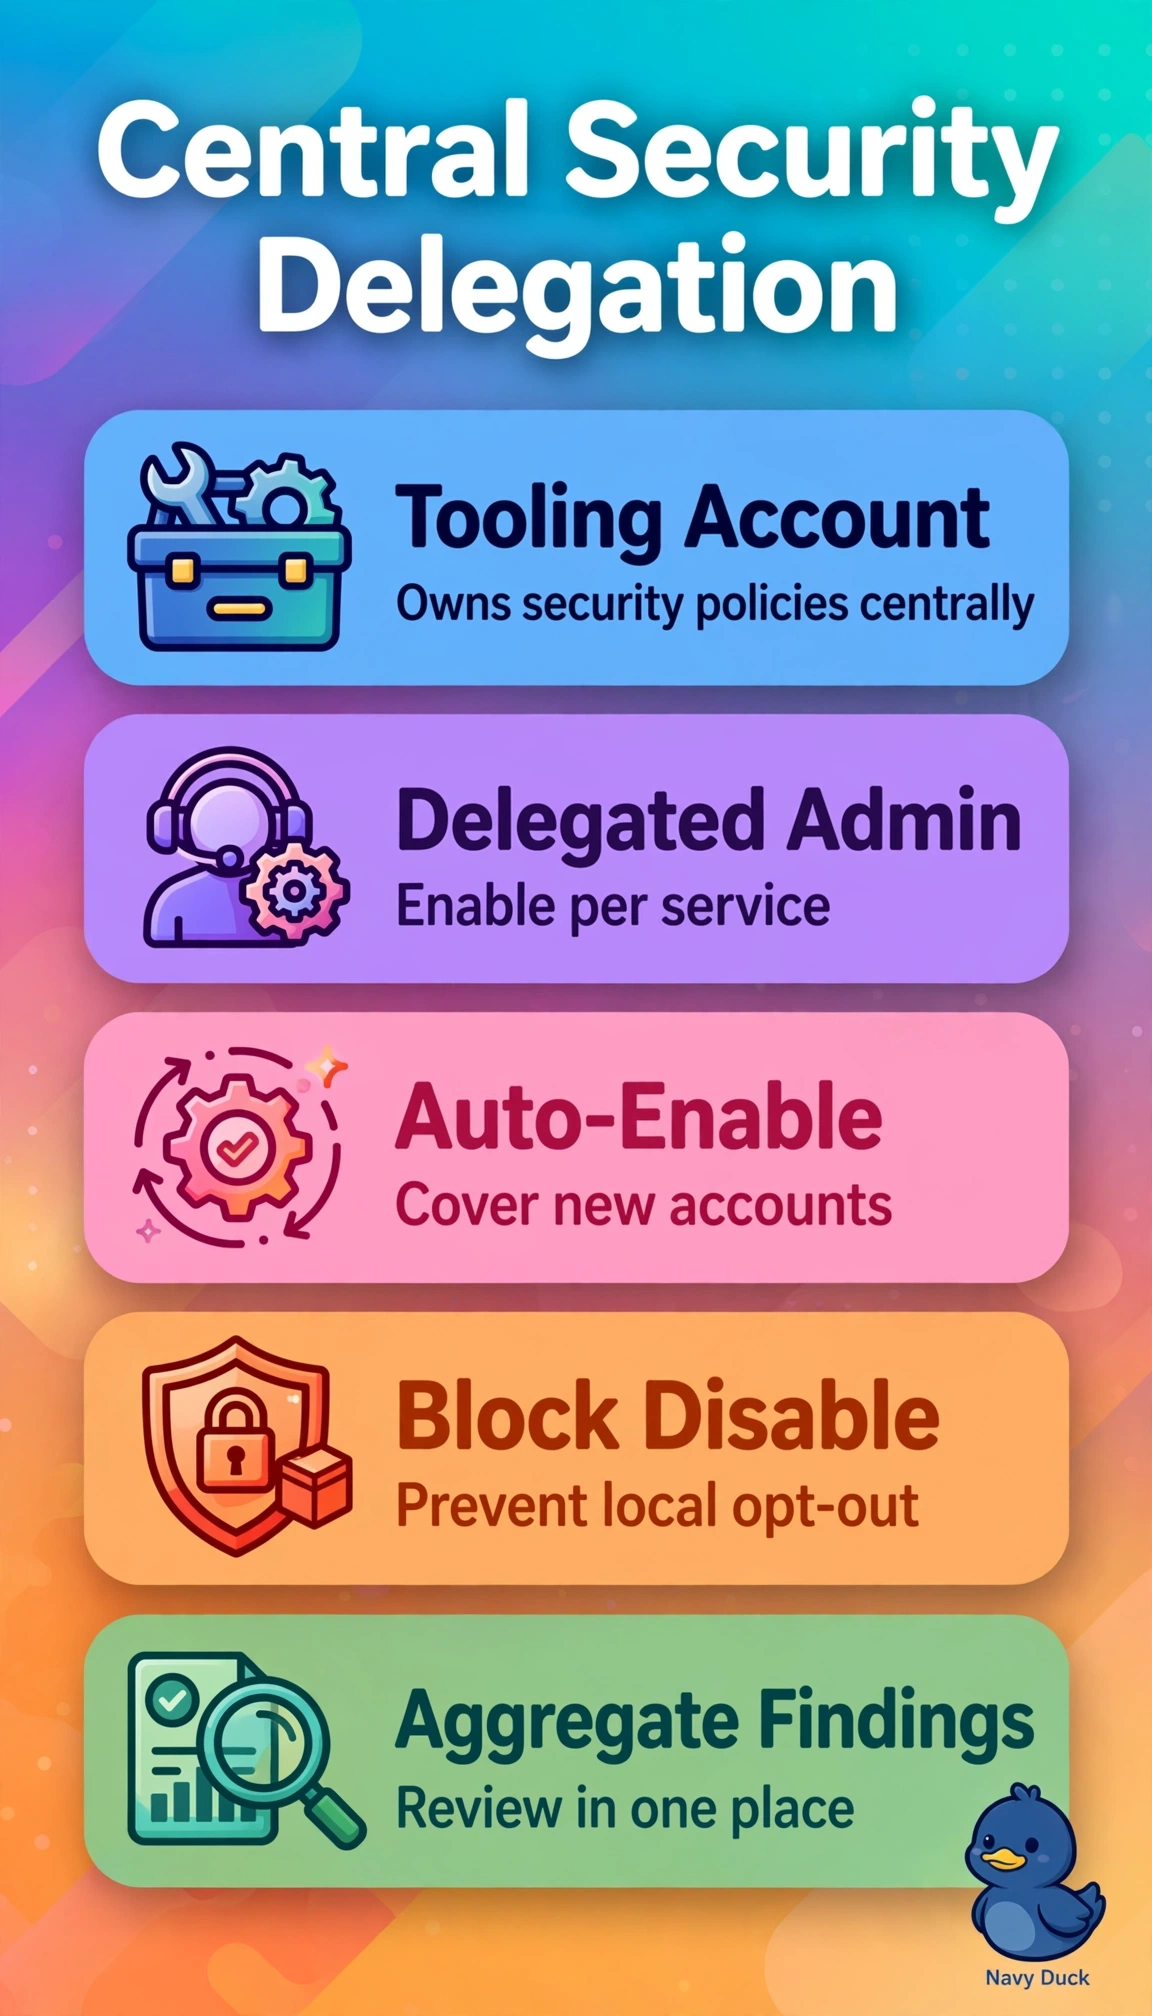
You’ll herd 150 accounts without chasing invites. Delegation lets your tooling account own policies while members can’t switch them off. Auto-enable keeps every new account covered from day one.
Full Explanation
The correct strategy works because AWS Organizations delegated administration lets the designated security tooling account centrally own GuardDuty, Inspector, and Security Hub configuration, with organization auto-enable ensuring every current and future Control Tower-enrolled account inherits consistent detective coverage without per-account setup, satisfying single-place control and regulator demand for uniformity. The member-opt-out approach fails on governance because permitting local disable or tuning retains bypassable enforcement and drift that auditors will flag despite central visibility. The management-account approach fails on architecture because concentrating security operations in the billing and organization-management account contradicts the tooling-account design and least-privilege separation and increases blast radius even though centralization is preserved. The manual-onboarding approach fails on lifecycle because without auto-enable coverage lags account creation and violates the everywhere-including-future requirement during Control Tower growth. Exam caveat is to distinguish enabling detectors from preventing deactivation, since delegated administration plus auto-enable provides consistent deployment while durable no-opt-out often additionally needs Organizations policies that centrally restrict disabling, so read whether the stem asks for administration strategy versus preventive guardrail. Practical check is to inspect the tooling account for delegated-administrator status and auto-enable for all three services, then enroll a test account through Account Factory and confirm centralized findings, coverage, and inability to disable locally appear within minutes.