
A retail enterprise runs 60 AWS accounts with VPCs that need identical WAF rules and Security Groups baseline, plus automatic remediation when teams drift. Central security wants single-pane enforcement without logging into accounts. Which centralized deployment strategy enforces consistent network protection centrally?
Select an answer to reveal the explanation.
Short Explanation
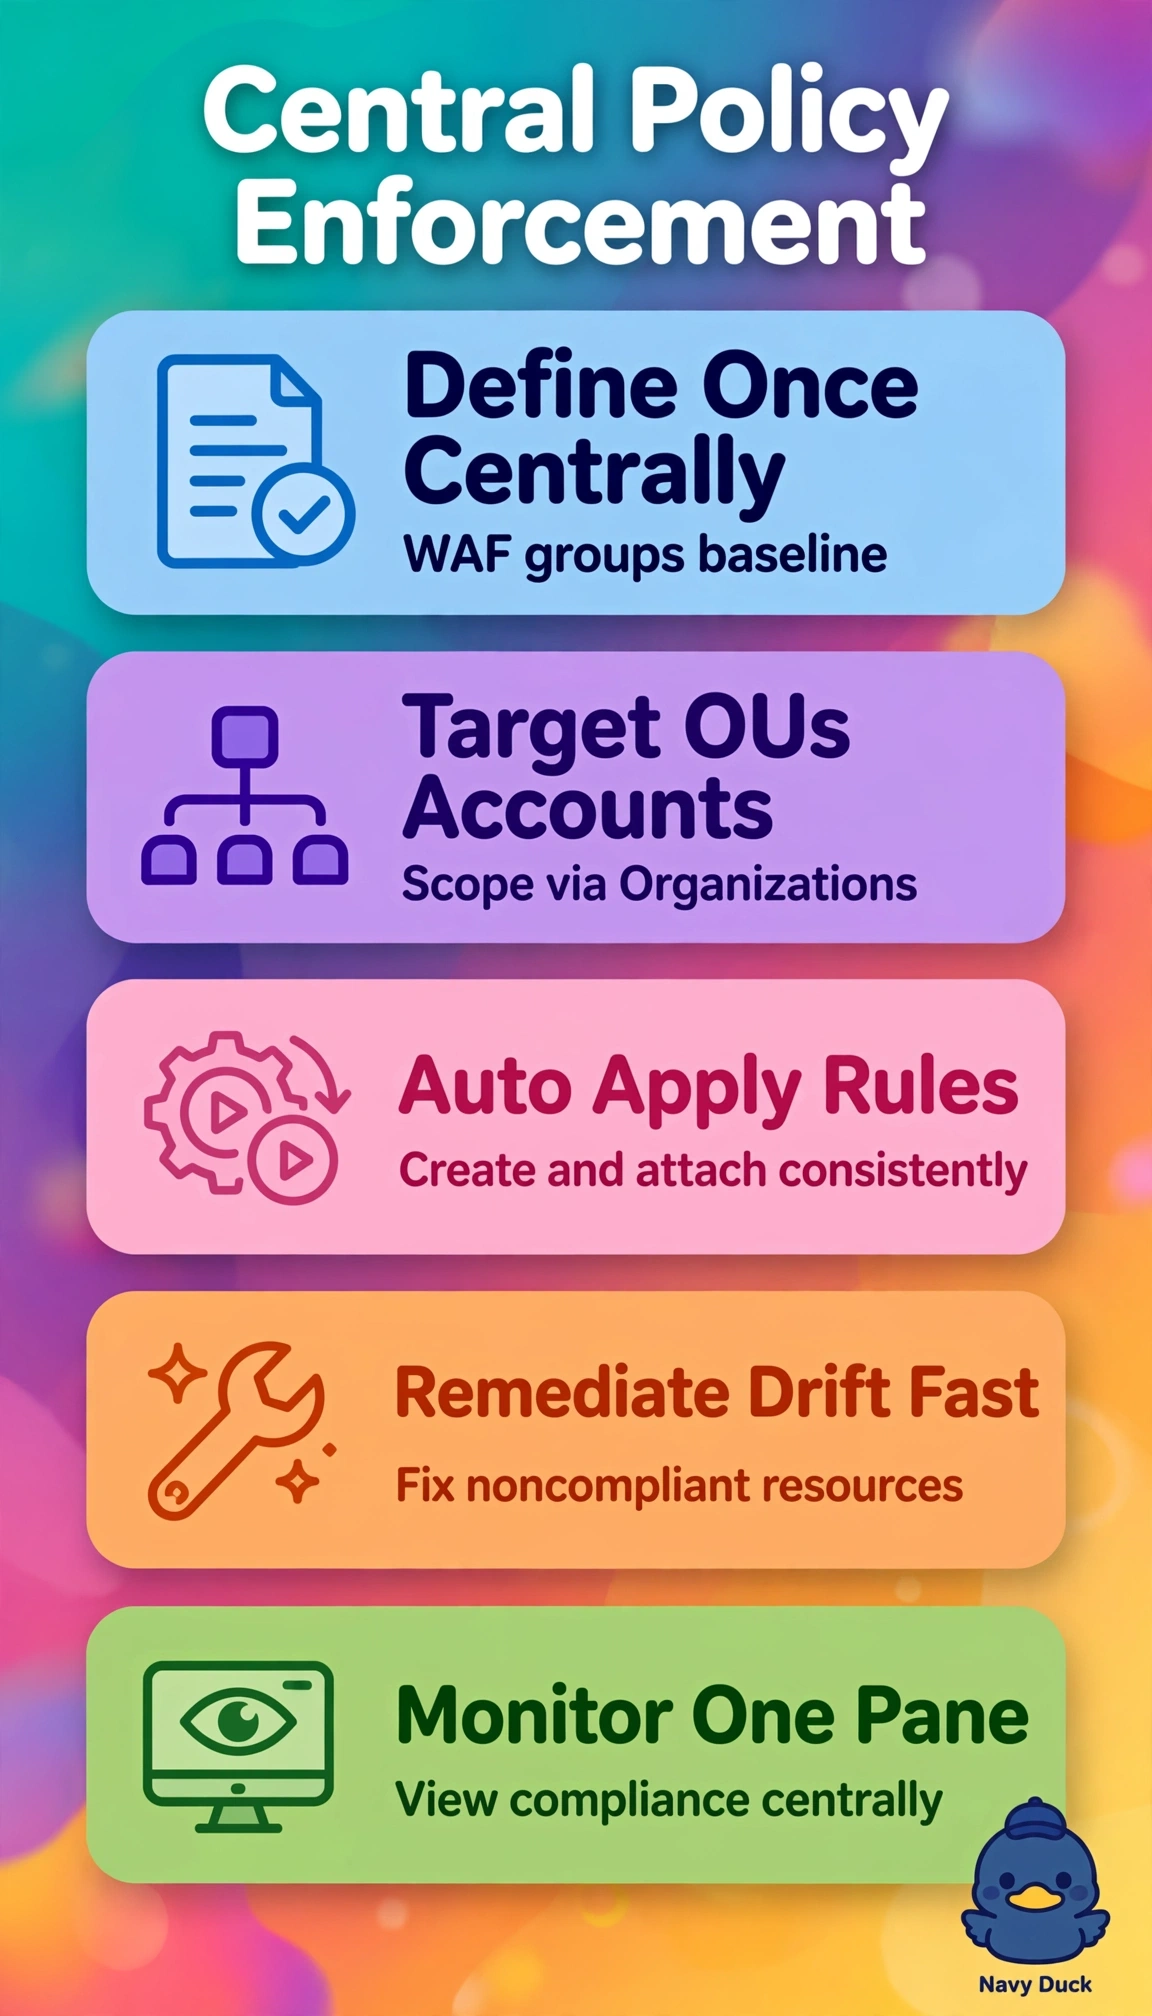
You're pushing one rulebook from headquarters instead of nagging branches. Firewall Manager auto-applies and fixes WAF and group drift across every account for you.
Full Explanation
AWS Firewall Manager integrated with AWS Organizations is the designated central enforcement service for distributed network protections because a single administrator can define WAF and Security Group policies once and have them automatically applied to in-scope accounts and resources, with continuous evaluation and automatic remediation when local changes cause drift, which satisfies identical baselines, single-pane management, and no per-account login in one workflow. Deploying identical protections with CloudFormation StackSets from the management account is a legitimate large-scale provisioning pattern, yet it fails the automatic remediation requirement because StackSets create resources but do not continuously audit and revert unauthorized modifications like a Firewall Manager policy does. Aggregating AWS Config rules in a delegated administrator account is a best practice for centralized compliance visibility across many accounts, yet it fails the enforcement requirement because detection and dashboards alone only report noncompliance and do not centrally push corrections or prevent drift. Routing traffic through a centralized Network Firewall in a shared inspection VPC is a sound hub-and-spoke inspection architecture, yet it fails the distributed baseline fact because it centralizes transit inspection rather than managing per-VPC WAF associations and per-account Security Group baselines where workloads reside. On exams, distinguish deploy-once automation from enforce-always governance when the stem explicitly demands drift remediation and central control, and in practice verify Organizations integration, Firewall Manager administrator delegation, policy scope and auto-remediation settings, then test by intentionally modifying a member WAF association or Security Group to confirm automatic reversion.