
A retail company with 40 AWS accounts in Organizations must retain all management and data events centrally, prevent member accounts from disabling logging, and forward logs to a security SIEM. Auditors require one consistent trail definition. Which logging configuration should the engineer implement to centralize AWS service activity across the organization?
Select an answer to reveal the explanation.
Short Explanation
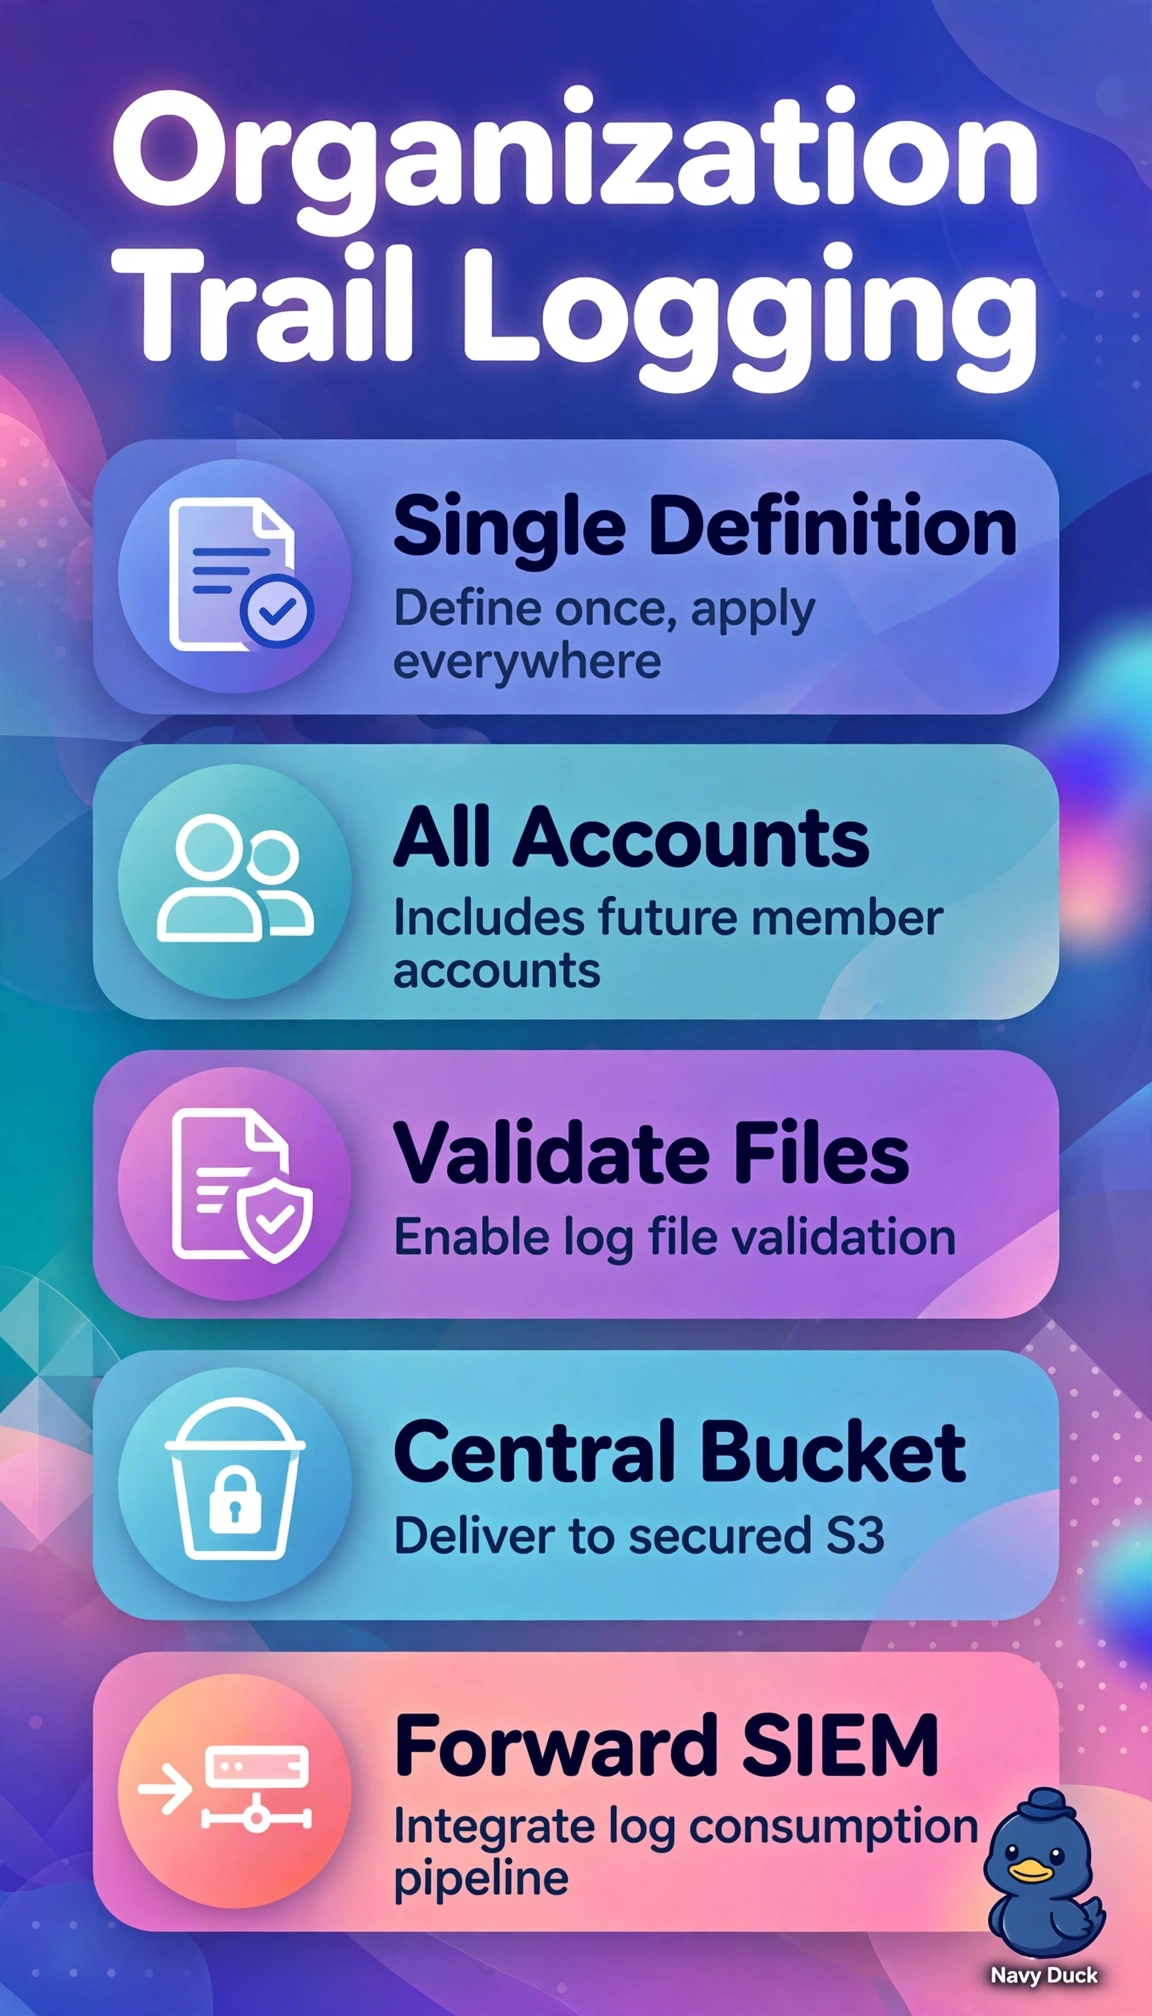
Central control wins here for scale and tamper resistance. An organization trail defined once in management enforces consistent logging everywhere and locks in your evidence pipeline.
Full Explanation
The organization trail created in the management account is correct because it applies a single definition across all current and future accounts, captures both management and data events centrally in one S3 bucket with integrity validation for audit assurance, blocks member-level tampering, and provides a stable feed for SIEM ingestion. A management-events-only organization trail fails on completeness by concept because S3 object-level, Lambda execution and other data events would be absent despite centralization and tamper resistance, violating the explicit retain-all requirement. Identical StackSet-deployed account-level trails fail on governance by concept because even with central replication each trail remains locally owned and stoppable, so there is no enforced single definition and drift or disabling can occur. Separate trails per organizational unit fail on consistency by concept because auditors demand one uniform definition, while multiple definitions complicate versioning, validation and SIEM parsing even when coverage and central storage match. Exam caveat: distinguish organization trails versus organization event data stores and delegated Log Archive designs, and remember cost-optimized management-only logging is still incomplete when data events are stated. Practical check: in the console verify the trail shows organization type, includes data event selectors, points to the central bucket with log file validation enabled, and attempt from a member account to confirm stop or delete is denied.