
A holding company with 60 AWS accounts needs a single view of GuardDuty, Inspector, and Macie findings plus centralized CloudTrail and Config history for threat hunting. Regional analysts require local access to aggregated data. Which monitoring aggregation design centralizes security and monitoring events for organization-wide alerting?
Select an answer to reveal the explanation.
Short Explanation
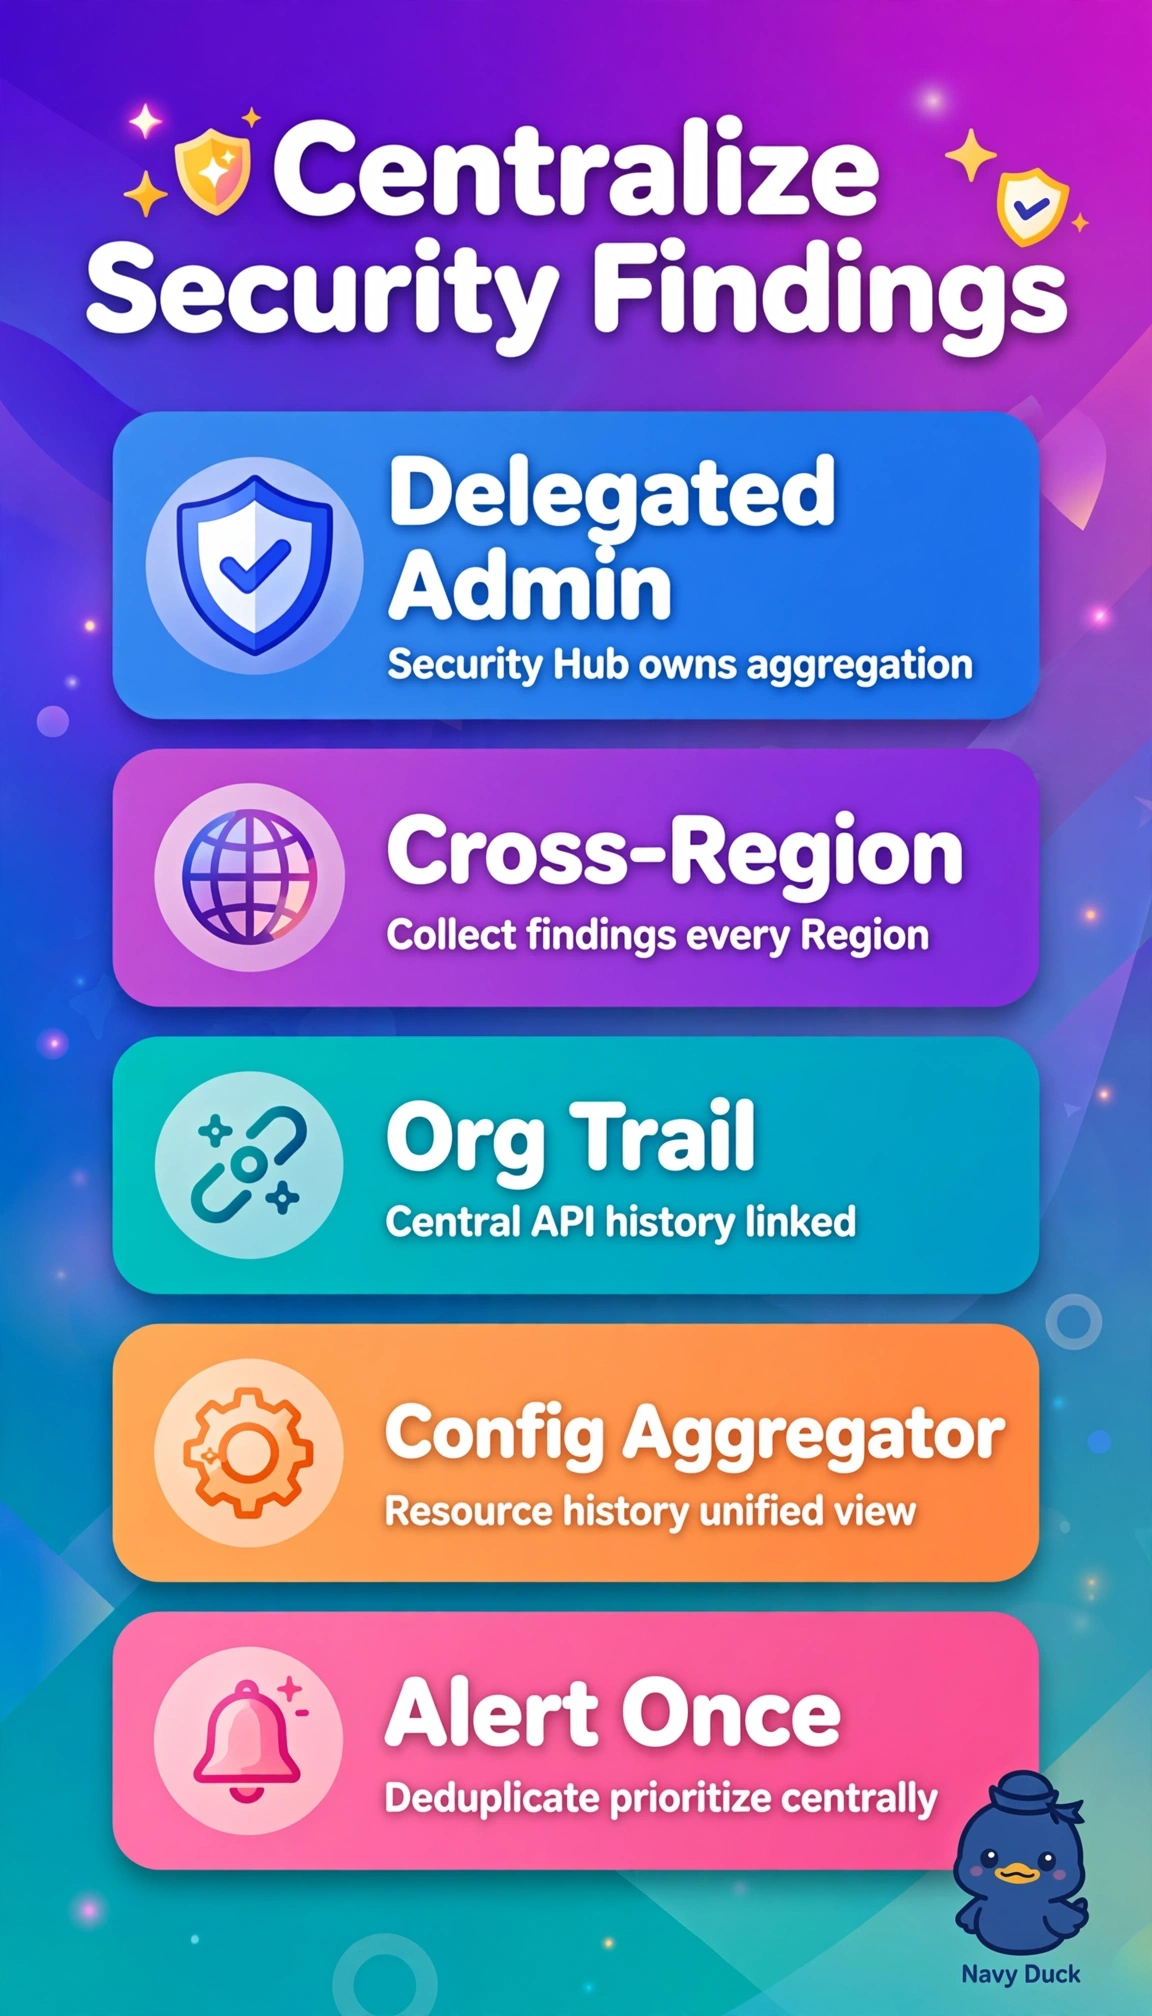
You’re coordinating security across many accounts, so a shared view helps your analysts work from the same picture. A delegated Security Hub administrator with cross-Region aggregation, an organization trail, and a Config aggregator brings findings and history together while supporting regional access.
Full Explanation
The delegated Security Hub administrator with cross-Region aggregation, an organization trail, and a Config aggregator is the complete design: delegated administration supports organization-wide auto-enrollment and policy control for GuardDuty, Inspector, and Macie, while cross-Region aggregation brings findings into one view. The organization trail provides immutable multi-account CloudTrail history, and the Config aggregator centralizes configuration timelines, supporting correlation and threat hunting with delegated regional access. Aggregating findings, trail, and configuration while restricting access to the management account centralizes the data, but leaves regional analysts dependent on that account rather than providing delegated access to aggregated regional views. Centralizing CloudTrail Lake and Config history can support log hunting and delegated regional queries, but neither ingests and deduplicates the GuardDuty, Inspector, and Macie findings as Security Hub does, so normalized severity and workflow are missing; CloudTrail Lake is also closed to new customers. Delegated Security Hub with cross-Region aggregation but member-local CloudTrail and Config provides findings visibility, yet local trails and recorders do not provide immutable centralized retention or organization-wide timeline queries. Exam caveat: finding aggregation differs from log and configuration aggregation, so all three services are needed here. Practical check: verify the delegated administrator in Organizations, enabled standards and cross-Region aggregation, an organization trail logging to a central bucket, and a Config aggregator authorized in all Regions.