
A logistics firm is preparing for a customer security review and wants a structured gap assessment of its multi-account architecture against AWS security best practices with prioritized improvements. Which evaluation service should the security architect use to benchmark architecture maturity and track remediation?
Select an answer to reveal the explanation.
Short Explanation
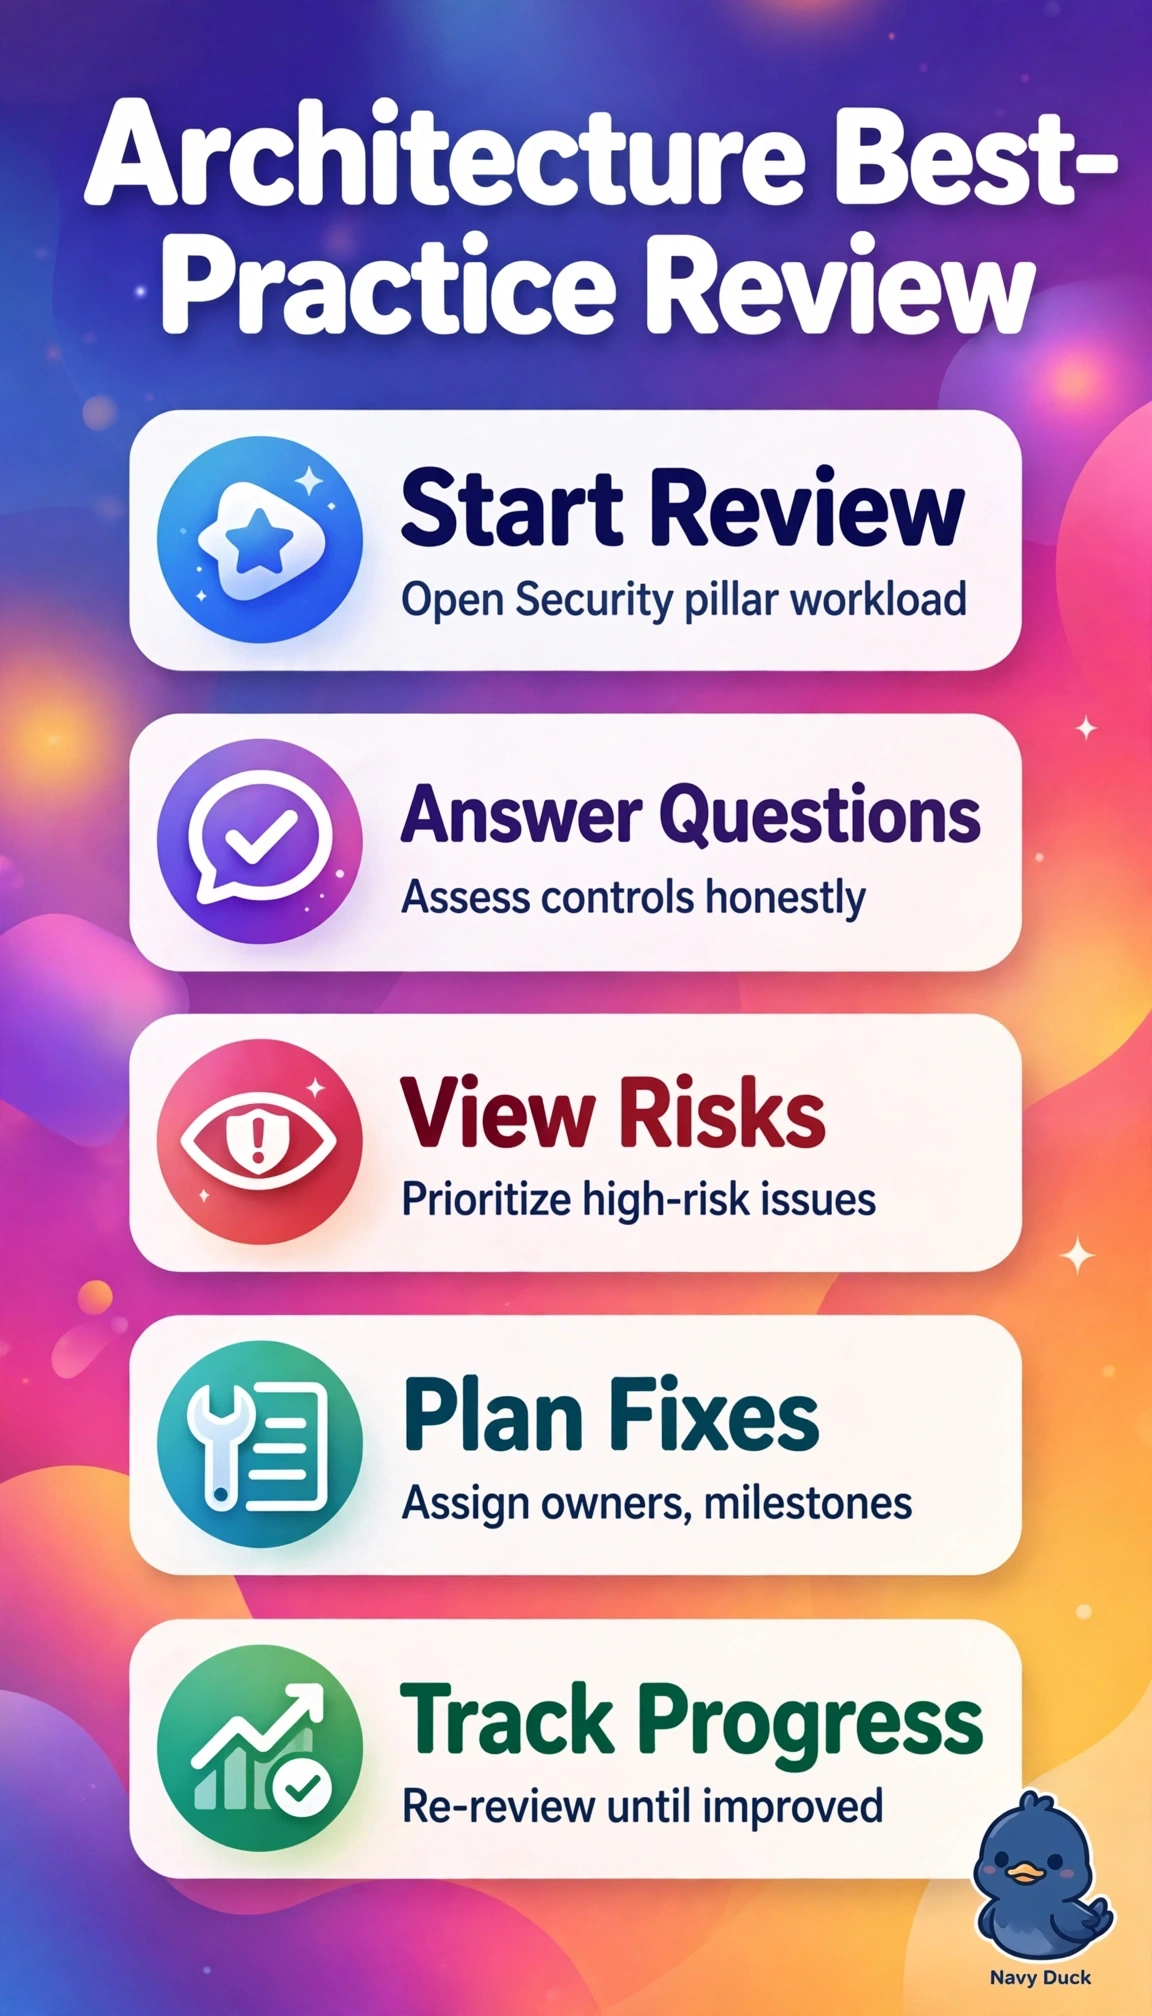
You need a health checkup, not just a burglar alarm for live break-ins. The Well-Architected Tool grades your design against best practices and builds your fix-it list.
Full Explanation
The correct approach uses the AWS Well-Architected Tool with the Security pillar and relevant lenses to answer design questions, generate high- and medium-risk issues, and track an improvement plan with owners and milestones for architecture maturity. Running Audit Manager fails by concept because it collects evidence to prove compliance to a specific regulatory framework rather than benchmarking design trade-offs against best-practice guidance, while enabling Security Hub fails because it continuously aggregates misconfiguration and control findings rather than facilitating a structured architectural review with recommendations. Activating GuardDuty fails because it performs intelligent threat detection on runtime telemetry to find active malicious behavior, not evaluating preventive architecture choices. For the exam, link Well-Architected Tool to best-practice reviews and Audit Manager to evidence for audits, and in practice schedule reviews after major launches, integrate custom lenses for company standards, and export milestone reports for customers.