
A fintech builds containers in CodeBuild and pushes to Amazon ECR for regulated payment services requiring vulnerability reports before deploy and tamper-proof images. Which pipeline security scanning design assesses vulnerabilities and signs artifacts?
Select an answer to reveal the explanation.
Short Explanation
You're checking IDs and sealing packages before shipping medicine. Inspector plus signing proves images are clean and tamper-proof before release.
Full Explanation
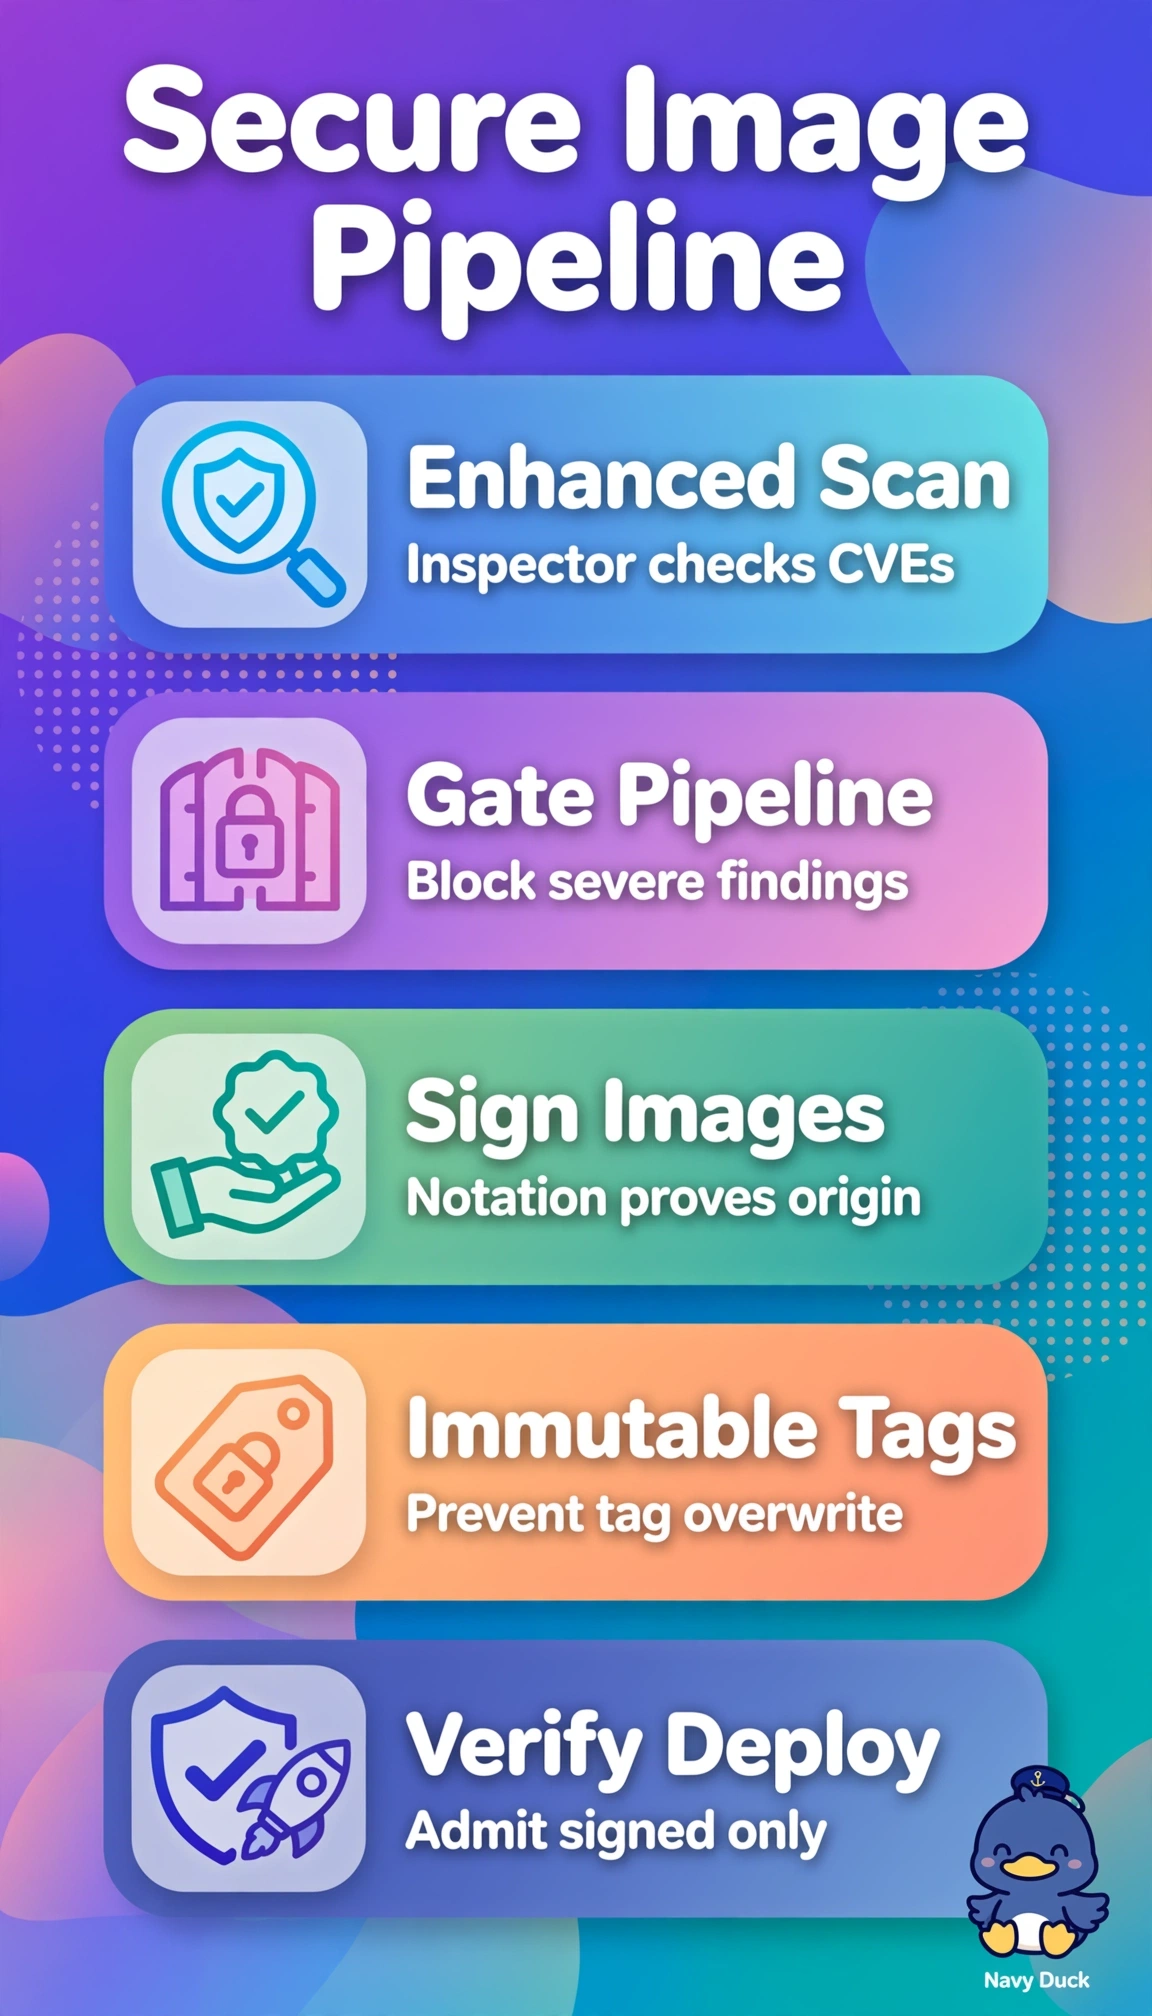
The correct design works because it enforces continuous assessment, pre-deployment control, and verifiable provenance together as required for regulated payment services: ECR enhanced scanning with Amazon Inspector continuously evaluates operating system and language dependencies for CVEs to generate auditable vulnerability reports, CodePipeline quality gates block promotion when findings exceed severity thresholds, and Notation signatures provide cryptographic attestation verified at deployment to ensure tamper-proof images. The alternative using enhanced scanning and gating but relying on immutable tags fails provenance because tags even when immutable cannot cryptographically prove origin and integrity like a signature, allowing substituted or rebuilt images to pass. The alternative using basic scanning with gating and signing fails assessment scope because basic scanning checks only operating system layers at push without continuous Inspector coverage of application dependencies needed for compliance reporting. The alternative scanning after production deployment with signing fails prevention because post-deploy detection violates the explicit before-deploy requirement and allows vulnerable images to run. As an exam caveat, distinguish push-time basic scanning from continuous enhanced scanning and remember tag immutability never equals signing. As a practical check, verify Inspector HIGH and CRITICAL findings in ECR, confirm the pipeline halts promotion, and enforce signature verification in the cluster admission policy so only signed digests deploy.