
A SaaS company runs dev, test, and prod in separate AWS accounts across two Regions. Leaders require one pipeline that deploys with delegated least-privilege roles, promotes the same immutable build artifact between stages, and blocks prod without manual approval. Which pipeline deployment design satisfies multi-account promotion?
Select an answer to reveal the explanation.
Short Explanation
You're shipping one golden build through locked doors, not rebuilding at each stop. Promotion with cross-account roles lets each stage assume only its rights while approvals guard production like a bouncer.
Full Explanation
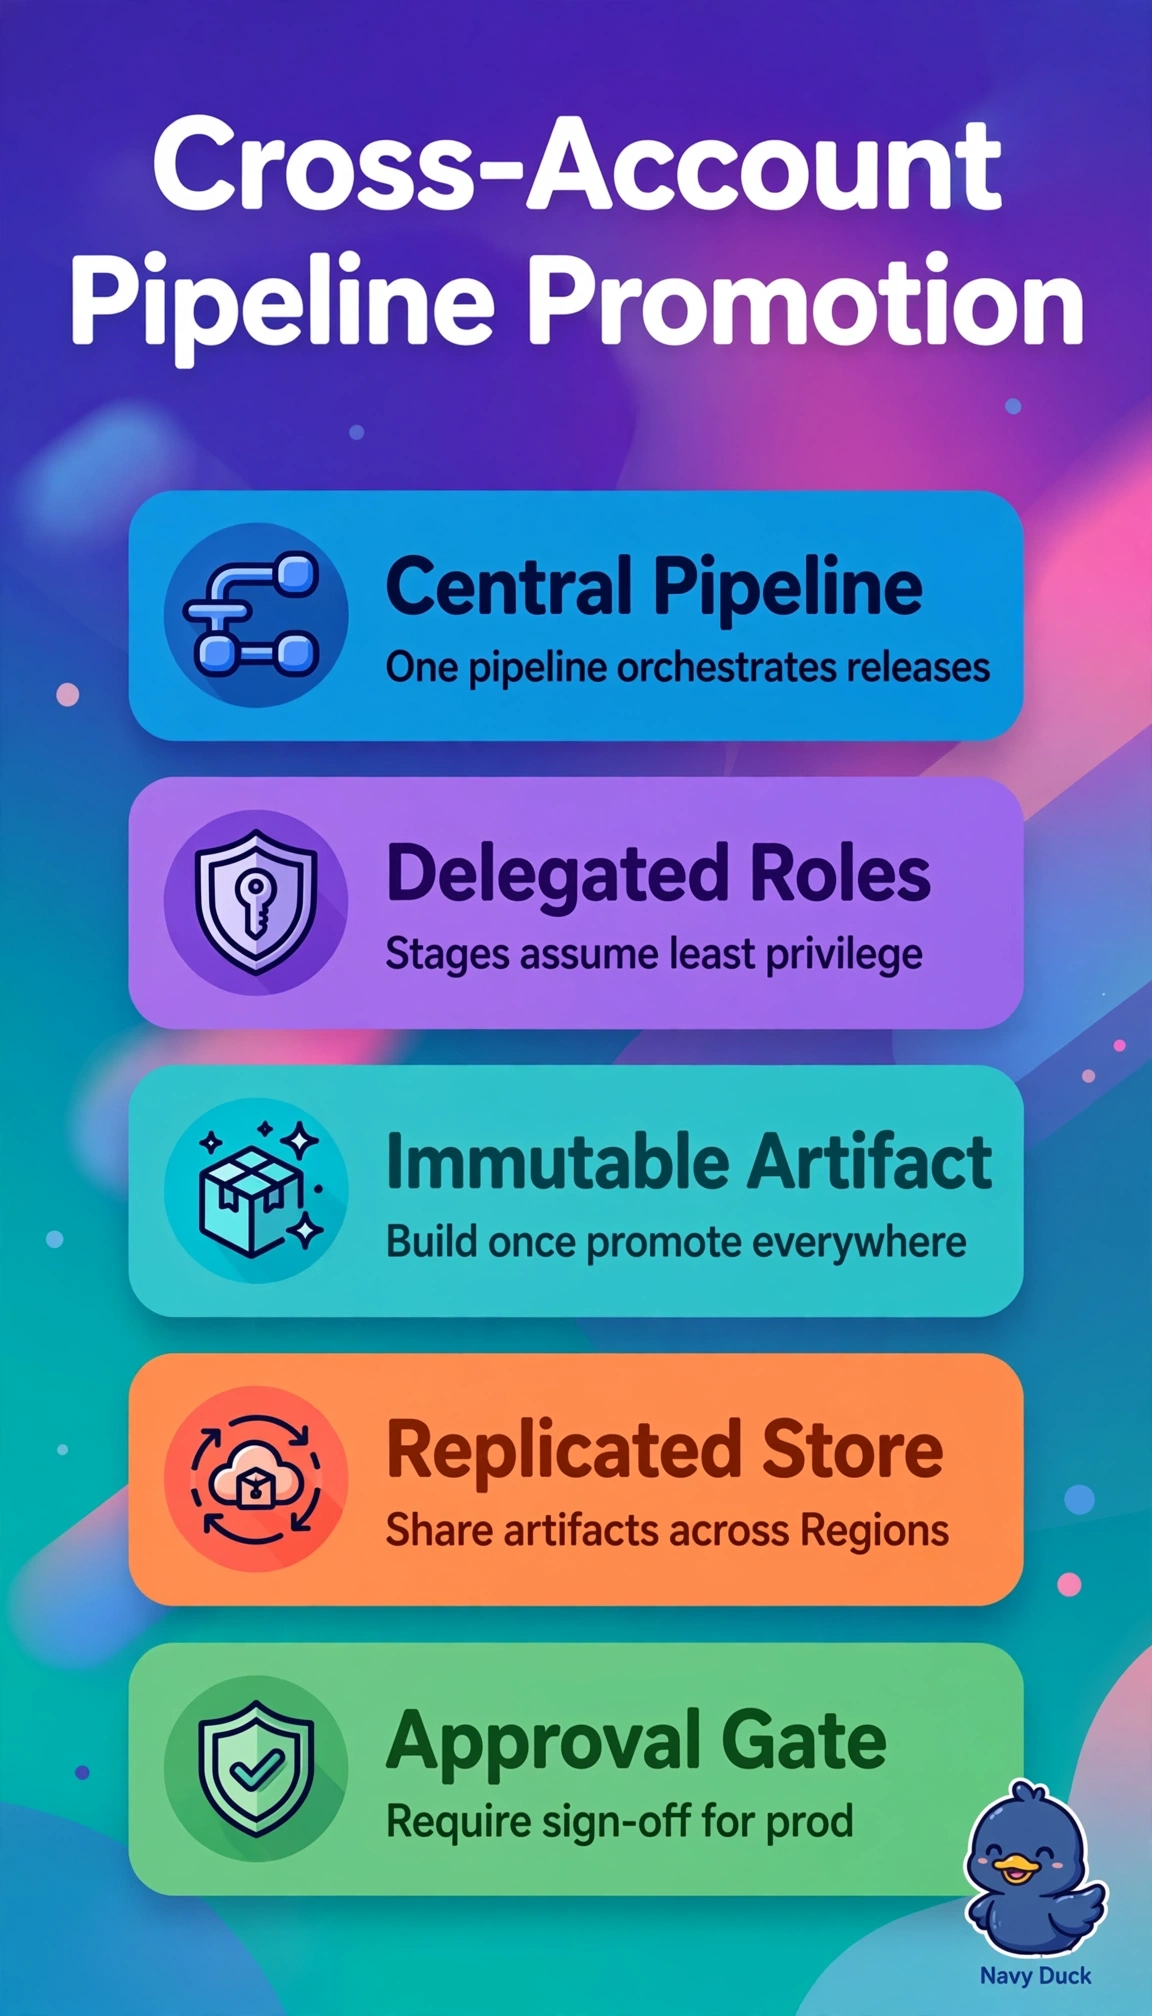
A central CodePipeline using cross-account IAM role delegation plus replicated artifact stores enables one immutable artifact built once to be promoted across accounts and Regions, with stage roles granting least privilege and a manual approval action gating production, directly meeting delegation and promotion requirements. Separate per-account pipelines that rebuild from source violate immutable artifact promotion and create drift between test and prod. CodeBuild with long-lived access keys and presigned URL copying breaks least privilege, adds credential management risk, and provides no governed promotion or approval workflow. CodeDeploy from workstations with shared IAM users bypasses pipeline governance, auditability, and role delegation entirely. Exam caveat is to look for same artifact promoted plus assumed roles and approval, and practical check is to validate trust policies, artifact bucket policy with KMS grants, and pipeline stage transitions in lower environments first.