
A media company produces live-stream metadata in an ap-southeast-2 production account and must deliver filtered playback events to a central analytics custom bus in a eu-west-1 audit account with secure least-privilege access and replay for missed events. Compliance requires no public internet exposure of the bus. Which cross-account and cross-Region event routing pattern using event buses and forwarding meets these needs?
Select an answer to reveal the explanation.
Short Explanation
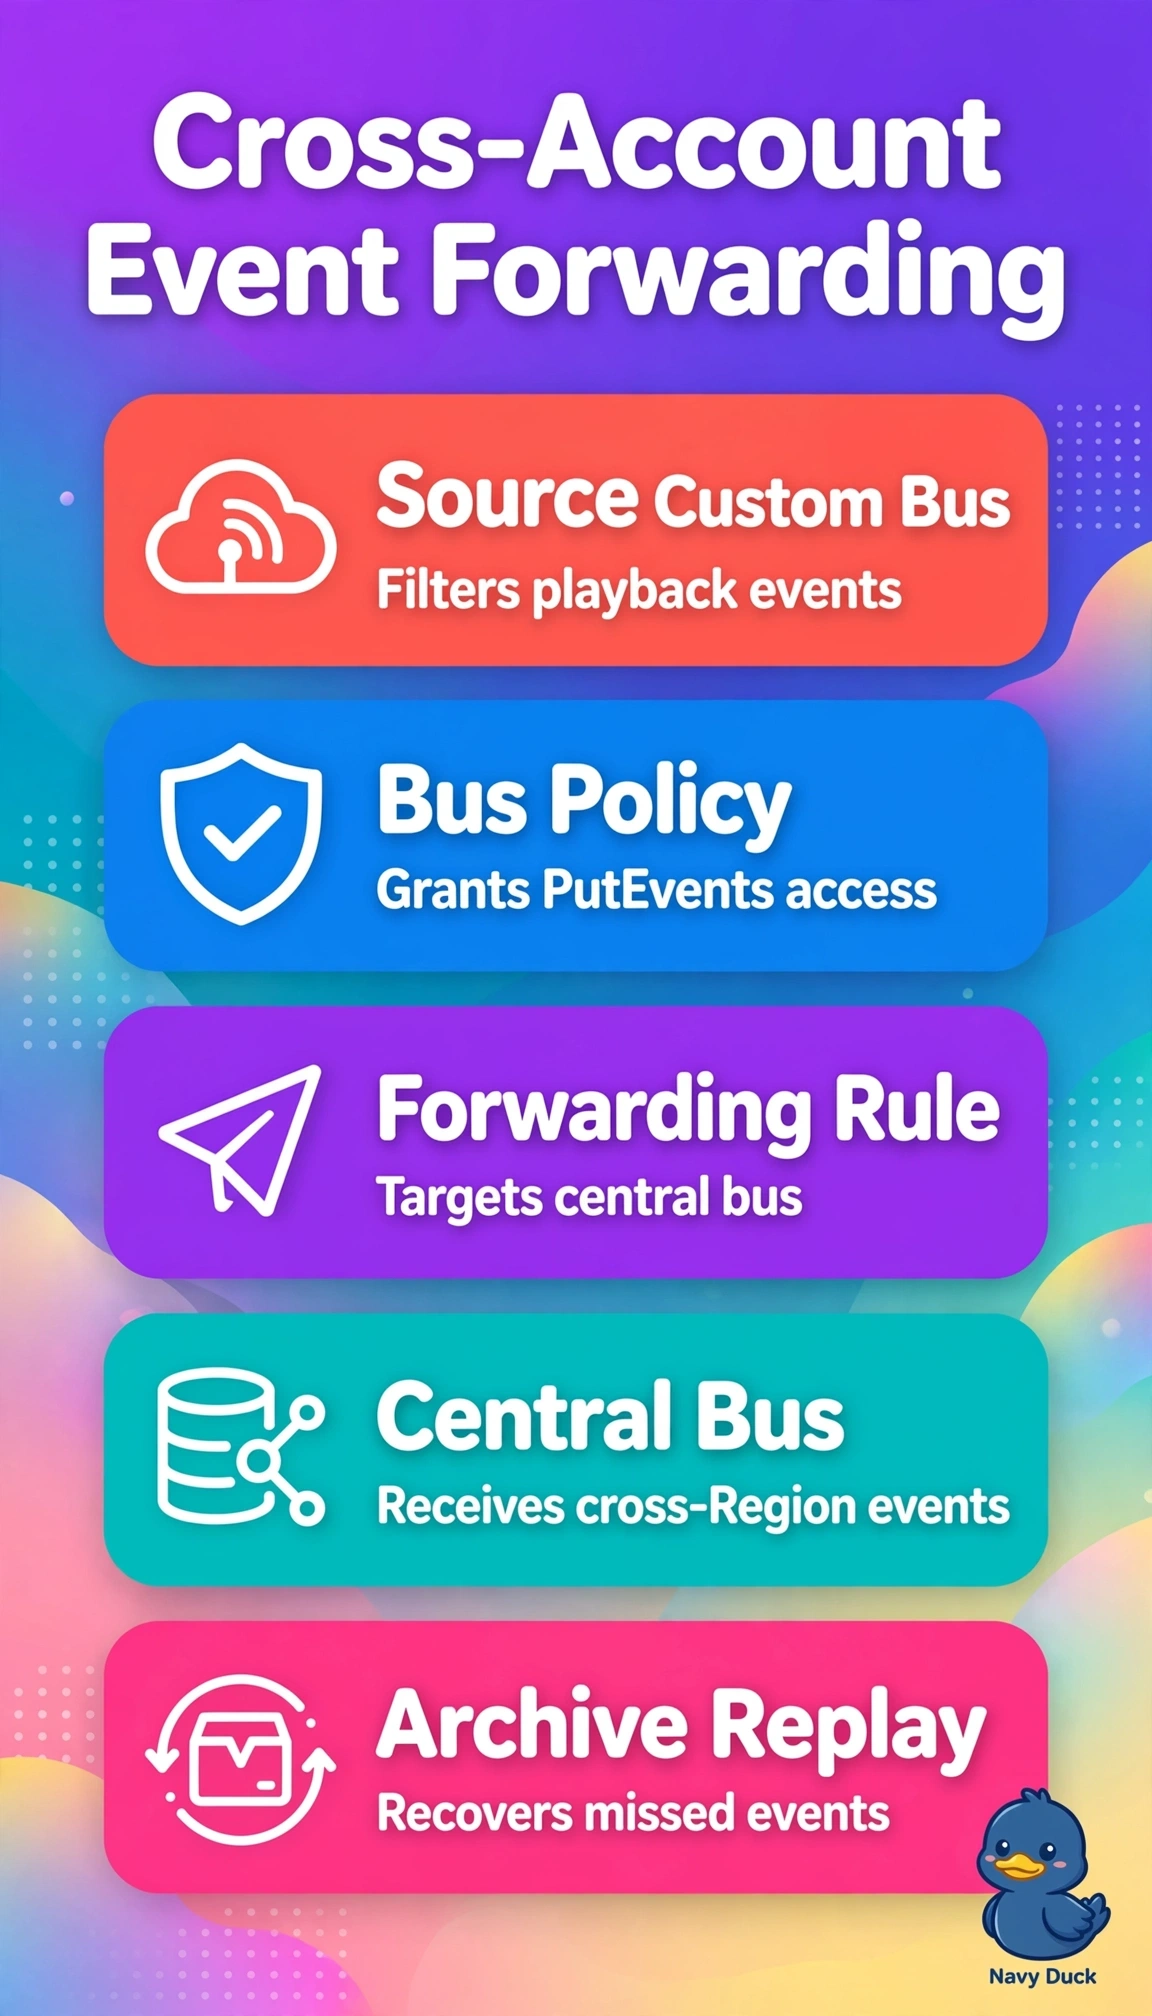
You can keep this route private and tightly authorized across accounts and Regions. A scoped resource policy plus archiving lets filtered events reach the custom bus and be replayed if delivery is missed.
Full Explanation
The pattern with a scoped resource policy on the eu-west-1 analytics custom bus and a filtered production rule targeting that bus with archiving meets the requirements. The policy authorizes PutEvents only for the ap-southeast-2 production account or role, preserving least privilege; cross-Region bus delivery uses the AWS backbone without exposing the bus to the public internet. Archiving on the receiving bus retains events so you can replay them after an outage. The policy-and-rule design without archiving provides secure, filtered live delivery, but retains no history for replay if events are missed. Allowing every organization account to write is broader than least privilege and could admit unwanted or spoofed events, even with filtering and archiving. Forwarding to the central default bus does not meet the requirement to use the custom analytics bus and loses its workload separation and fine-grained governance. Exam caveat: check that the destination is the required custom bus, not merely a bus in the correct account and Region. As a practical check, verify the policy principal, test the playback-event filter, confirm archive retention, and run a small replay to the audit target.