
A regional retailer deploys storefront services with AWS CDK pipelines to dev, staging, and production, and developers currently commit encrypted database strings in code that block rotation and expose values in diffs. The team needs versioned secrets per environment, automatic rotation for RDS, and no plaintext in templates or logs. Which secrets management approach secures infrastructure code for these environments?
Select an answer to reveal the explanation.
Short Explanation
Your recipes shouldn't list the safe combination in the margins. Dynamic references pull the right secret at deploy time while rotation happens behind the scenes without code changes.
Full Explanation
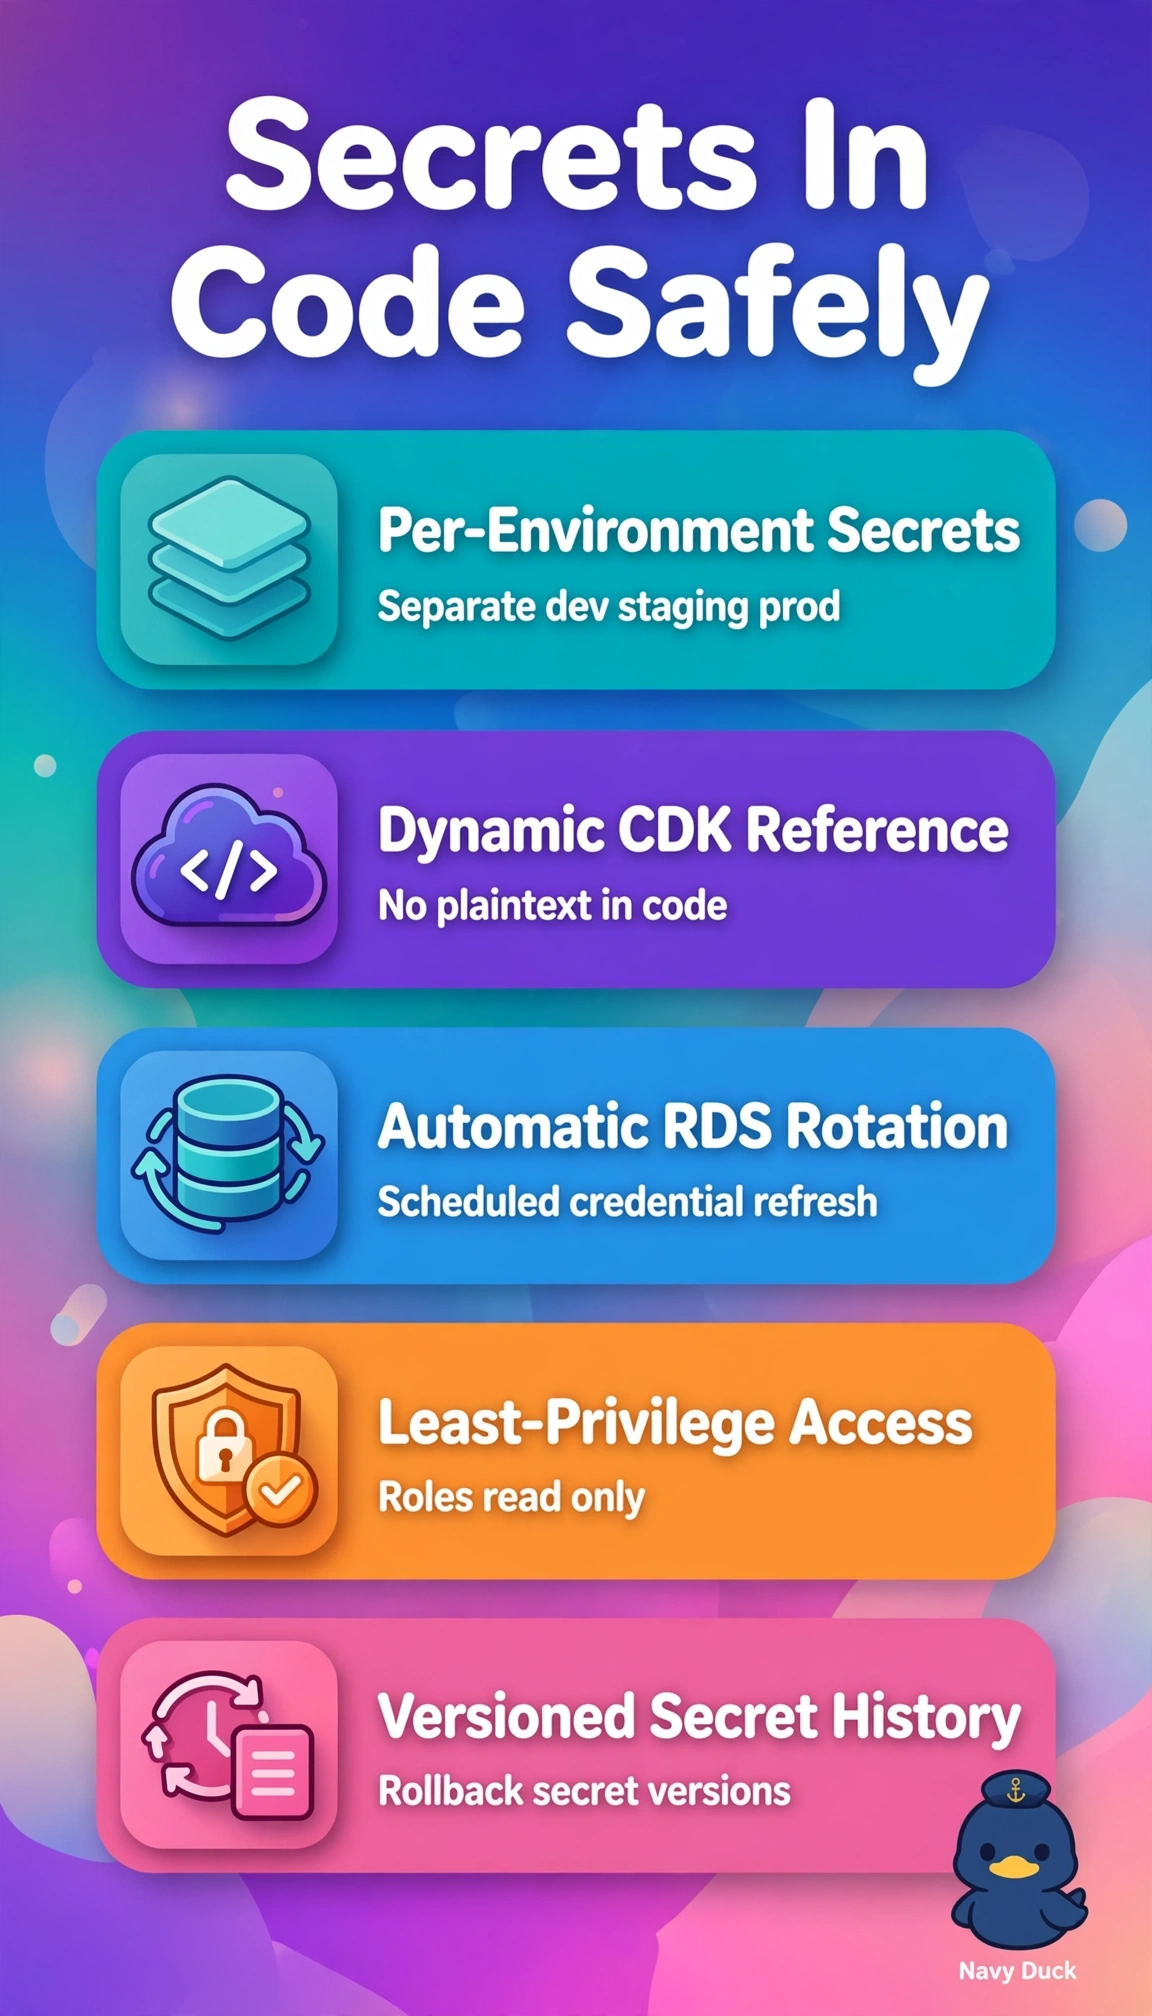
The correct approach works because isolated Secrets Manager secrets per environment give independent versioning rollback and audit scope, dynamic references preserve secrets as unresolved tokens until CloudFormation deployment so values never enter CDK source synthesized templates diffs or pipeline logs, built-in RDS rotation automates credential rollover via managed Lambda without redeploying code, and environment-scoped least-privilege IAM prevents cross-stage access. The Parameter Store SecureString hierarchy with KMS encryption and dynamic lookup is a legitimate pattern for hierarchical configuration but fails on concept because it has no native RDS rotation orchestration and limited secret version staging, forcing custom automation and missing the stated managed rotation need. The centrally managed secret with automatic rotation and dynamic lookup for all stages is efficient for small workloads but fails on isolation because one lifecycle spans dev staging and production, so versioning promotion and blast radius cannot be separated and a single rotation impacts every environment. The synthesis-time retrieval pattern with per-environment secrets and rotation preserves organization yet fails on confidentiality by resolving values during synth into stack properties, embedding plaintext in templates context and detailed logs instead of deferring resolution to deploy time. As an exam caveat, encryption alone does not equal managed rotation, so prioritize rotation keywords when choosing between Parameter Store and Secrets Manager, and as a practical check inspect cdk synth output for secretsmanager dynamic references and verify rotation status plus IAM policies limited per environment.