
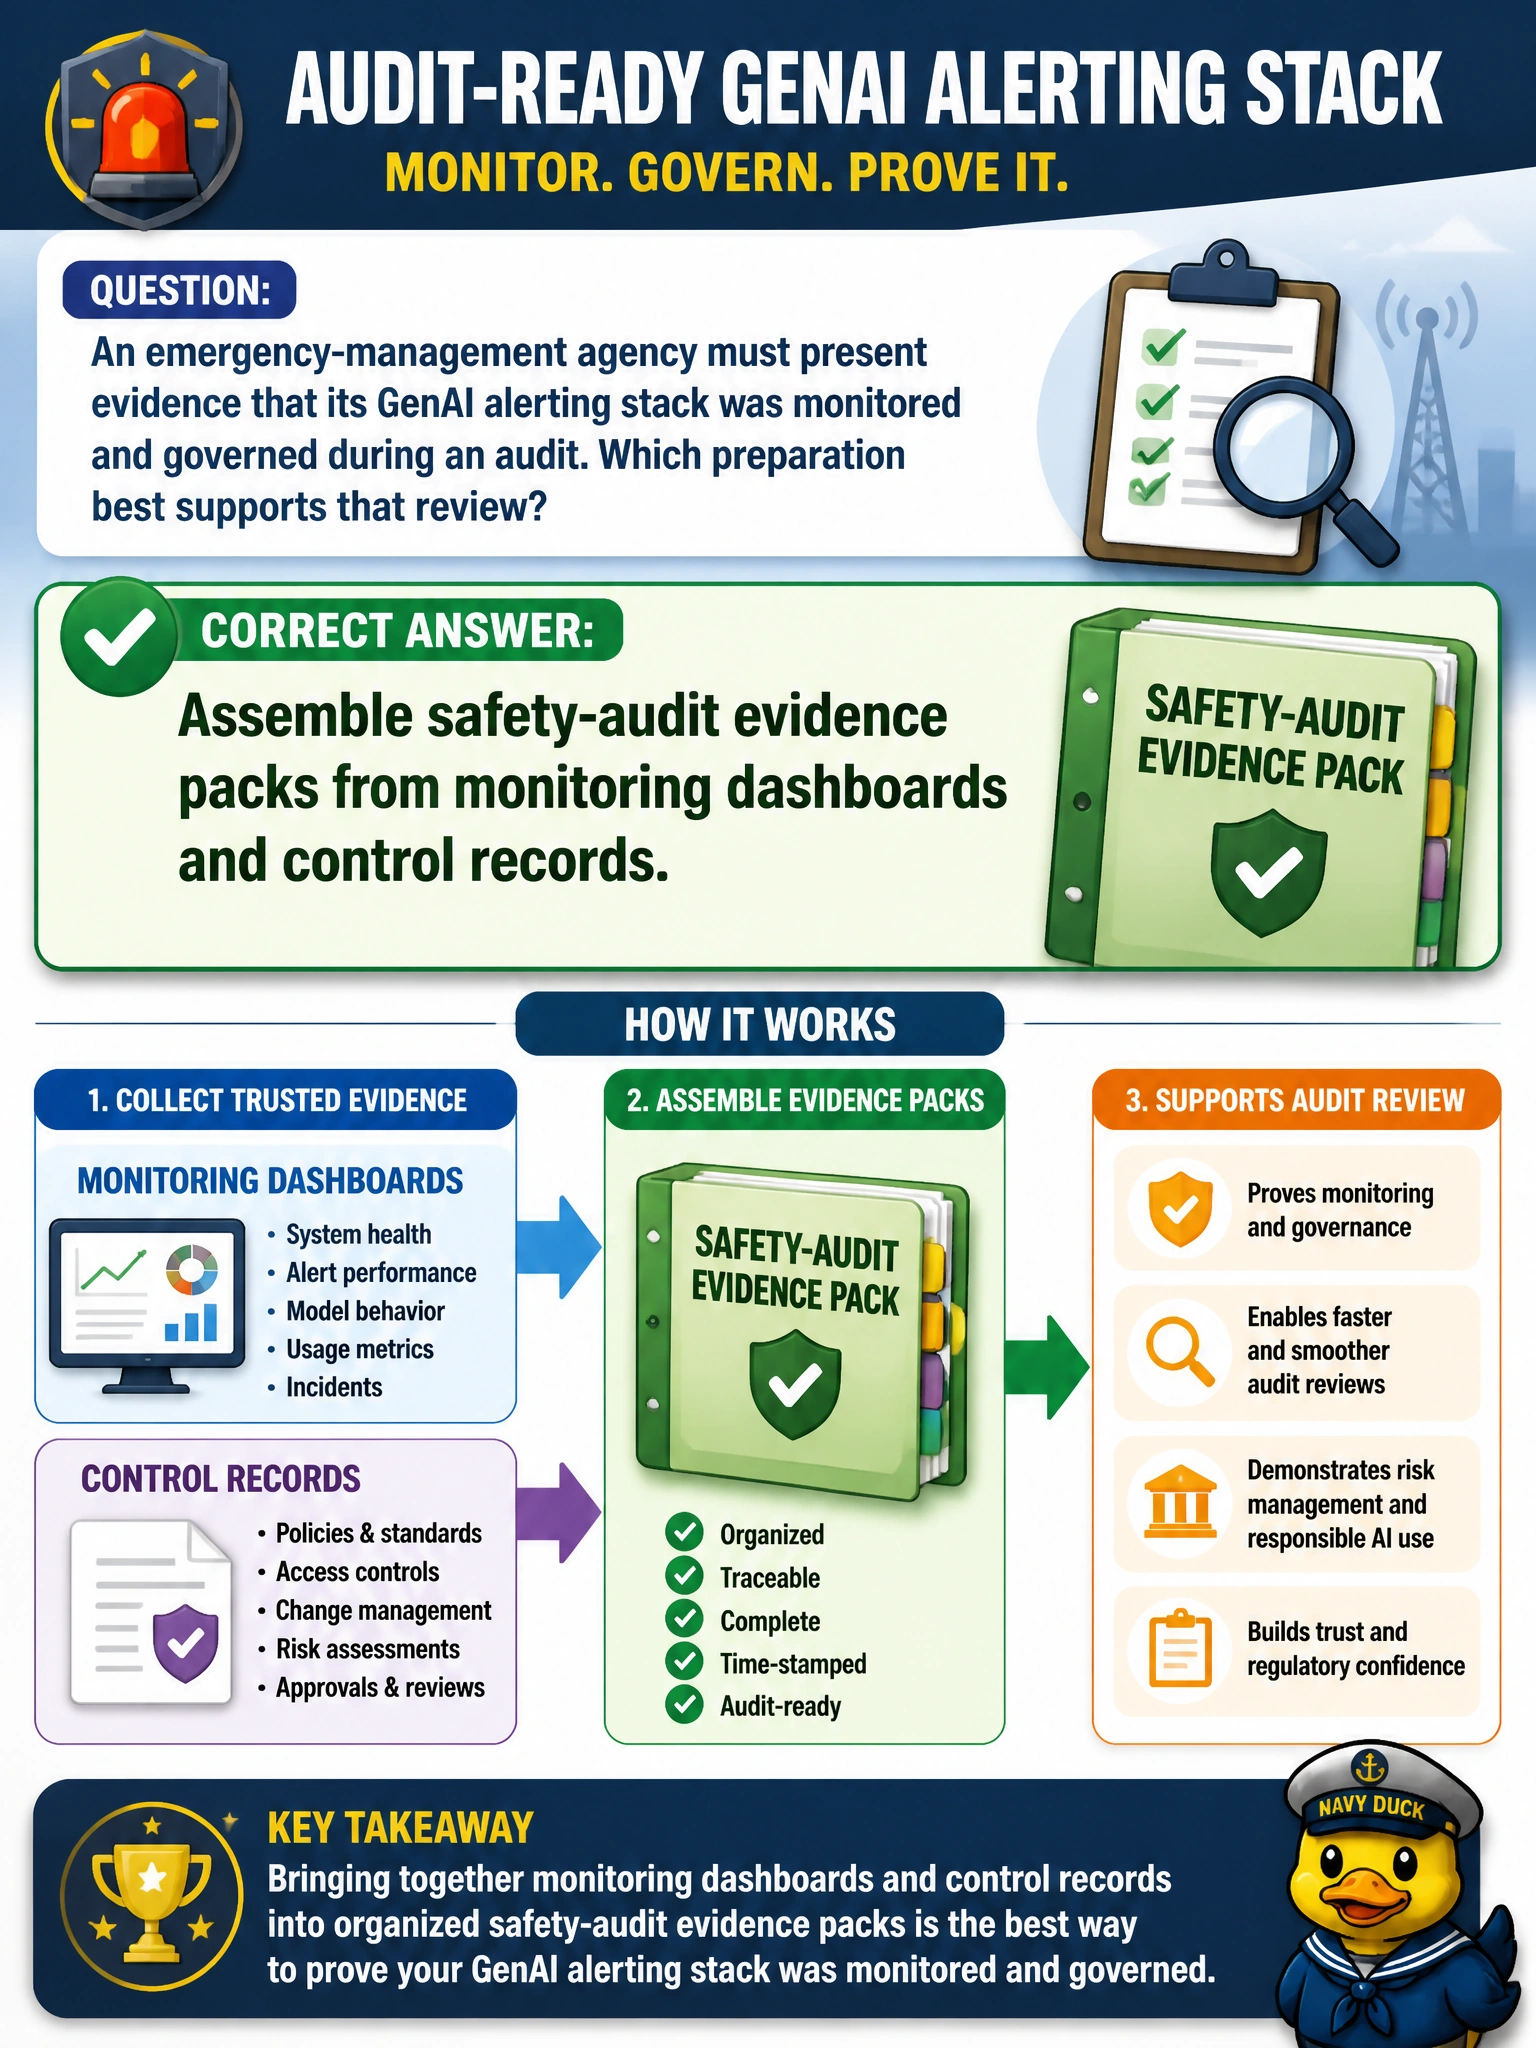
An emergency-management agency must present evidence that its GenAI alerting stack was monitored and governed during an audit. Which preparation best supports that review?
Select an answer to reveal the explanation.
Short Explanation
Auditors want the binder, not the pep talk. Pull evidence packs from the monitoring dashboards and control history so emergency-management GenAI can show what was watched, when, and how issues were handled.
Full Explanation
Assembling safety-audit evidence packs from monitoring dashboards and control records best supports an emergency-management agency that must present evidence its GenAI alerting stack was monitored and governed during an audit. Evidence packs typically include exported metrics, alert histories, incident tickets, guardrail configurations, access reviews, and change logs covering the audit period. Reviewers need artifacts, not assurances—packaging dashboard exports and control records demonstrates that monitoring existed continuously and that governance actions were recorded.
Providing only marketing screenshots with no metrics or control history fails evidentiary standards. Claiming continuous monitoring verbally without exporting supporting artifacts leaves auditors nothing to verify. Wiping dashboards before auditors arrive destroys evidence and signals control failure rather than simplifying the story.
Exam caveat: audit readiness for GenAI safety/governance is about exportable evidence from operational monitoring and control systems. Screenshots and verbal claims are classic incorrect distractors.
Operational check: define an evidence-pack checklist for the emergency GenAI alerting stack, schedule periodic exports (metrics, alerts, configs), store packs in an immutable or write-once audit bucket, rehearse retrieval before real audits, and never delete monitoring history to “clean up” for reviewers.