
Your multi-agent pipeline has five worker agents that each require access to different external APIs (database, search, calendar, email, file storage). The team is debating whether each agent should have its own tool set or whether all agents should have access to all tools. What is the architecturally correct approach and why?
Select an answer to reveal the explanation.
Short Explanation
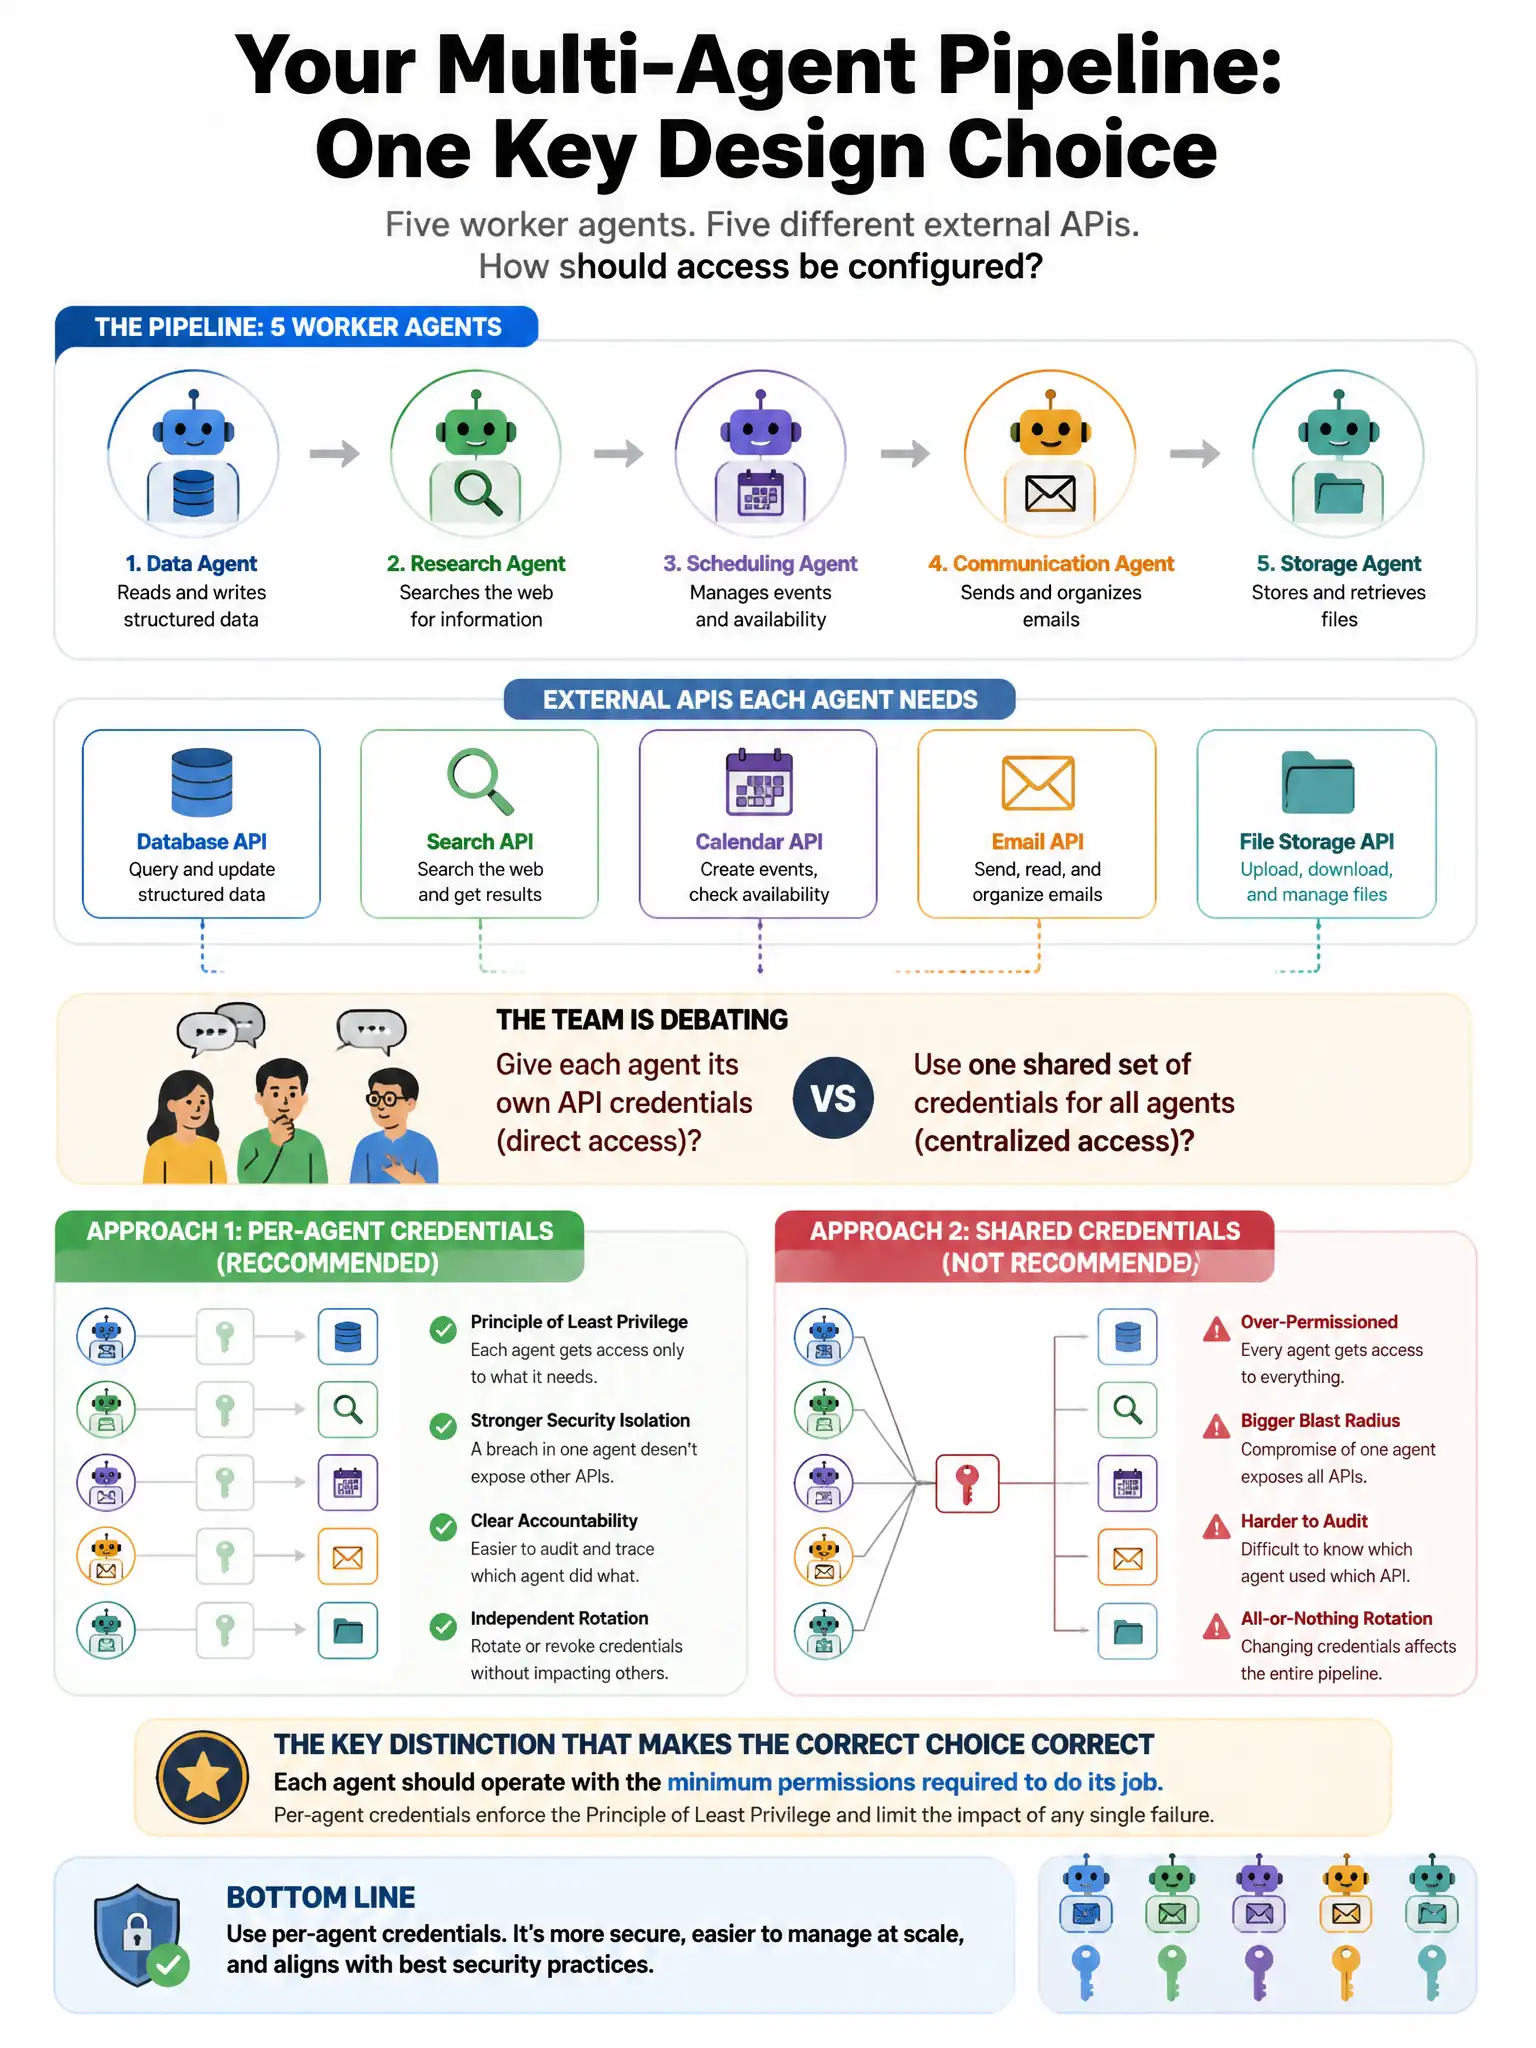
Here's the deal — give each agent only the tools it actually needs. That least-privilege setup limits the blast radius if an agent fails, misreads a task, or gets hit by prompt injection. The search agent can't touch email if you never gave it email tools.
Full Explanation
Least-privilege tool assignment is the architecturally correct approach because it is the fundamental security principle for agent systems. Restricting each agent to only its required tools limits the blast radius of any agent failure, misinterpretation, or prompt injection — a compromised search agent cannot access the email API if it was never given email tools. This also makes agent behavior more predictable and auditable, while the orchestrator can manage cross-agent coordination without handing every worker every capability. The all-tools approach is wrong because Claude's safety training reduces but does not eliminate misuse risk, and giving all agents all tools creates unnecessary attack surface; the self-recovery argument is a rationalization that trades security for marginally improved fault tolerance. The shared tool broker approach is wrong because audit logging and rate limiting address auditability and operational control but not least-privilege — an agent with access to all tools through a broker can still misuse any of them. The progressive-access approach is wrong because granting progressively broader access to later pipeline stages is an anti-pattern; it creates a high-privilege execution context for agents operating on already-processed, potentially attacker-influenced data, which is exactly backwards from least-privilege principles.