
A community bike-barn board’s insurer asks for AWS’s own SOC-style package, not a homemade screenshot. Which service supplies that report?
Select an answer to reveal the explanation.
Short Explanation
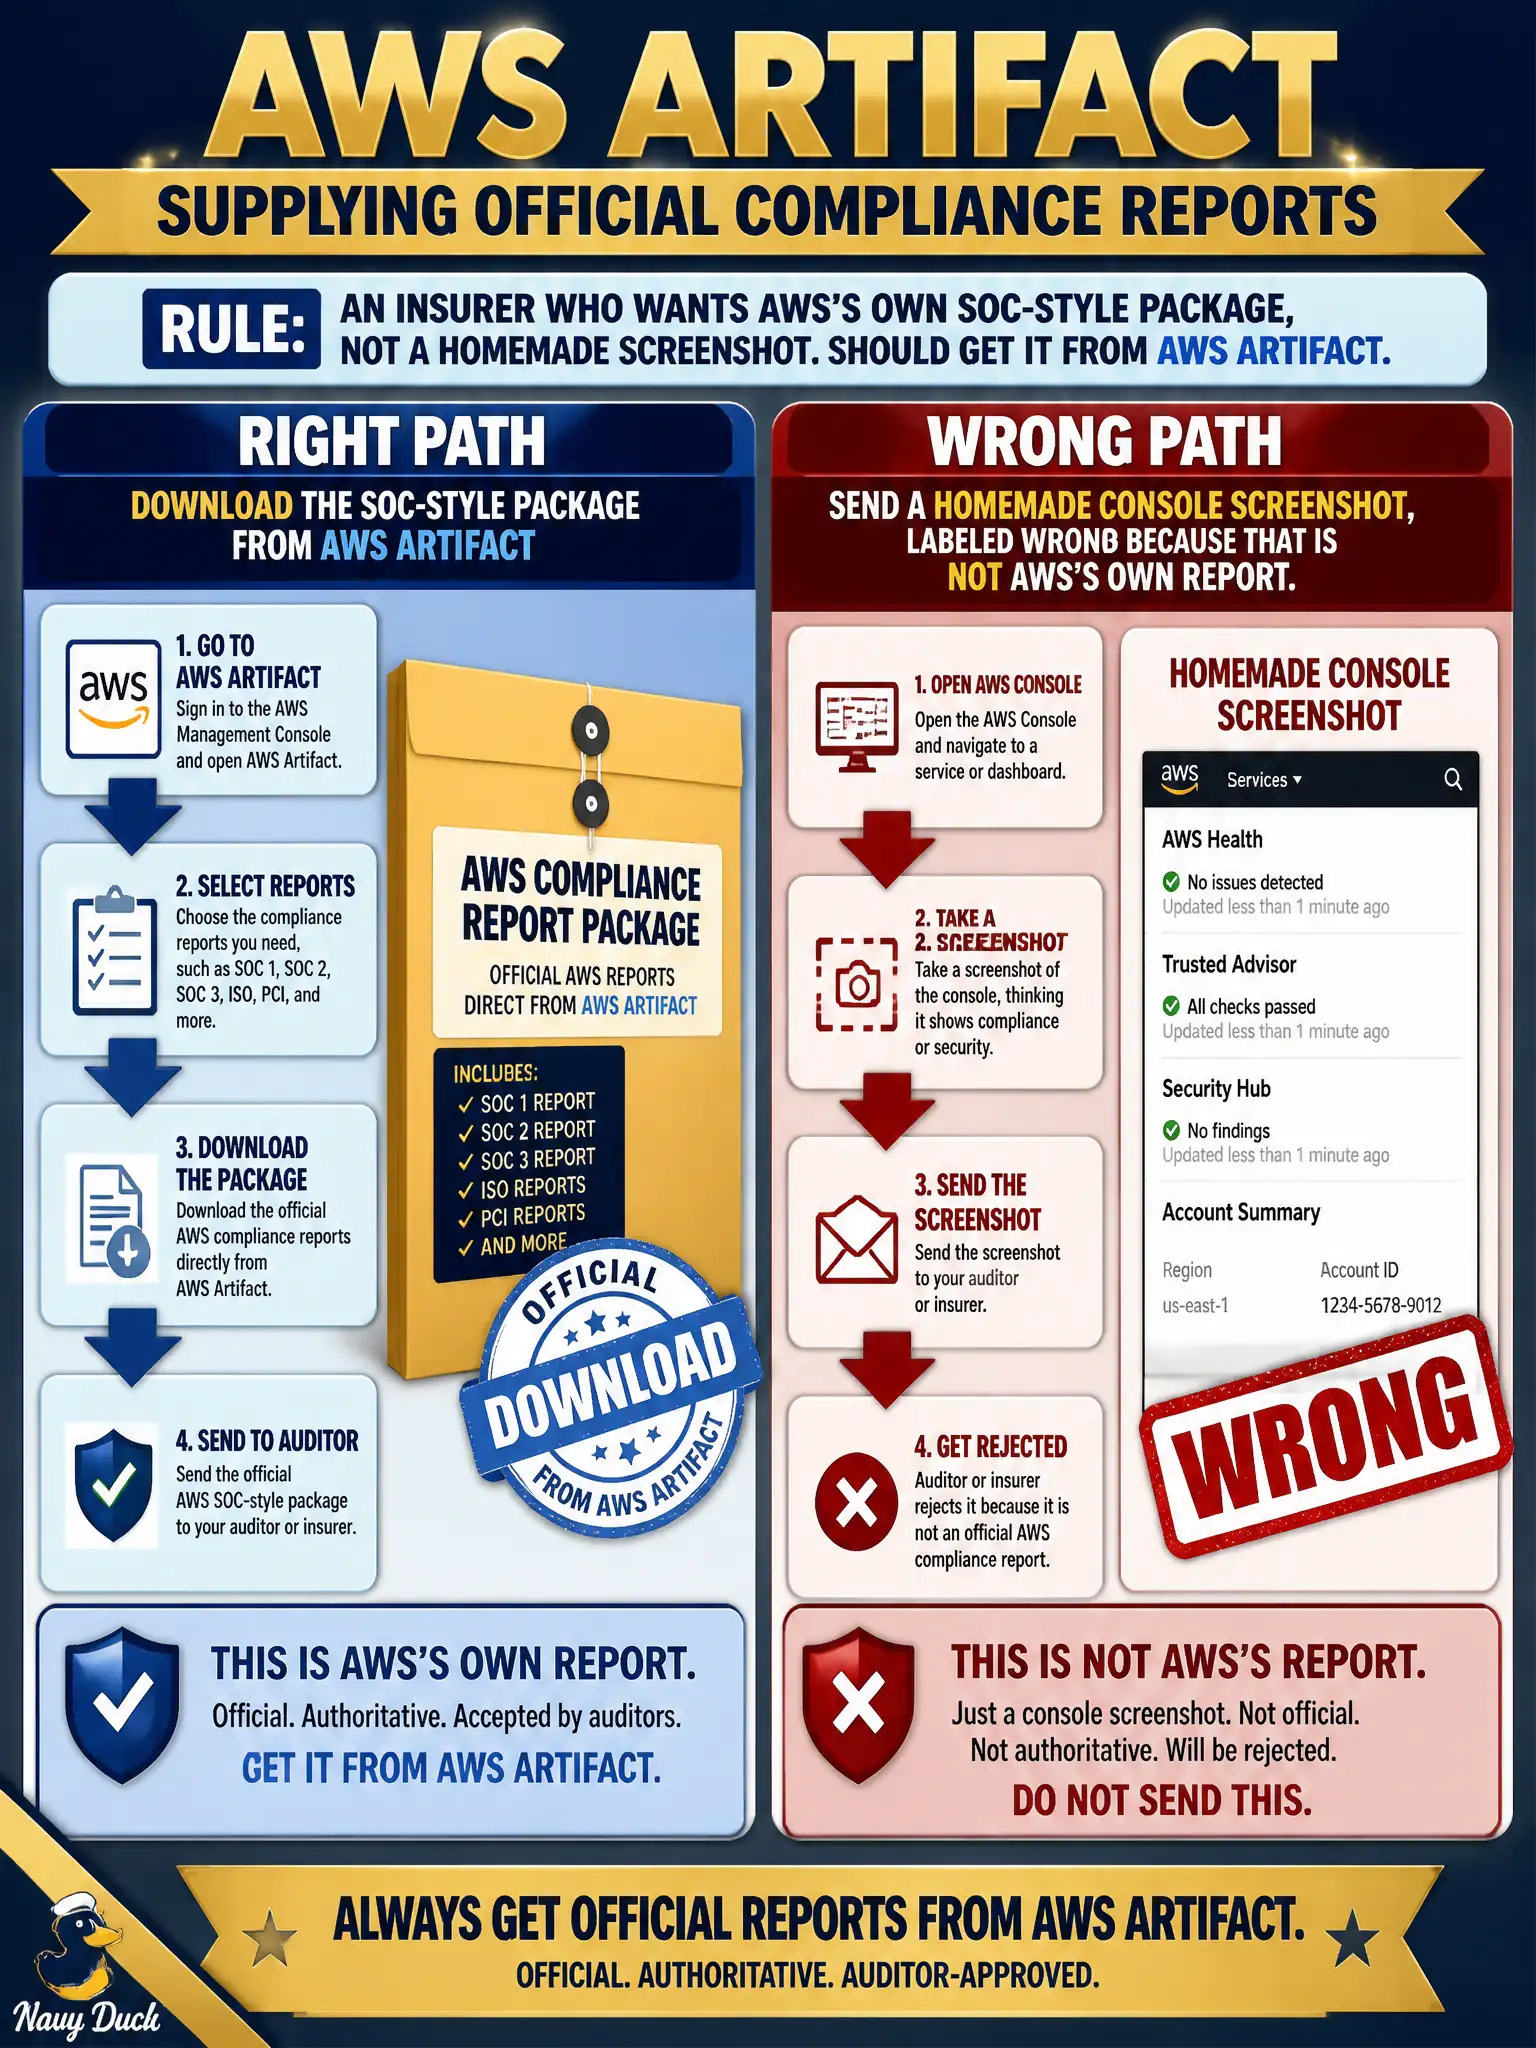
Think of an insurer who wants AWS’s own SOC-style package, not a homemade screenshot. AWS Artifact is where that report lives. Polly and a shop-written HIPAA plan are not that download.
Full Explanation
When the bike-barn board’s insurer asks for AWS’s own SOC-style package rather than a homemade screenshot, the download comes from AWS Artifact. Artifact distributes AWS compliance reports and agreements so auditors can review the provider’s controls. That is the correct source when the request is for AWS’s attestation package, not for the barn’s internal evidence of how it configured AI helpers.
A homemade console screenshot fails by concept: it is customer evidence at best, not AWS’s SOC package, and insurers typically reject it as a substitute. Amazon Polly fails because speech synthesis does not produce audit reports. Writing a HIPAA implementation plan from scratch instead of Artifact fails when the ask is specifically for AWS’s own SOC-style package; a shop-written plan may still be needed for the barn’s responsibilities, but it does not replace Artifact downloads.
Exam caveat: Artifact shows AWS’s controls; the customer remains responsible for how they configure Bedrock, buckets, and access in their account. Operational check: sign in with an authorized role, download the requested report family from Artifact, store it in the insurer’s evidence folder with access controls, and separately attach the barn’s configuration evidence for AI workloads.