
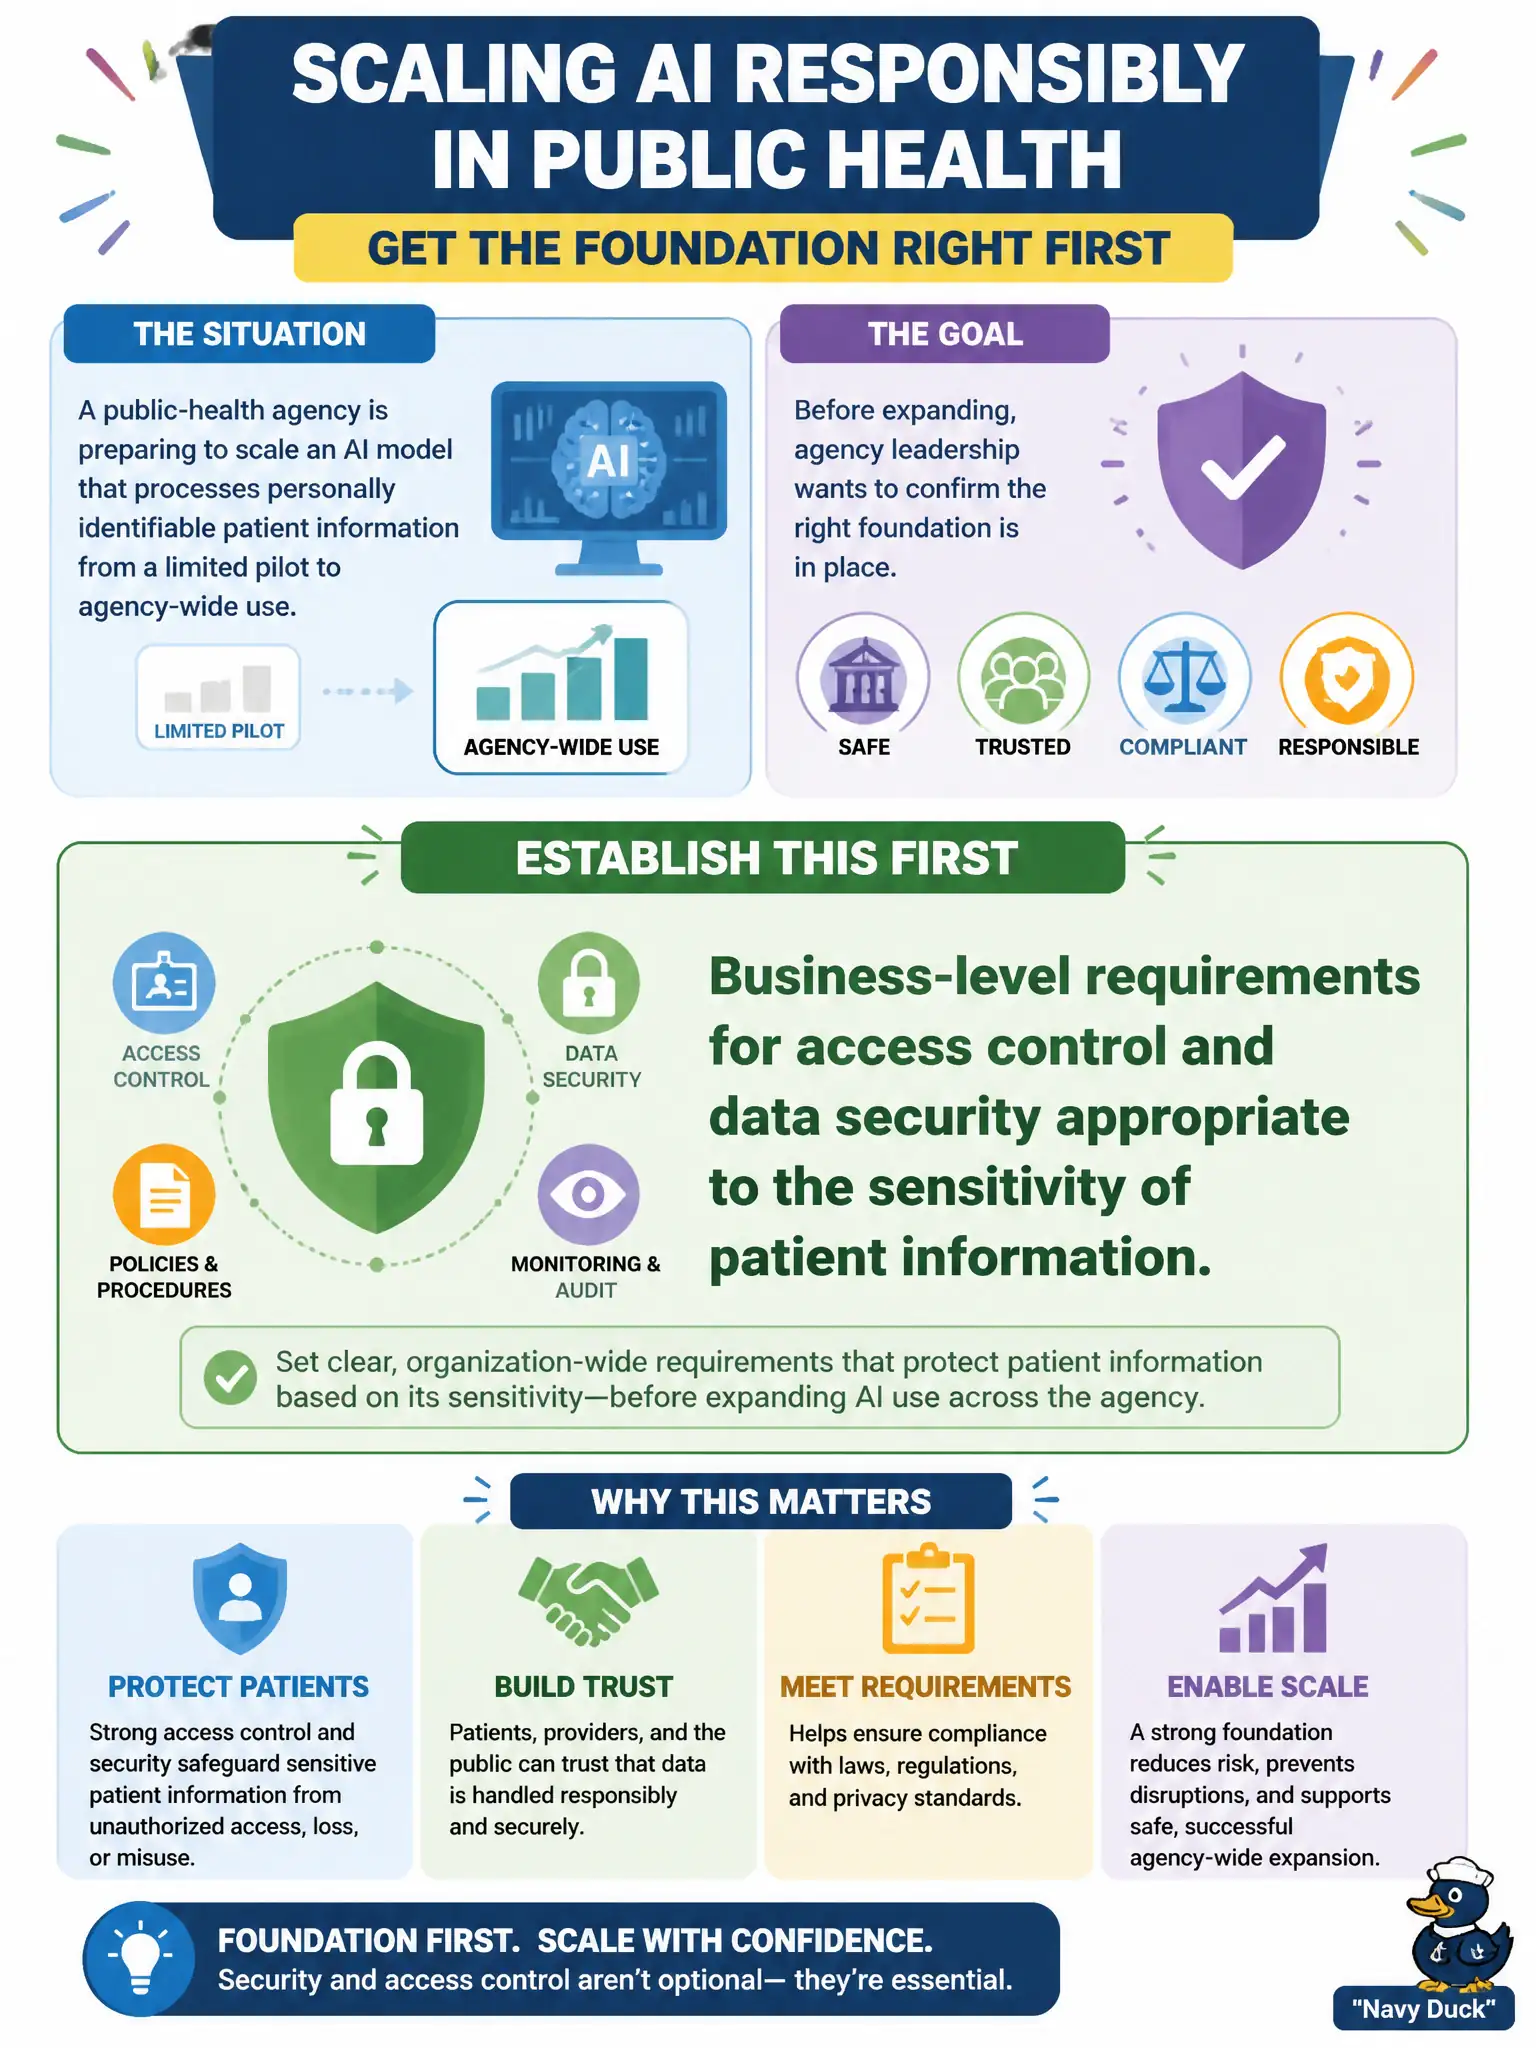
A public-health agency is preparing to scale an AI model that processes personally identifiable patient information from a limited pilot to agency-wide use. Before expanding, agency leadership wants to confirm the right foundation is in place. What should they establish first?
Select an answer to reveal the explanation.
Short Explanation
Think of scaling a pilot like moving a small clinic's records into a hospital-wide system, the locks that were good enough for one file cabinet aren't good enough for the whole records room. Before the agency touches more patient data, leadership needs to define the security and access rules the expansion demands, at the business level, not just the engineering level. Everything else can wait until that foundation is set.
Full Explanation
Scaling an AI system that handles personally identifiable patient information multiplies both the volume of sensitive data at risk and the number of people who can potentially reach it, so leadership's first job is to define business-level requirements for access control and data security proportional to that sensitivity, things like who may view what, under what conditions, and with what audit trail. That decision belongs to leadership because it sets the risk tolerance and compliance posture the technical team then implements; it isn't itself a configuration task. A technical runbook of screens to click is a step below this decision, it assumes the underlying security requirements were already defined and simply documents how to execute them. A marketing plan addresses public communication, a concern that matters later but does nothing to protect the data itself. A fixed retraining schedule decided before any monitoring data exists puts a process detail ahead of the more urgent question of who can access sensitive records safely at scale. This guidance applies specifically to expansions involving PII or other sensitive categories; a pilot scaling with fully de-identified data would carry a lower bar. A useful operational check is confirming a written access-control policy exists and maps to the new scale before granting any additional system access.