
A school district is defining an access-control policy for who may query a student-data GenAI assistant that can surface information like grades, attendance, and behavioral notes. What access-control approach should the district's leadership adopt?
Select an answer to reveal the explanation.
Short Explanation
Think about how a school's paper student files were never left out in a shared filing cabinet open to every employee, a hall monitor didn't get to page through a student's therapy notes just because the cabinet was in the building. A GenAI assistant surfacing that same sensitive data needs the same logic: access scoped to what a person's actual job requires, not to everyone with a login.
Full Explanation
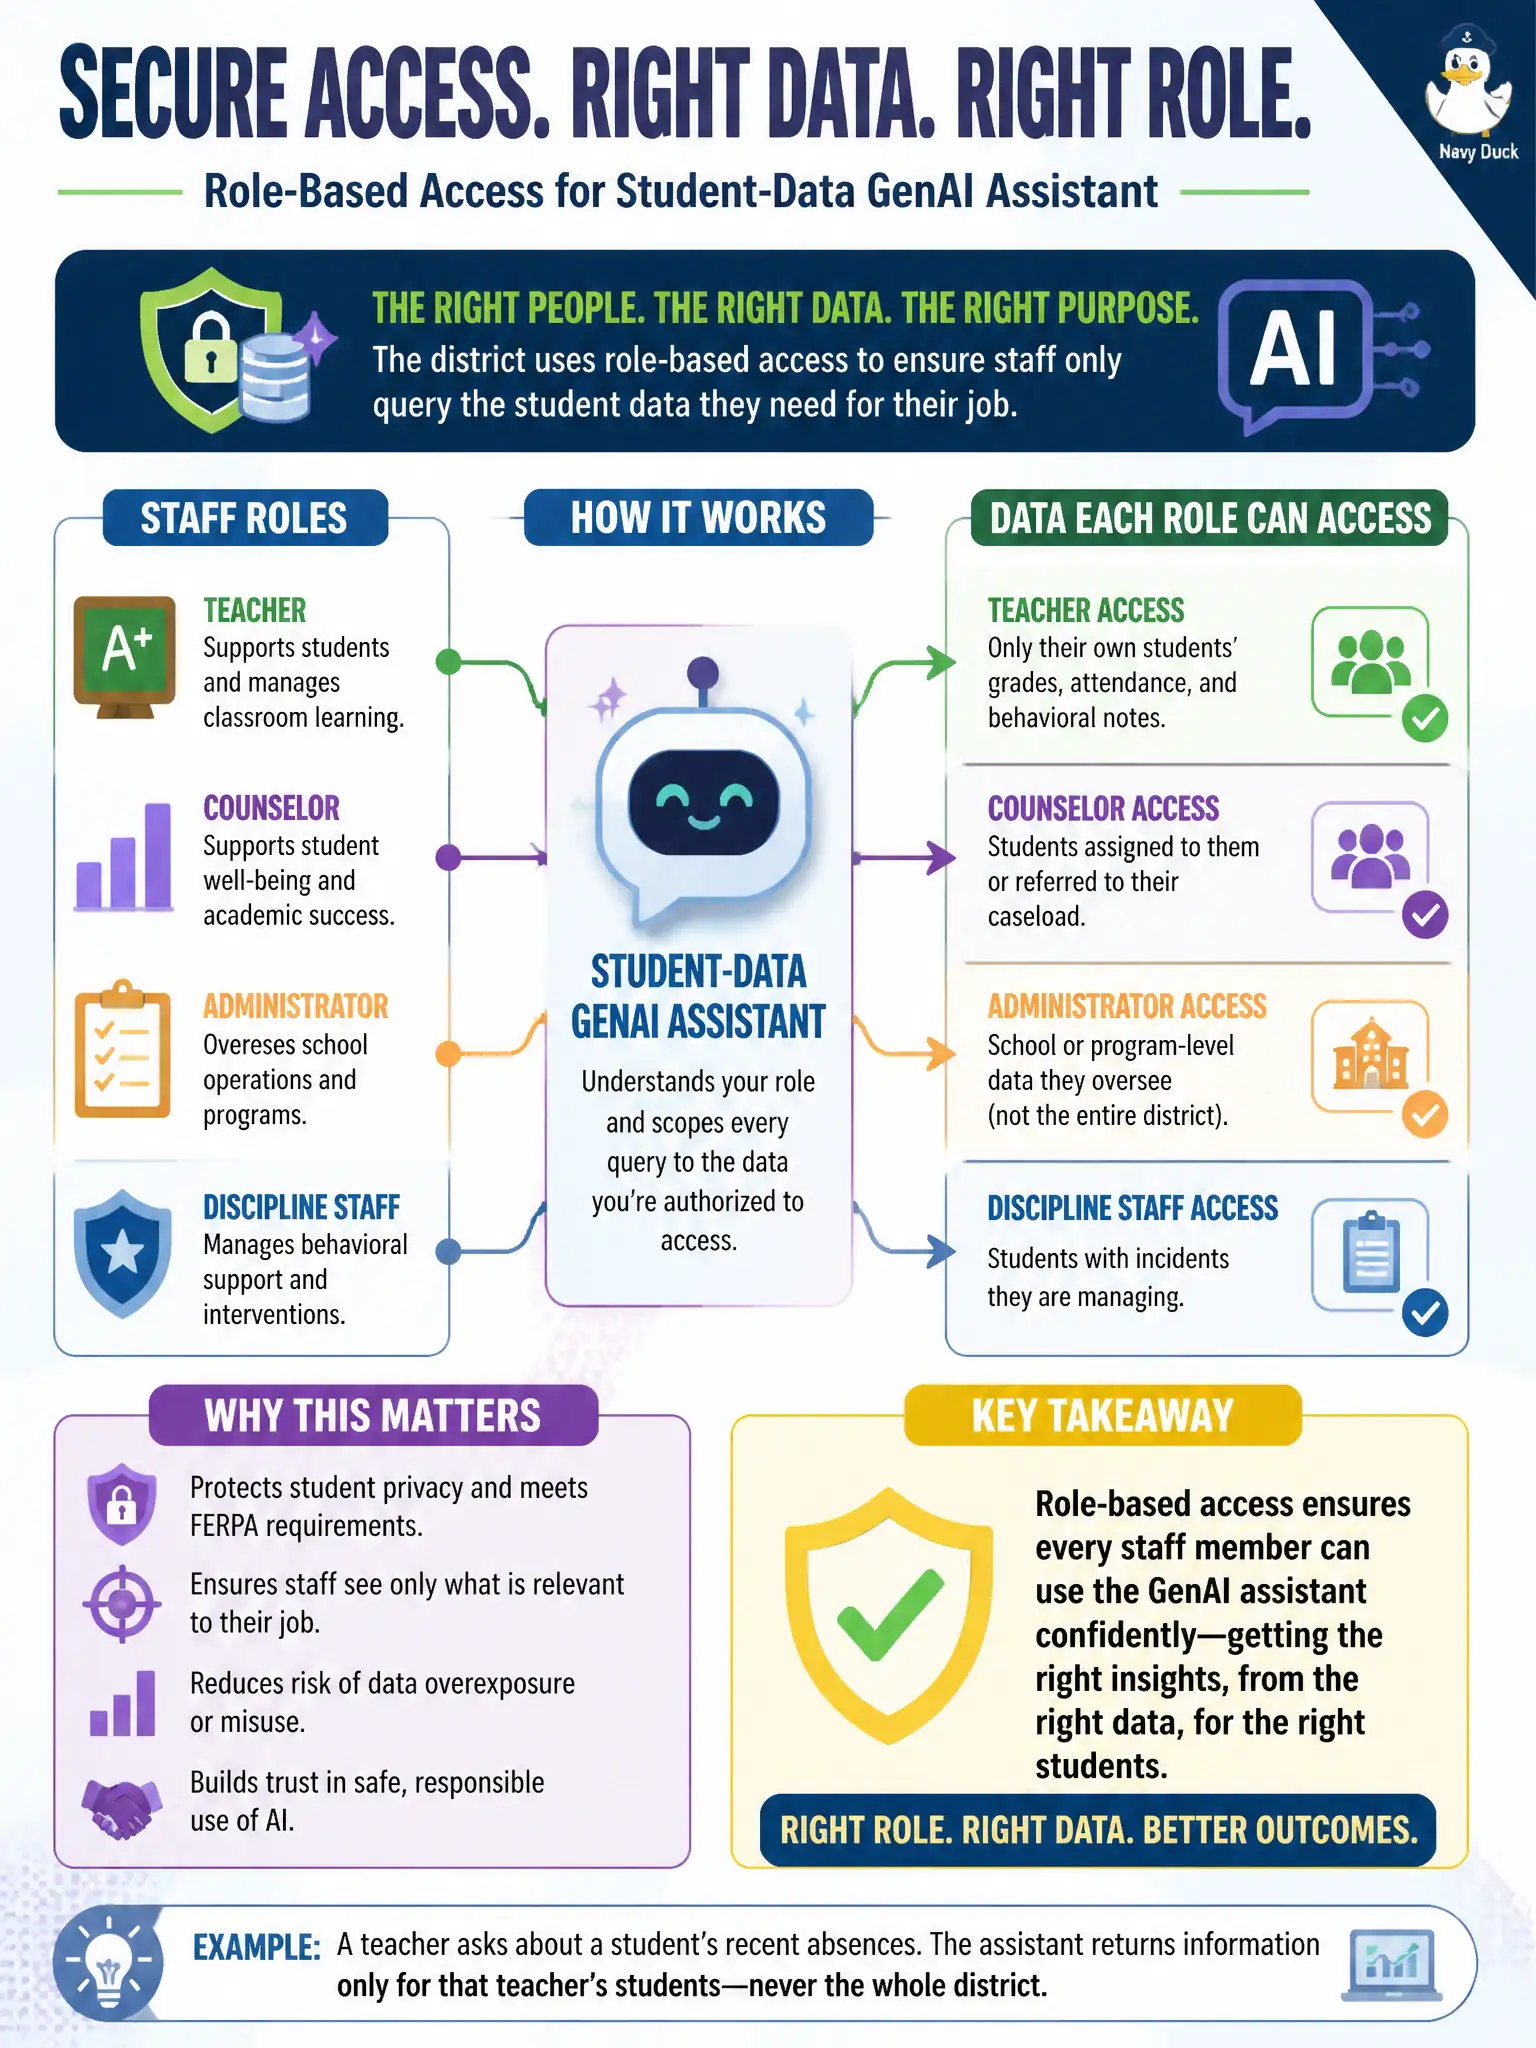
Role-based access control scopes each staff member's ability to query the assistant to the student data genuinely relevant to their job function, such as a teacher seeing their own students' records rather than the entire district's roster, which limits exposure of sensitive information like behavioral notes to only those with a legitimate need. Granting open access to all staff for the sake of operational speed ignores that student-privacy expectations require limiting who can view sensitive records regardless of how convenient broad access might be, and a breach or misuse risk grows substantially wider with every additional person who has unrestricted query ability. Restricting access solely to IT administrators solves the wrong problem, since IT staff typically don't need substantive access to student academic and behavioral content to do their jobs, while the staff who do need it, teachers and counselors, would be locked out entirely. Granting broad access based on completing a training course conflates general AI literacy with an actual need-to-know basis for specific student data, since knowing how to use an AI tool responsibly doesn't establish that a given staff member has a legitimate reason to query every student's record. A scope caveat: role definitions should be reviewed periodically as staff roles change, since a stale role assignment can quietly become an access-control gap. A concrete check: audit a sample of the assistant's query logs against staff role assignments to confirm no one is retrieving student data outside their defined scope.