
A city security team creates a new Vault master key for permit archives and must choose protection mode. Which statement is accurate?
Select an answer to reveal the explanation.
Short Explanation
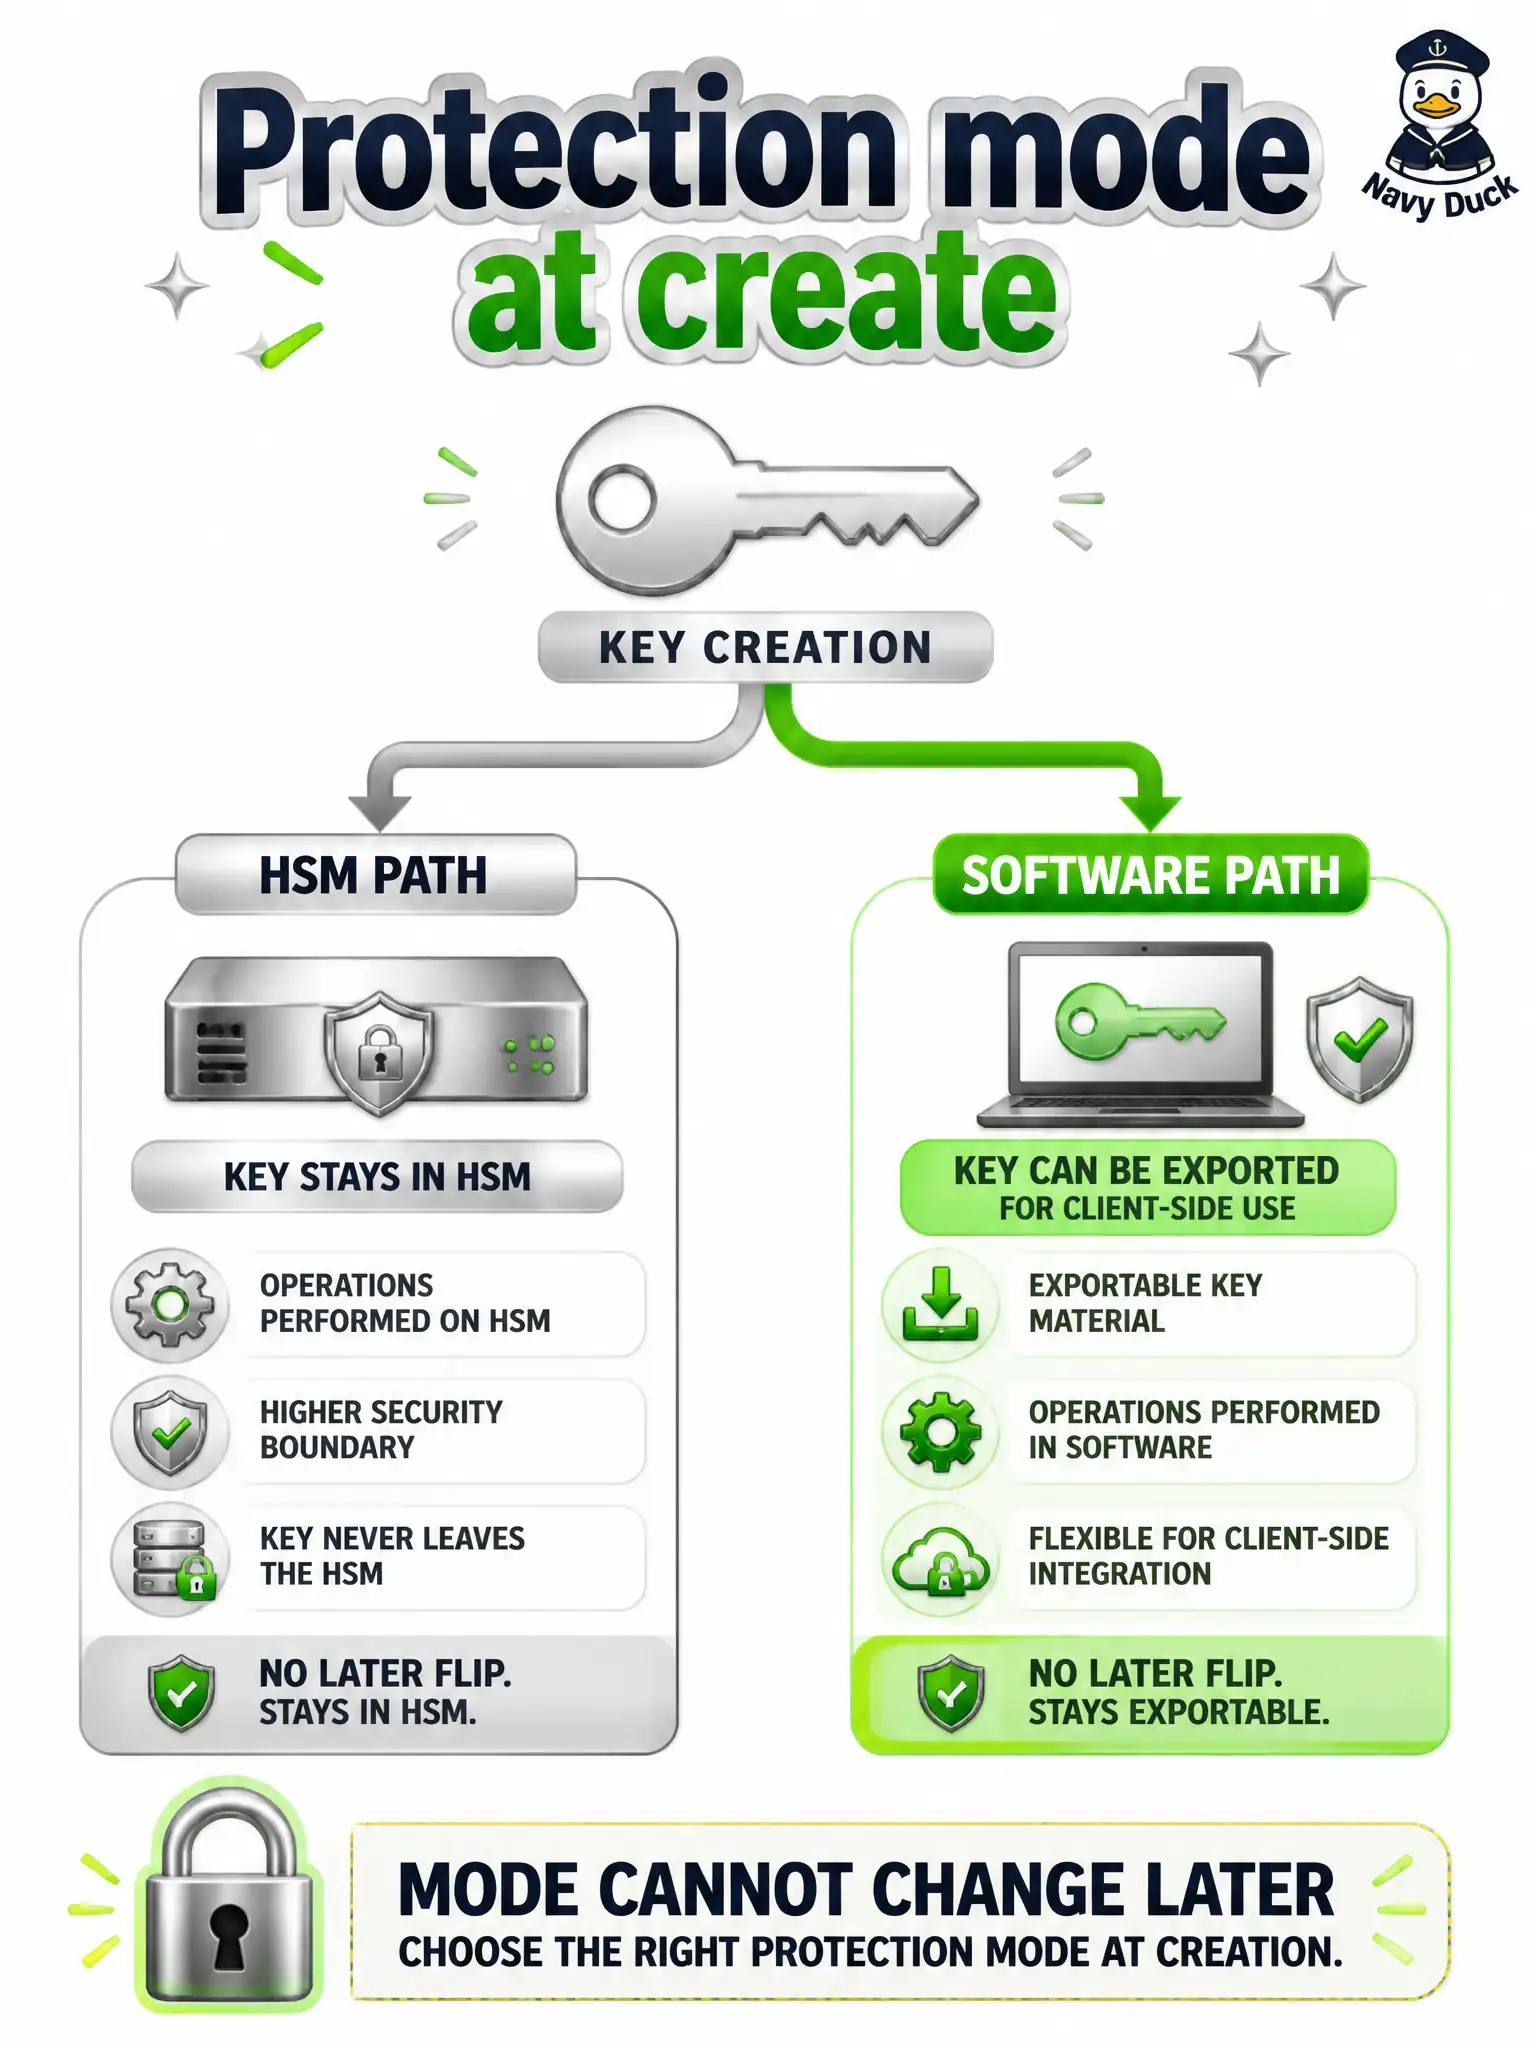
Pick HSM or software when the key is born—that choice sticks. HSM keeps the work on the HSM; software keys can be exported for client-side crypto. Pricing and exportability follow the mode.
Full Explanation
Vault master-key protection mode is chosen at create time for permit-archive keys and does not flip later. HSM-protected material keeps cryptographic operations on the HSM; software-protected keys can be exported for client-side cryptographic use cases. Pricing, exportability, and where crypto executes follow that mode, so the city security team must pick HSM versus software when the key is born based on compliance and export needs.
Claiming protection mode can be flipped freely between HSM and software after create with no recreate fails by concept: the mode is immutable for that key’s lifetime; a new key is required to change posture. Saying software-protected keys never encrypt anything and exist only as display labels fails—software-protected keys are usable for crypto and are the exportable path when client-side use is required. Claiming HSM mode is available only through Dedicated KMS and cannot be selected on a standard vault key fails as an over-restriction: protection mode is a key create-time choice on vault keys, not a claim that HSM exists only behind a different product SKU invented for the distractor.
Exam caveat: protection mode is create-time immutable—plan HSM vs software before create. Operational check: create a software-protected test key and confirm export is possible for a sanctioned client-side proof; create an HSM-protected key and confirm crypto stays on the HSM and mode cannot be edited to software in the console or API.