
After fn deploy, where does OCI Functions obtain the container image it runs for a function?
Select an answer to reveal the explanation.
Short Explanation
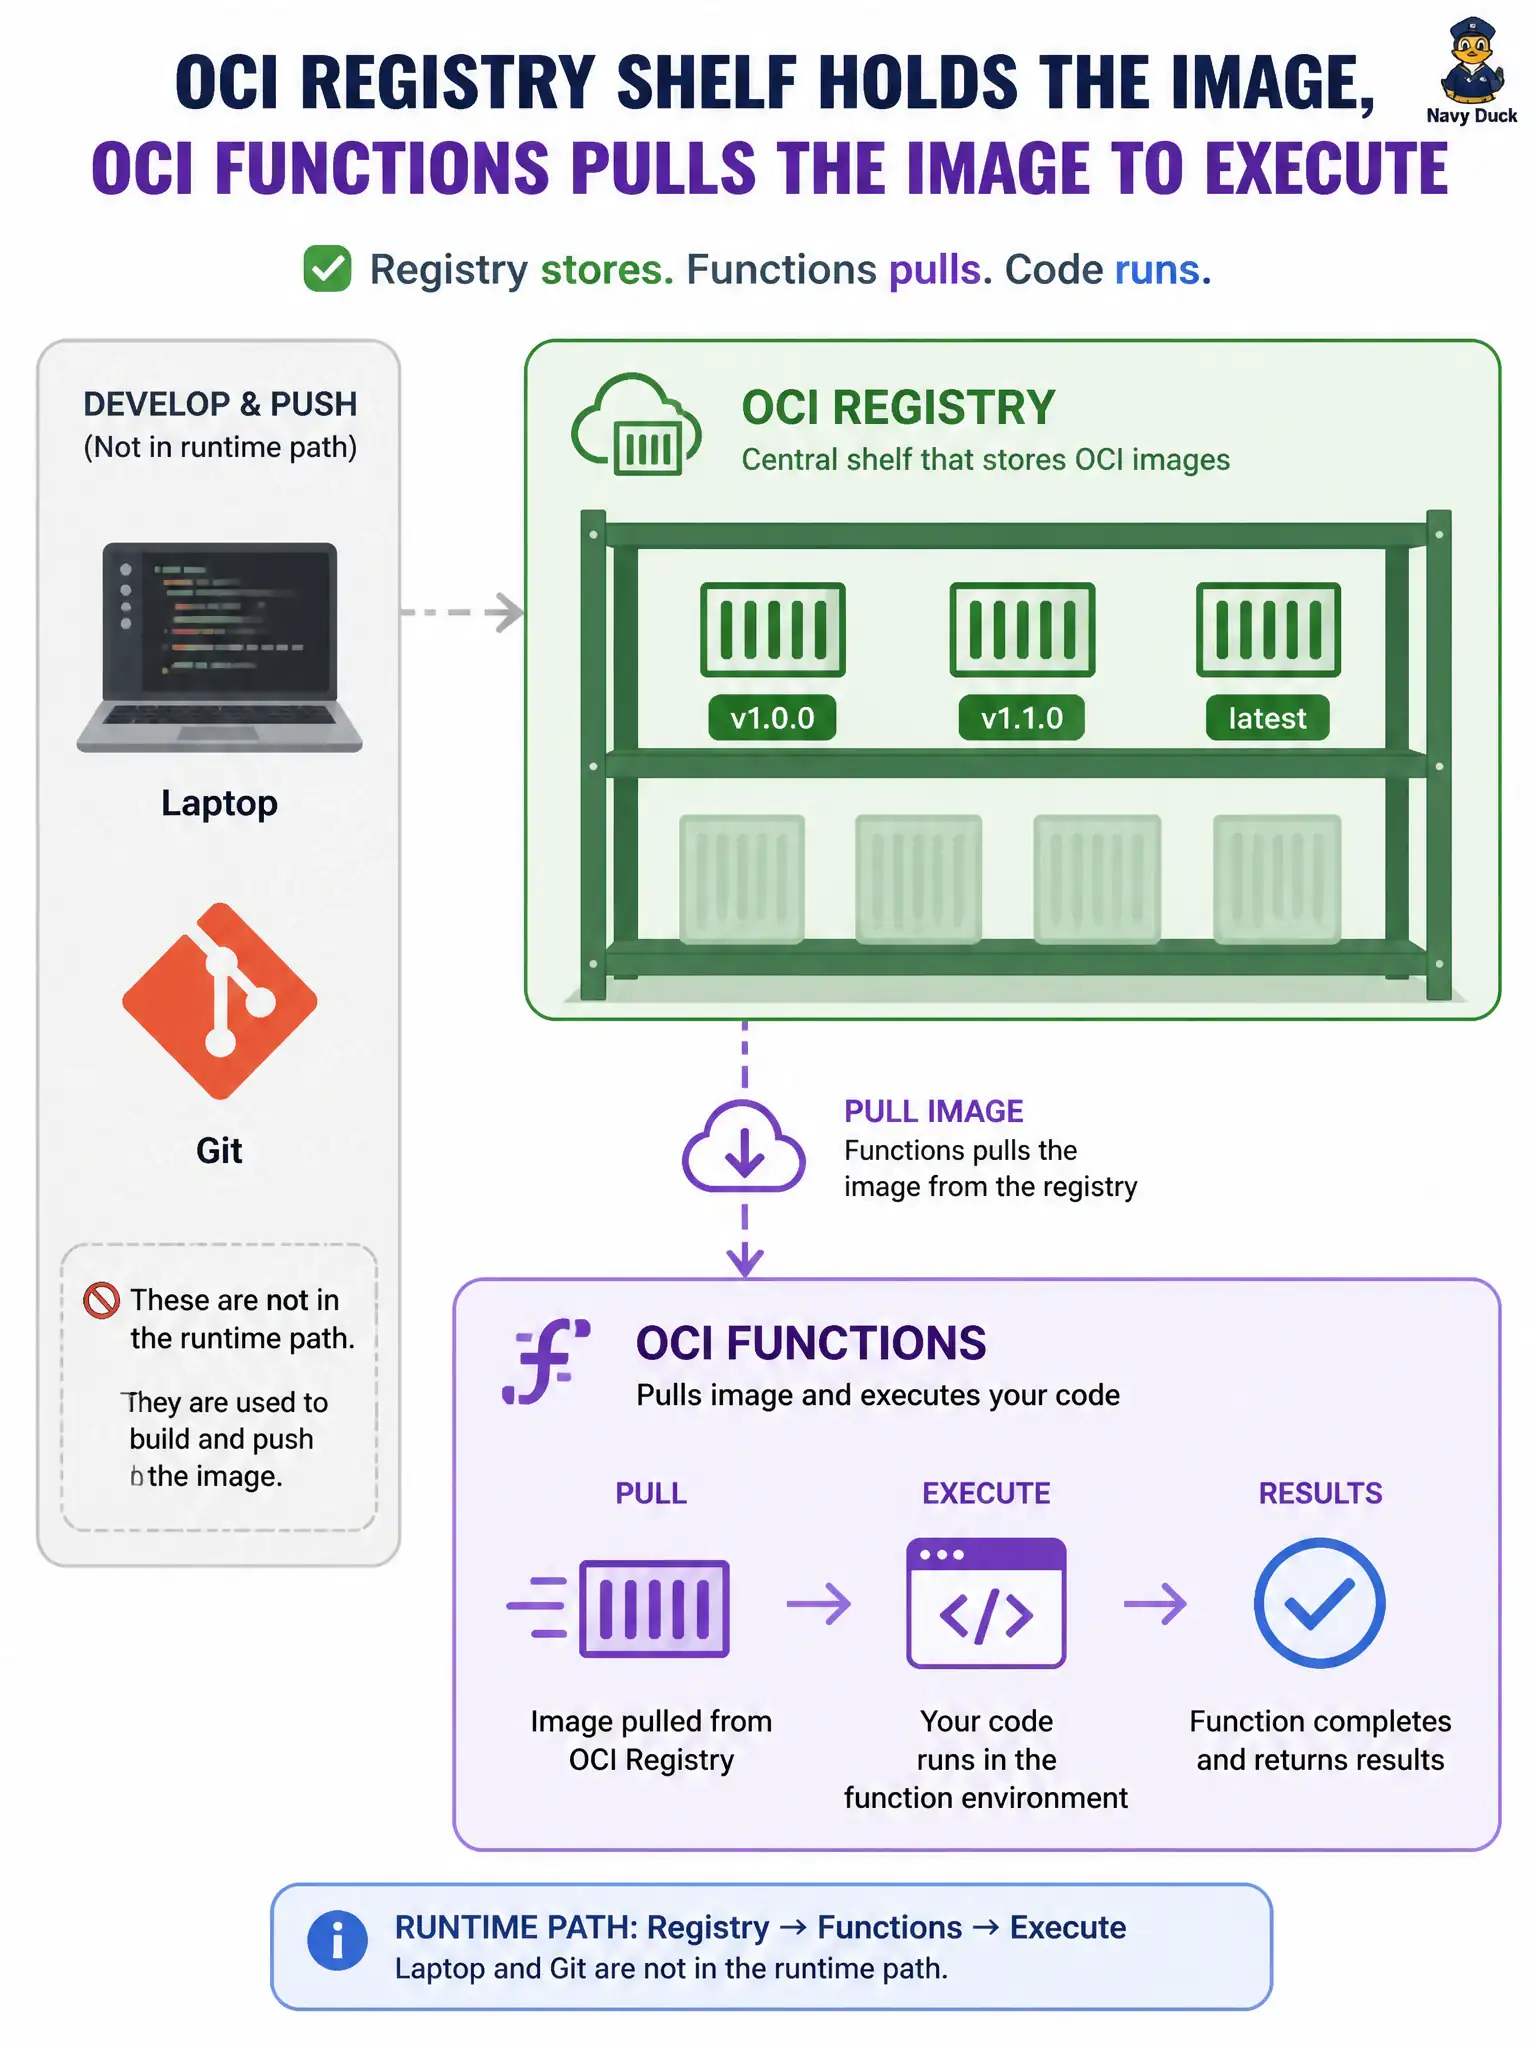
A deployed function is a container image on a shelf; OCI Functions pulls that shelf image from OCIR. Functions consumes the registry—it does not replace it.
Full Explanation
After fn deploy, OCI Functions obtains the container image it runs from Oracle Cloud Infrastructure Registry (OCIR) as configured in the Fn CLI context. A deployed function is a container image on a shelf; Functions pulls that image from the configured Docker registry—in this exam’s framing, OCIR. Functions consumes the registry; it does not replace it with an alternate code store.
Pulling from inline base64 blobs stored in the application shared config fails by concept because shared config is for configuration values, not the function’s container image layers. Cloning a Git repository on every cold start fails because cold start runs a pulled image—it is not a git checkout factory. Fetching from the local developer laptop over SSH each invoke fails because production invokes must not depend on a workstation path; the image must already live in the registry Functions can reach.
Exam caveat: OCIR auth, compartment policy, and private subnet service-gateway reachability still matter—knowing “image comes from OCIR” does not skip registry permissions. Operational check: after deploy, locate the image in OCIR, confirm the function resource references it, invoke, and ensure worker/execution networking can pull without falling back to a laptop.