
OKE worker nodes for a records-management workload run in a private subnet and must pull images from OCIR in the same region without public IPs. Which VCN attachment pattern do official OCIR docs call out for that pull path?
Select an answer to reveal the explanation.
Short Explanation
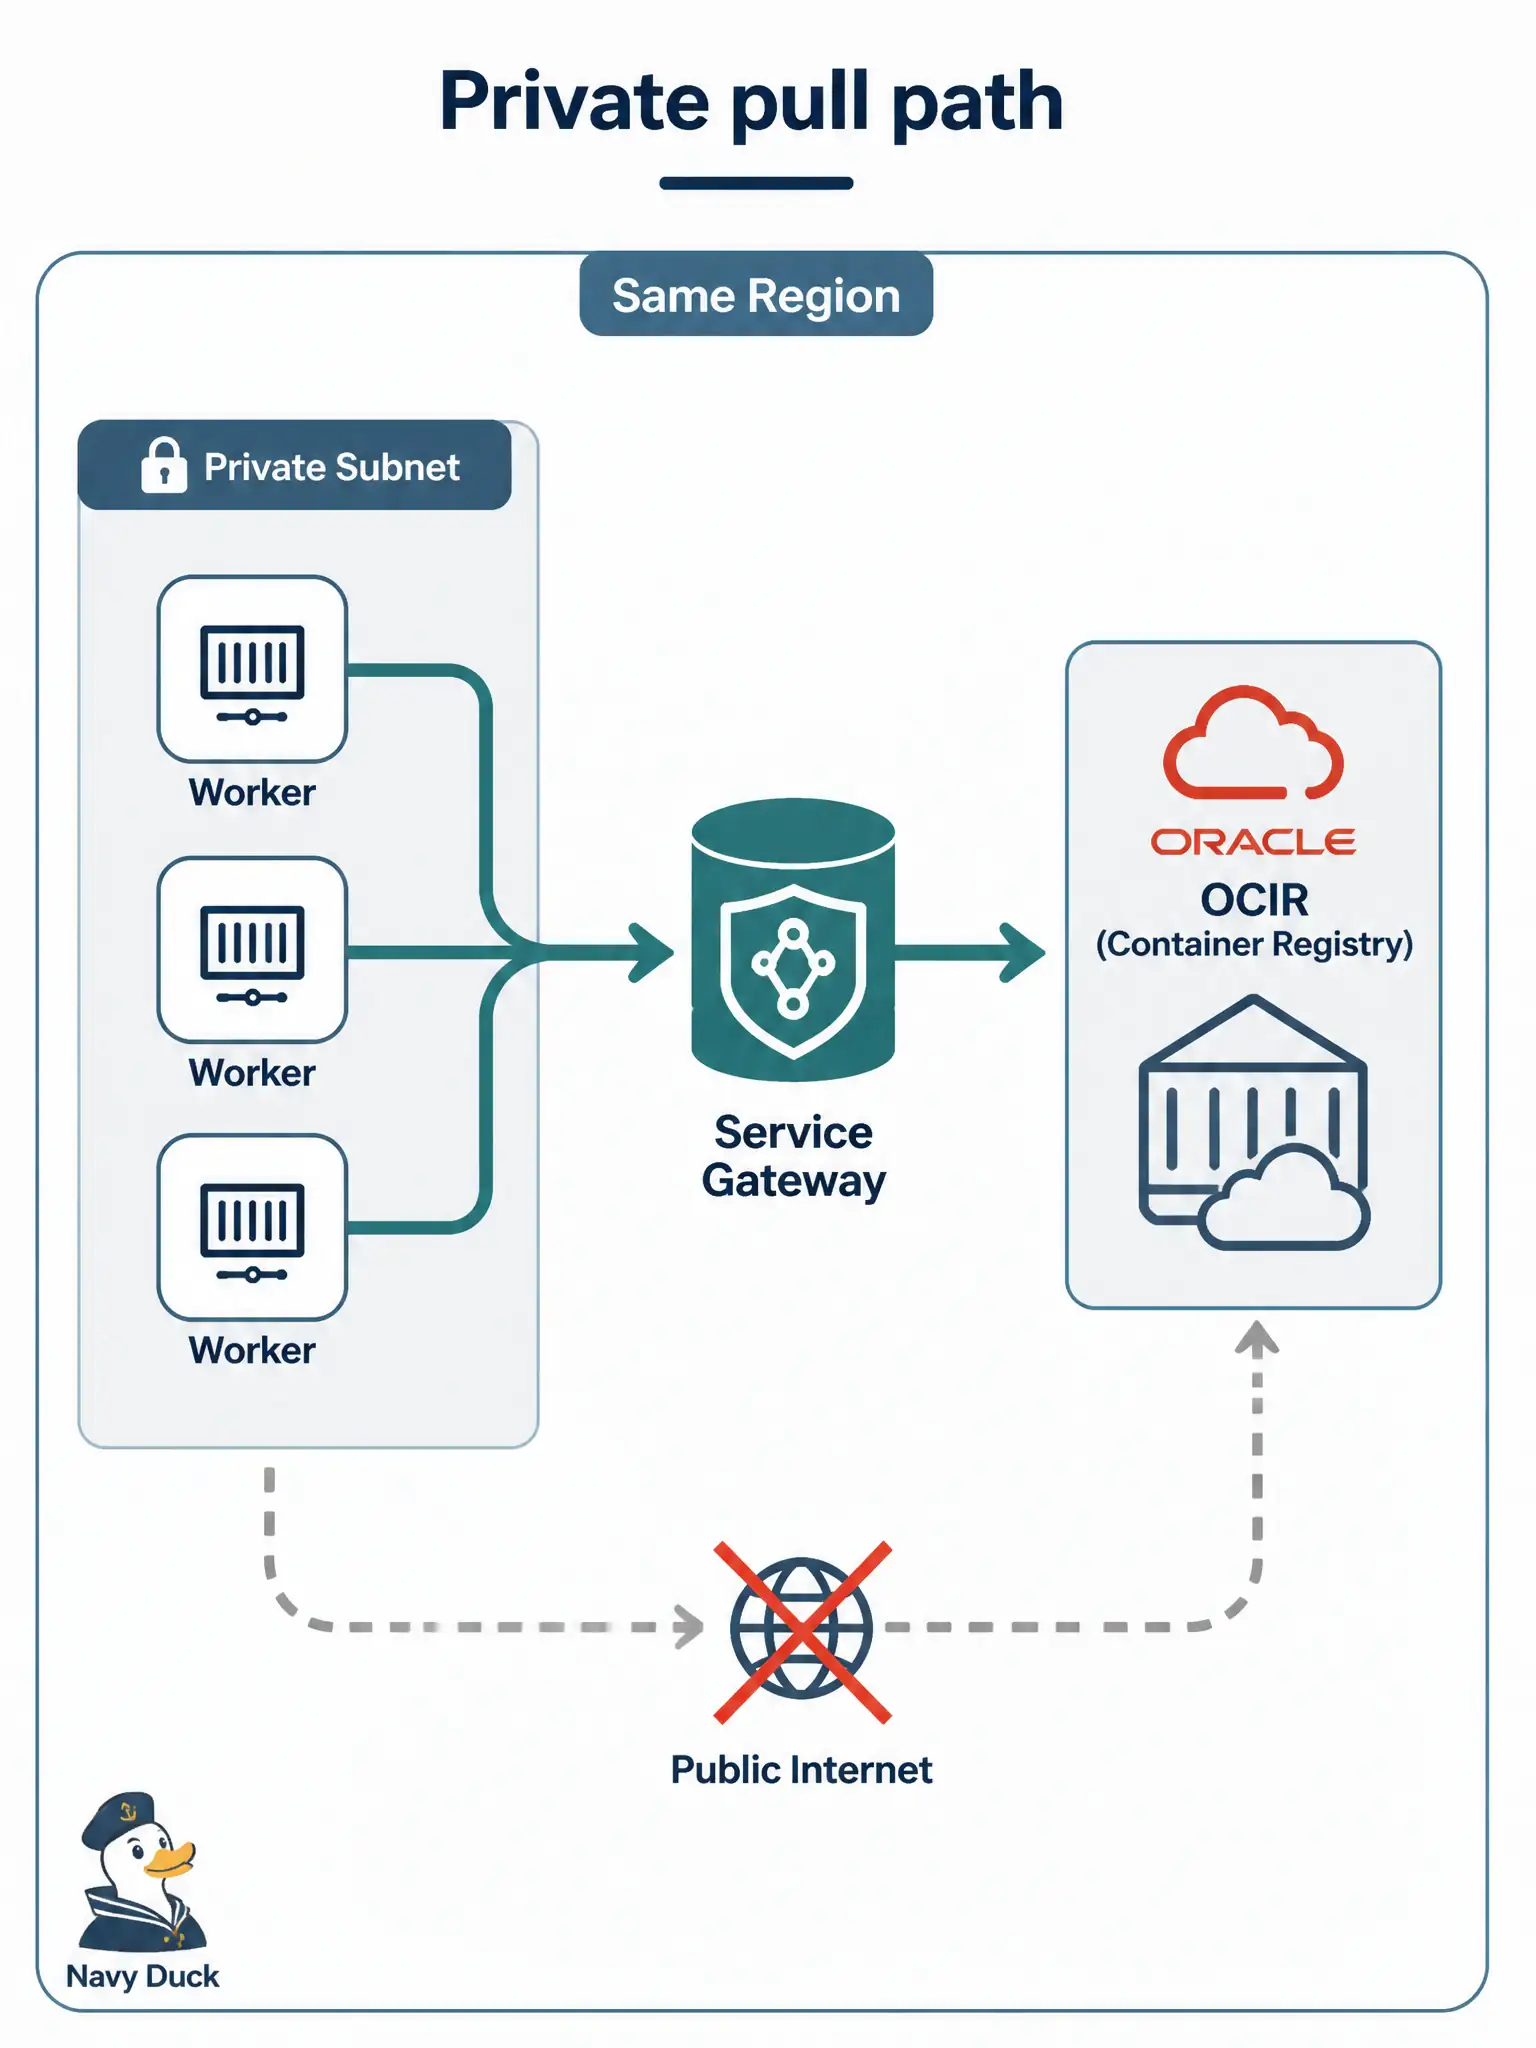
Private subnet workers do not need public IPs to pull same-region OCIR. A service gateway on the VCN is the documented path—app attachment to an existing VCN, not a hub-spoke redesign.
Full Explanation
Official OCIR guidance for private-subnet OKE workers pulling same-region OCIR images calls out a service gateway on the VCN. Workers without public IPs reach OCI services such as OCIR over the service gateway path instead of hairpinning through the public internet. That pattern keeps records-management image pulls private while still using the regional managed registry.
Requiring an internet gateway and public IPs on every worker as the only supported path contradicts the private-subnet service gateway design. Redesigning the entire tenancy into a hub-spoke DR landing zone before any pull is allowed massively overscopes a networking attachment question. Disabling all gateways and relying on docker save/load over SSH from a laptop is a manual workaround, not the documented cluster pull path, and does not scale to node replacement or autoscaling.
Exam caveat: security lists / NSGs and IAM still must allow the pull—service gateway alone does not grant repository permission. Operational check: confirm a service gateway exists and routes OCI services for the workers’ VCN/subnet, pull an OCIR image from a private worker (or test pod), and verify traffic does not depend on a public IP on the node.