
A teammate can pull from a private OCIR repository used by the 311 mobile API but cannot push new tags. What best explains that at developer depth?
Select an answer to reveal the explanation.
Short Explanation
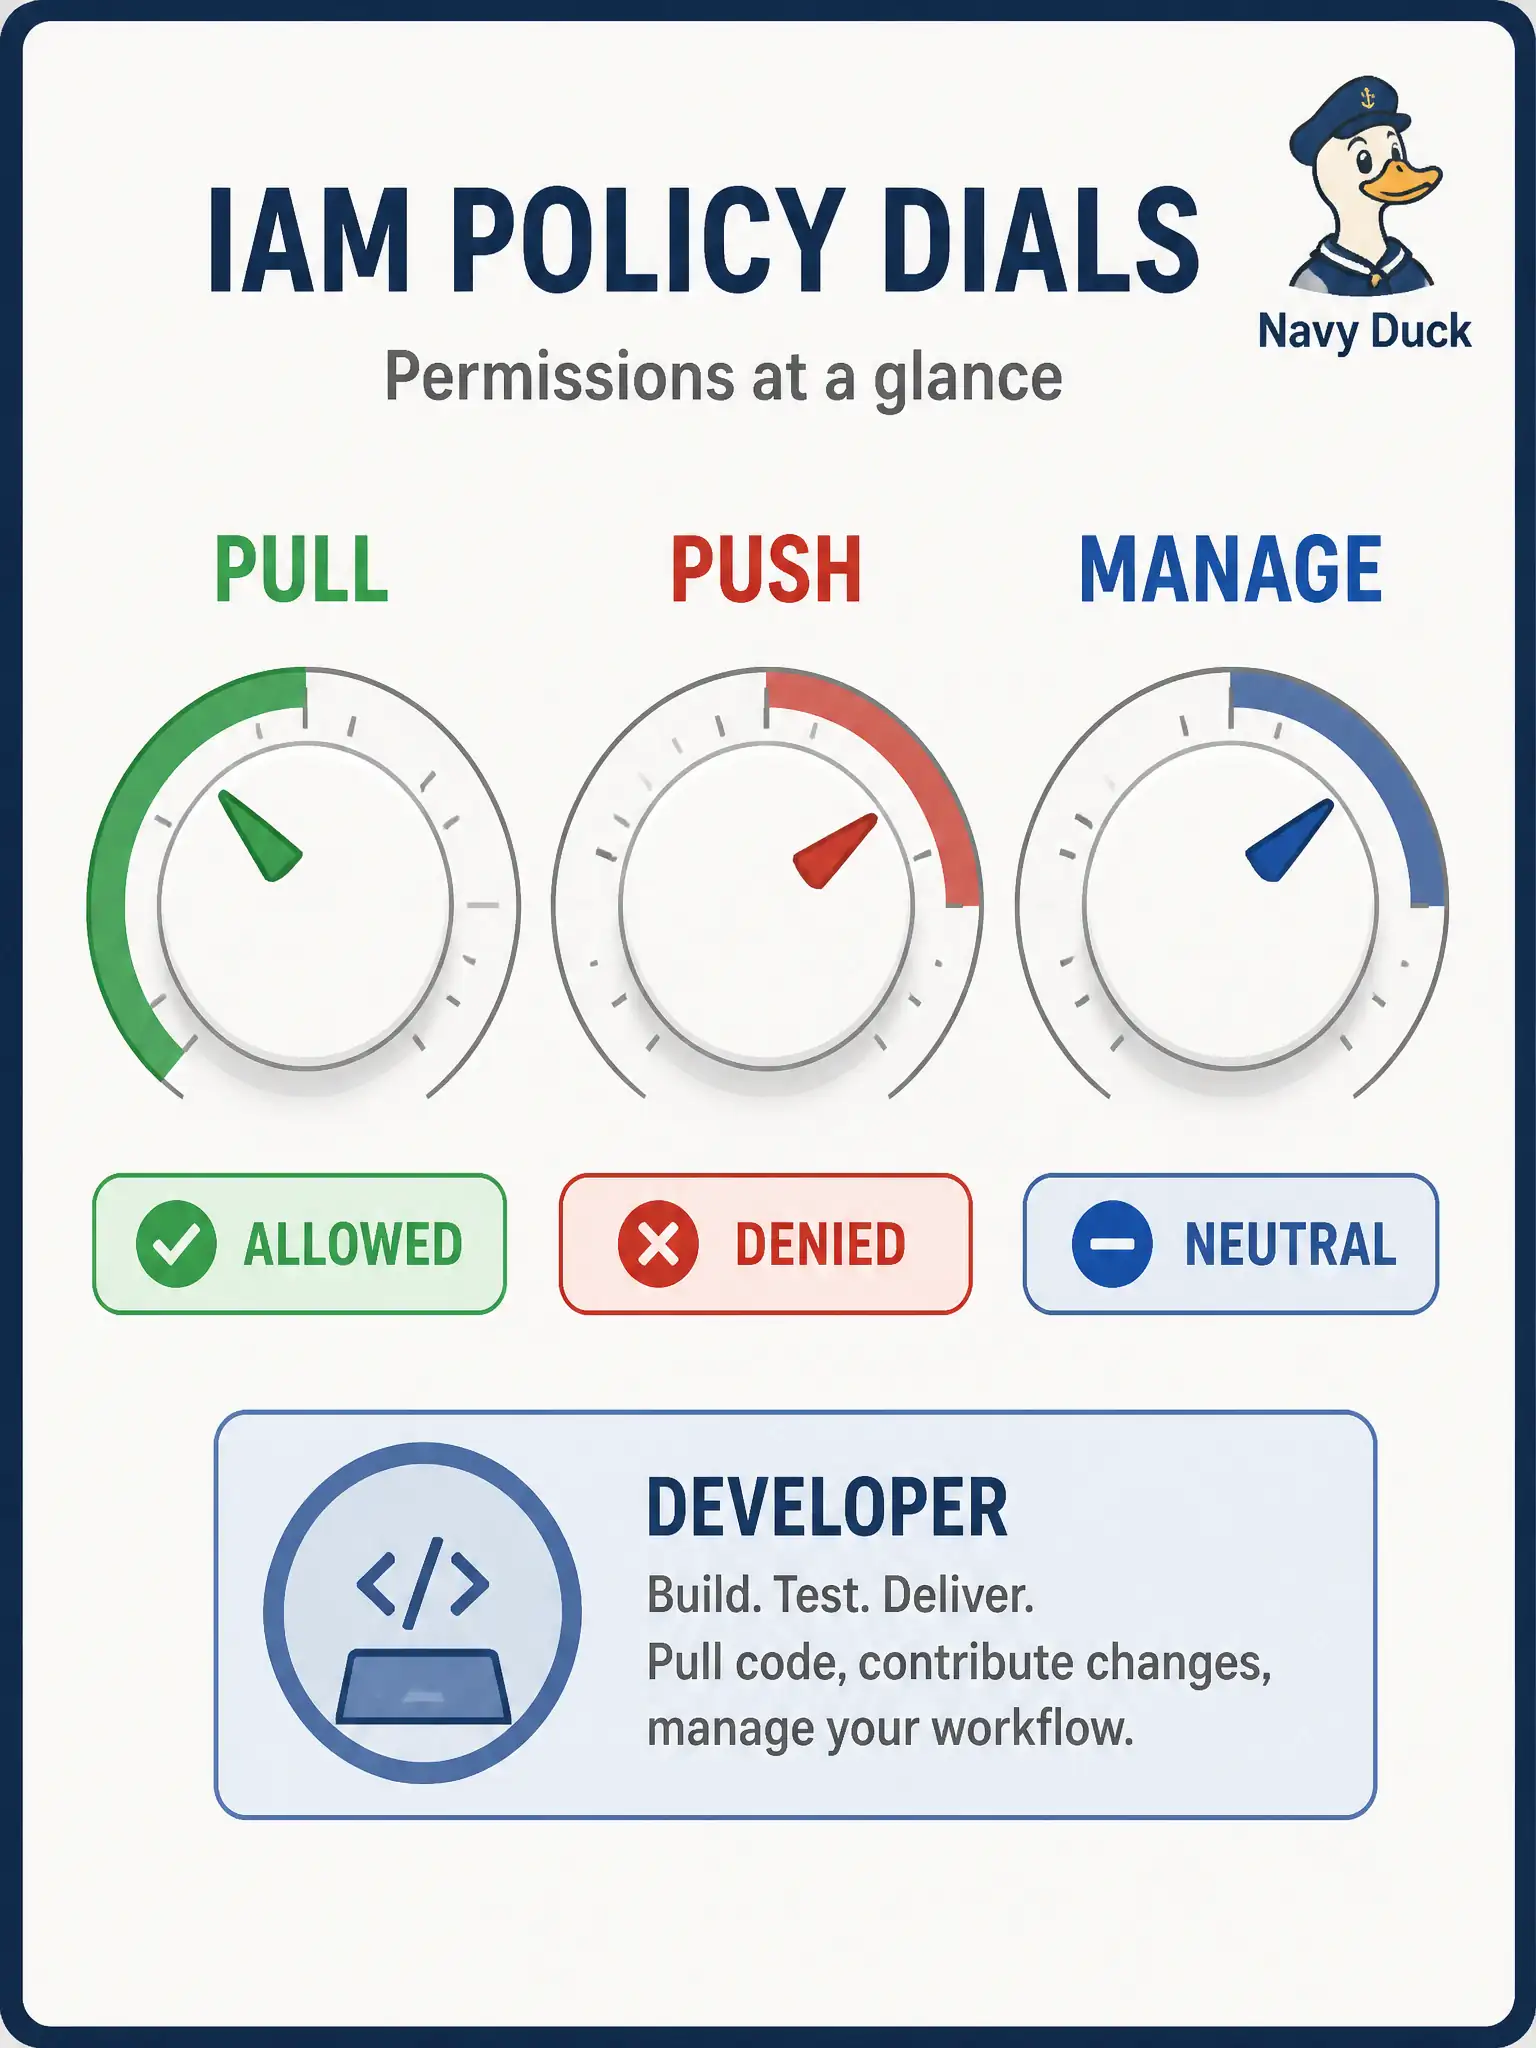
Belonging to Administrators works but is not required. Policies can let you pull without letting you push—teammates still need explicit grants on the compartment’s repositories.
Full Explanation
OCIR authorization is driven by IAM on repository operations in a compartment. Create, push, pull, and manage are separately controllable. A teammate can therefore hold enough policy to pull from the private repository used by the 311 mobile API without holding push (or manage) rights. That least-privilege split is intentional: readers and runtime pullers should not automatically become publishers of new tags.
Anyone who can pull is not automatically an Administrators group member with full push rights—Administrators is a blunt path, not the only or recommended one. Private repositories do not ignore IAM and allow every tenancy user to push; privacy restricts anonymous access while IAM still gates authenticated actions. Push rights are not conferred merely by owning a Compute instance in the same availability domain; compute locality is unrelated to OCIR IAM verbs.
Exam caveat: OKE pull and human docker pull may use different principals—fix both when diagnosing “cluster works but developer cannot push.” Operational check: inspect the IAM policies on the repository’s compartment for the teammate’s group, confirm pull-related verbs without push, attempt docker pull (success) and docker push (expected deny), then grant push only if their role requires publishing.