
A developer with rights only in a non-root compartment is ready to push the first tag of sanitation-routing. What should they do before the first docker push?
Select an answer to reveal the explanation.
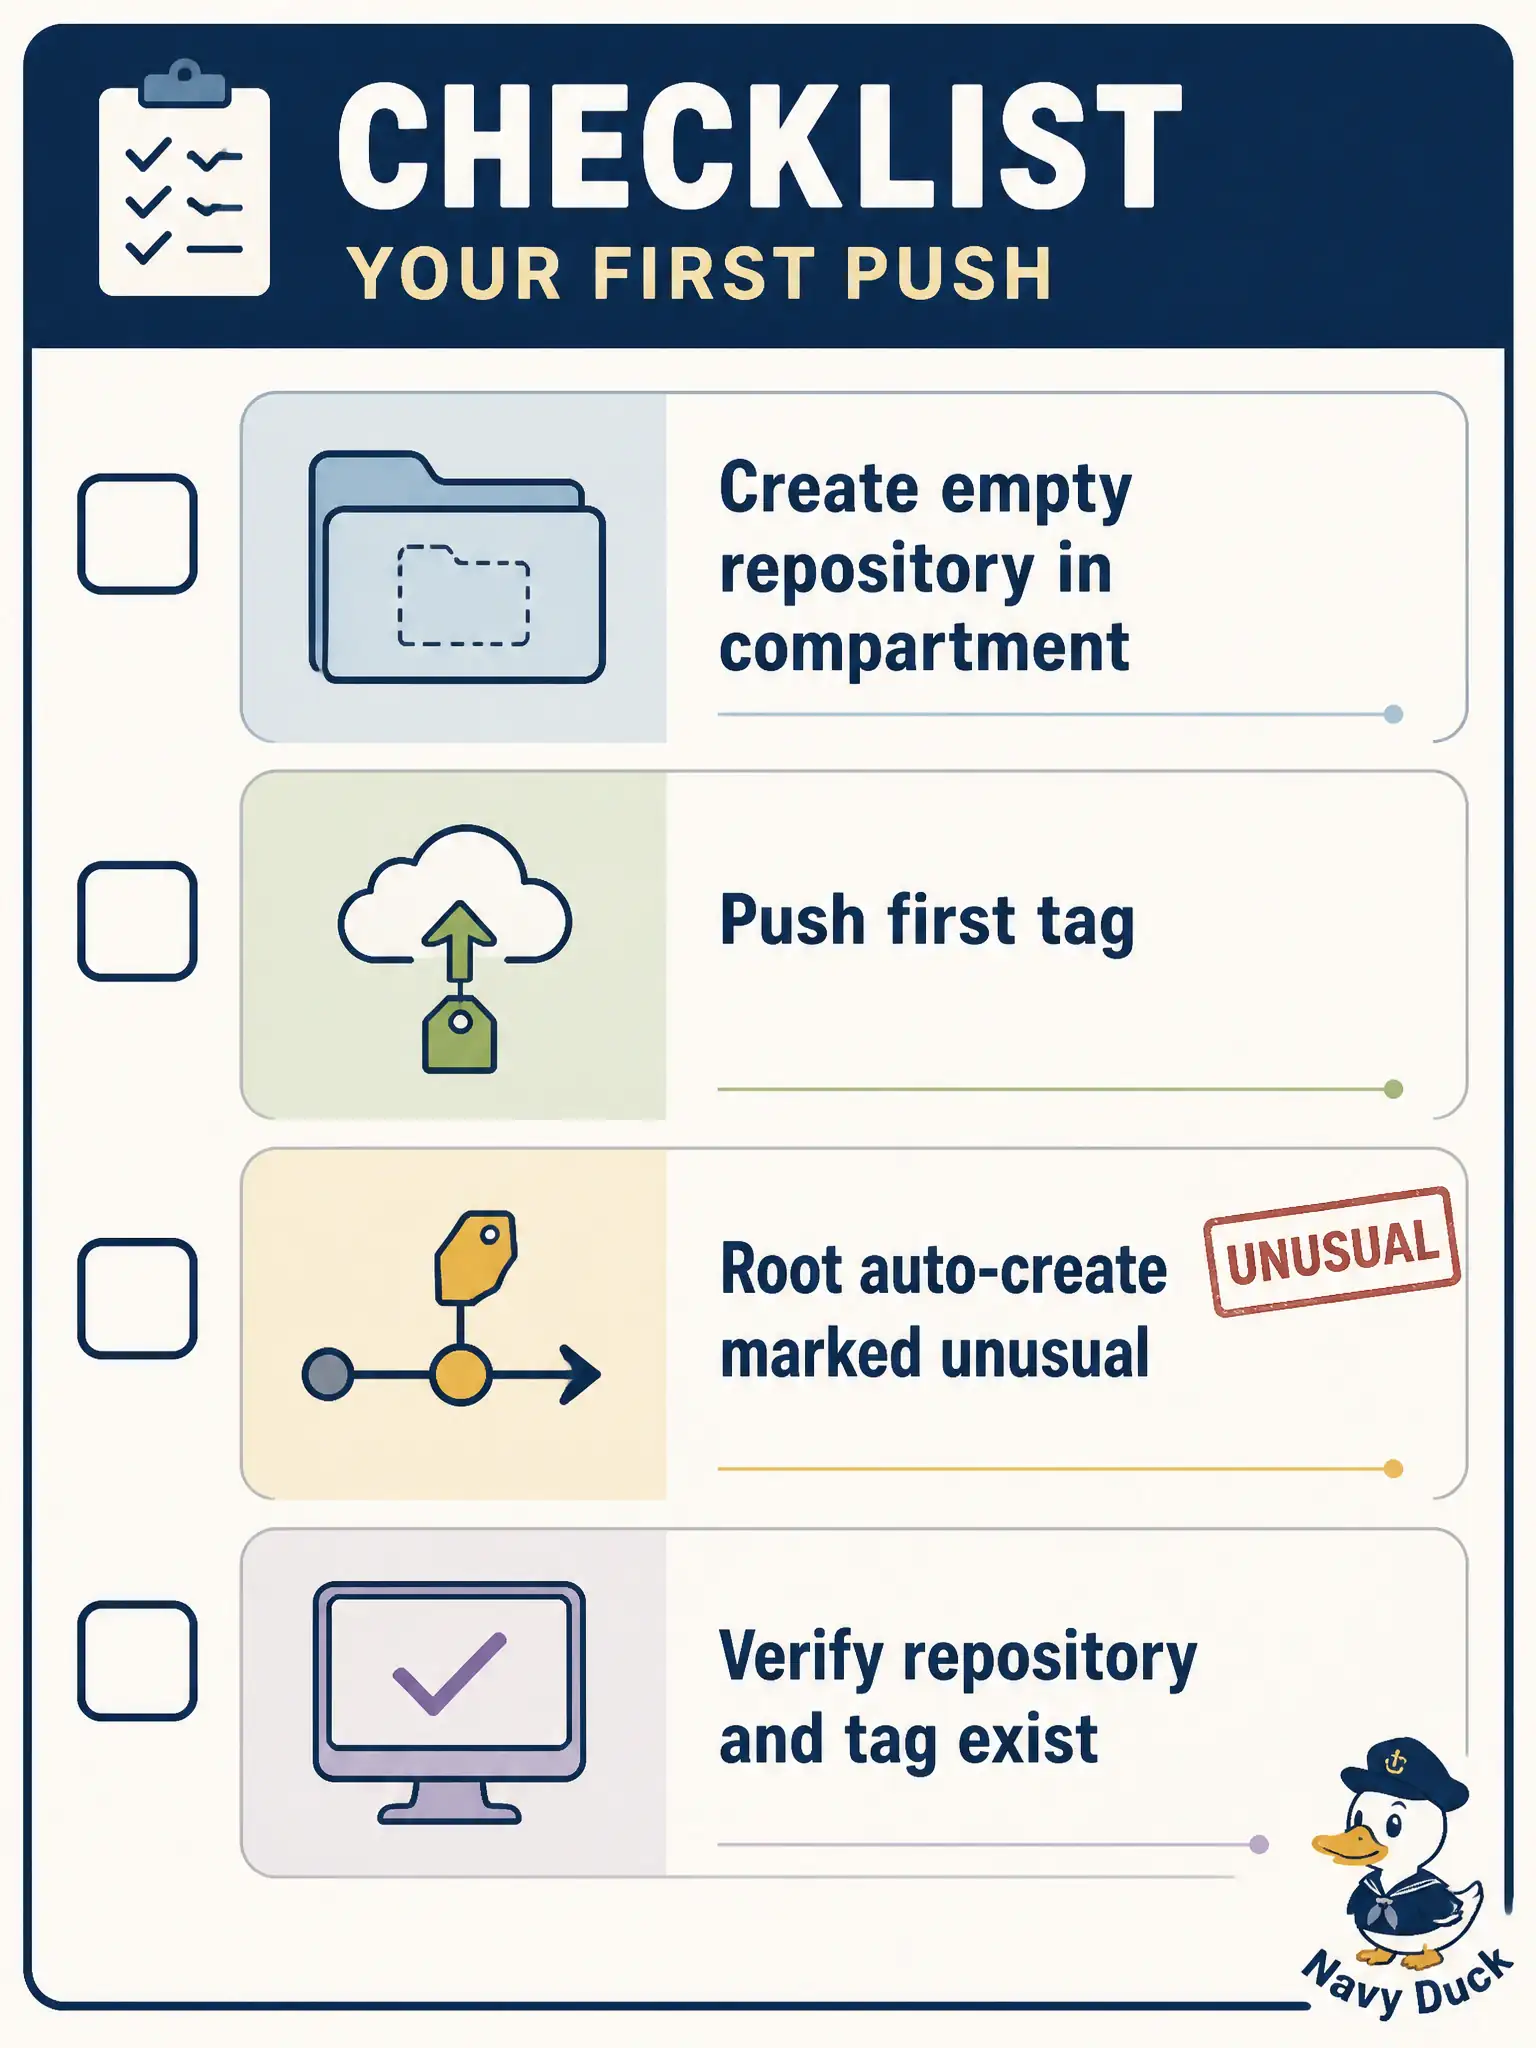
Short Explanation
Normal workflow: create the empty repository in the compartment, then push. If you only manage repos outside root, you must create first—root auto-create is the unusual case.
Full Explanation
Before the first docker push of sanitation-routing, a developer who only has rights in a non-root compartment should create the empty repository in that target compartment first, then push images whose path includes that repository name. Repository creation places the OCIR resource under the correct compartment for IAM and tenancy organization. Relying on implicit creation only where policies allow (often root-oriented auto-create behaviors) fails when the user cannot create in root and the repo does not yet exist where they do have rights.
Assuming root-compartment auto-create always invents the repository from the tag path is unsafe when the developer lacks root rights or when policy disables that behavior. Pushing a tarball to Object Storage and renaming it .tar does not register an OCIR repository or publish a distribution manifest. Skipping repository creation because “Docker invents OCI repositories from the laptop hostname” invents a behavior that does not exist.
Exam caveat: the repository name in the image path must match the repository you created; path typos create confusion with “not found” errors versus IAM denials. Operational check: create the empty repository in the sanitation compartment in the Console (or CLI), confirm IAM allows push for the developer’s group on that compartment, then push the first tag and verify it lands under that repository.