
A planning-department repository in OCIR must be pullable only by callers with IAM permission or a logged-in Docker session. Which repository setting matches that requirement?
Select an answer to reveal the explanation.
Short Explanation
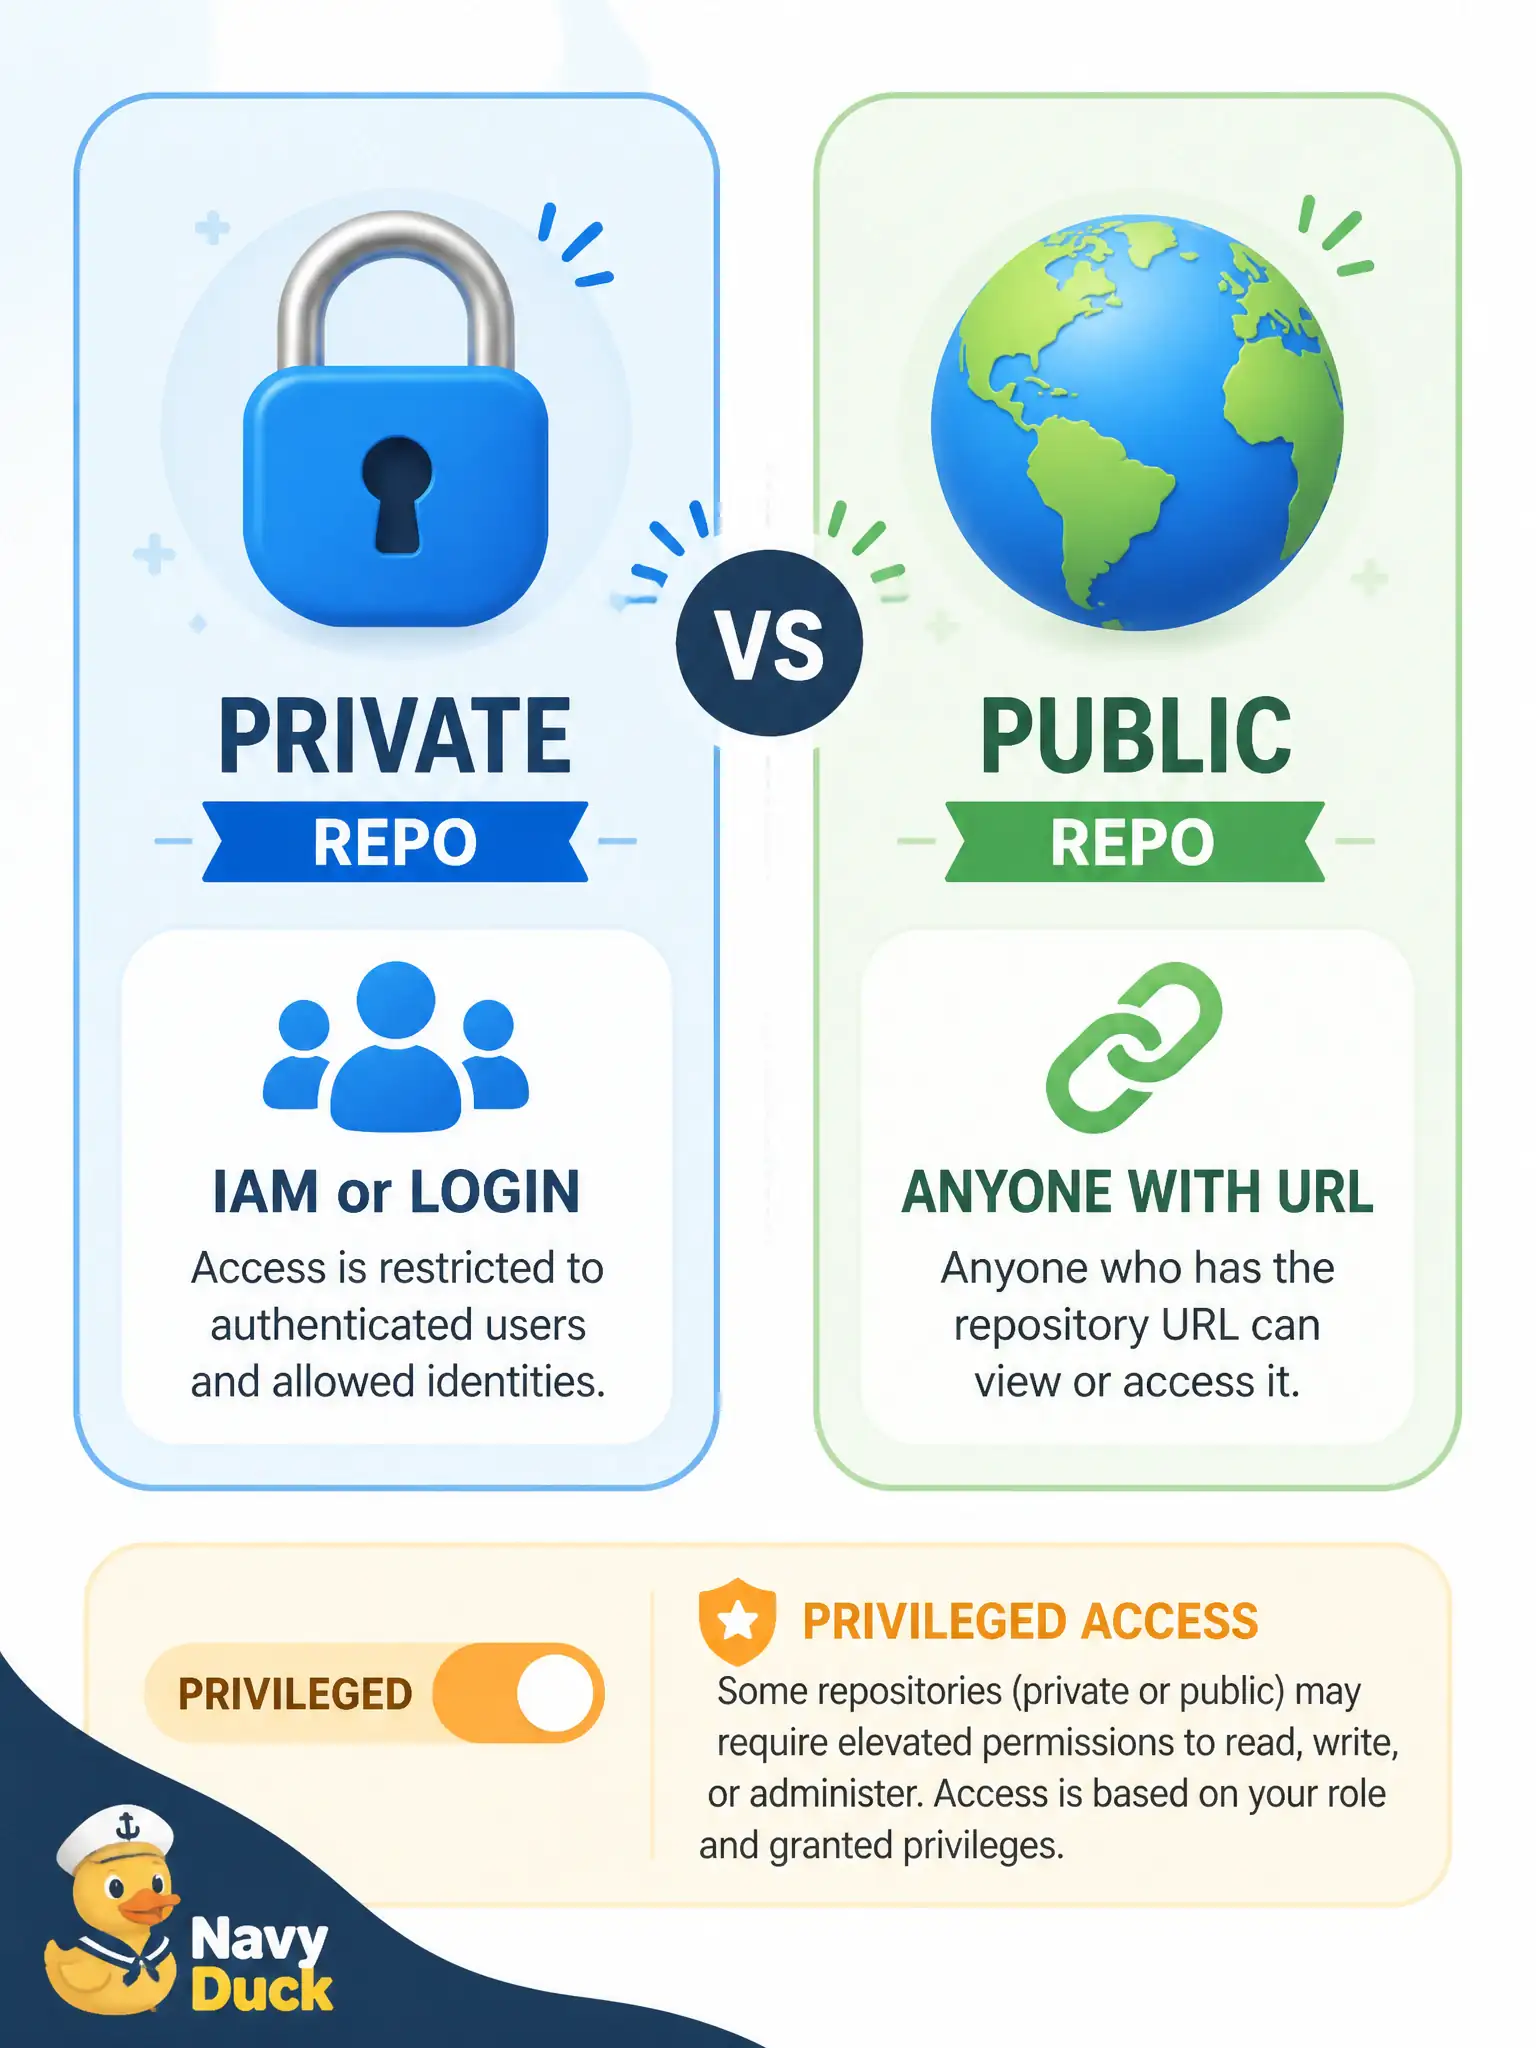
Private needs IAM or a logged-in pull. Public can be pulled by anyone who knows the URL—and making a repo public is a privileged manage operation, not “OCIR has no auth.”
Full Explanation
A private OCIR repository matches the planning-department requirement: pulls require IAM permission or an authenticated Docker session. Callers without authorization cannot anonymously fetch the image just because they know the URL. Public repositories, by contrast, are readable by anyone who can reach the URL; making a repository public is a privileged action because it widens exposure of the artifact.
Choosing public because “public means OCIR disables all authentication tenancy-wide” misstates the feature—public is a per-repository readability setting, not a tenancy-wide auth kill switch. Granting REPOSITORY_MANAGE to anonymous internet users by default is not how public repos work and would be grossly over-privileged. Claiming neither private nor public exists and that every OCIR repository is world-readable is false; privacy is a first-class repository setting.
Exam caveat: private repos still need correct IAM for CI push and for OKE pull (instance principal or imagePullSecrets patterns)—privacy alone does not grant access. Operational check: with the repository set to private, attempt an unauthenticated pull and confirm it fails; then pull with a principal that has pull rights and confirm success, proving the setting matches the intended control.