
A municipal GIS team needs the Oracle-managed place to store, share, and retrieve container images with the ordinary Docker CLI. Which OCI service should they use?
Select an answer to reveal the explanation.
Short Explanation
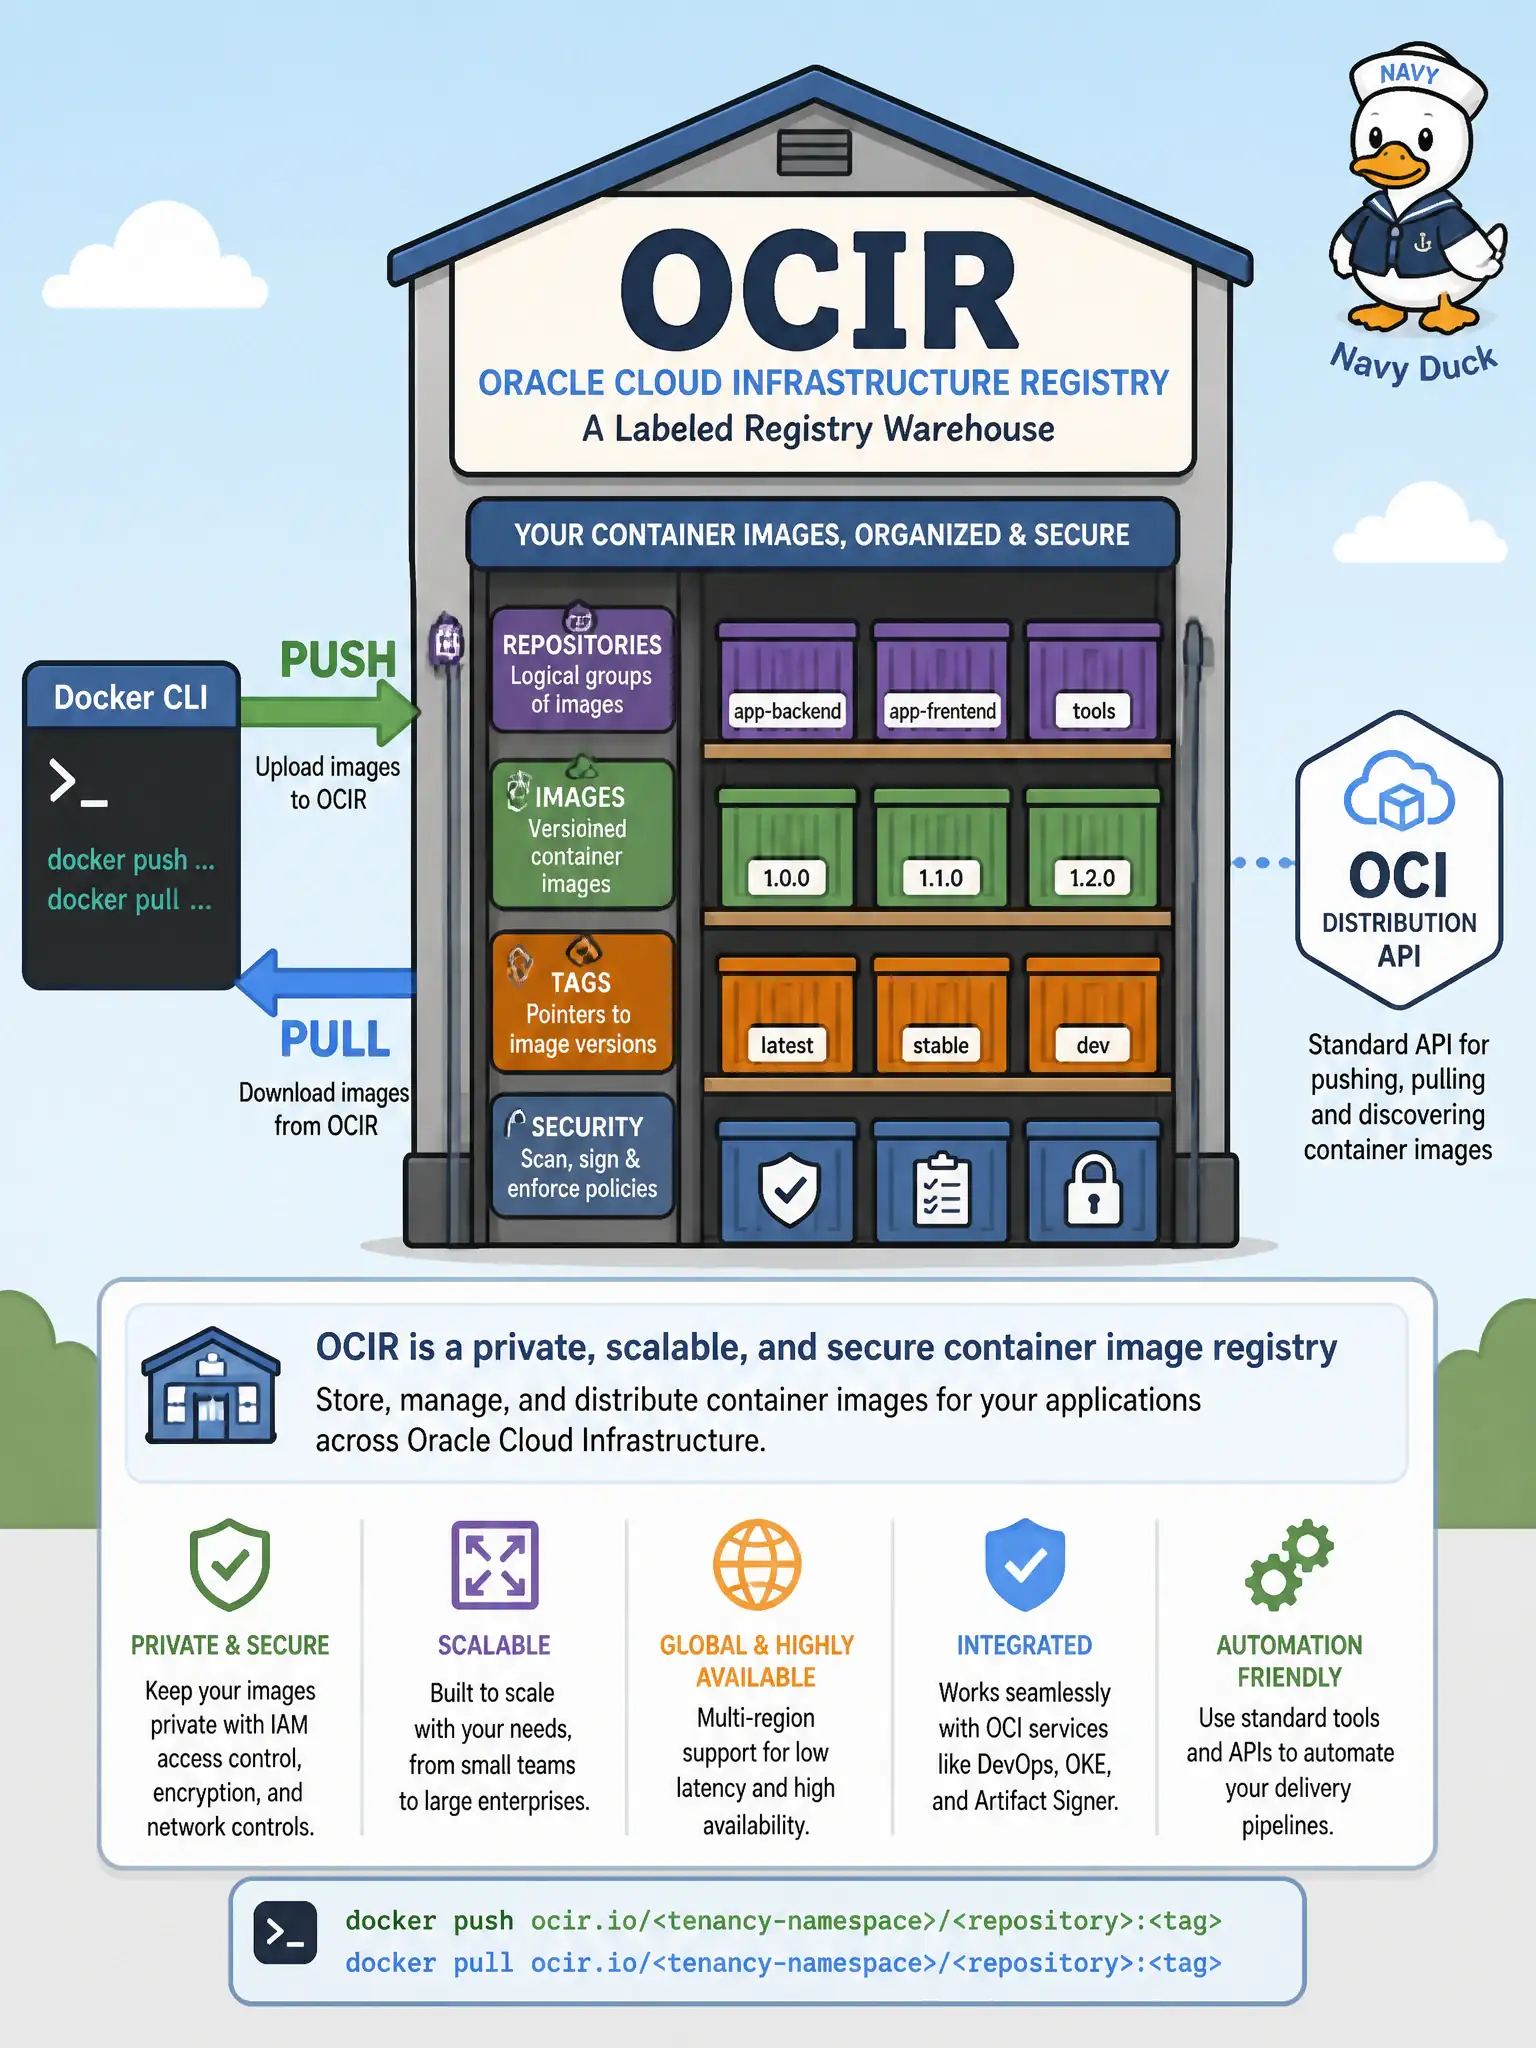
OCIR is OCI’s managed, OCI-compliant container registry—the Docker CLI’s home for push and pull. Object Storage with a sticker is not a registry.
Full Explanation
Oracle Cloud Infrastructure Registry (OCIR / Container Registry) is the Oracle-managed service that speaks the Docker V2 and OCI distribution API. The municipal GIS team can use the ordinary Docker CLI—docker login, tag, push, and pull—against the regional OCIR endpoint to store, share, and retrieve container images. That makes OCIR the natural home for CI-built images and for OKE (or other runtimes) that pull by standard registry path, without inventing a custom storage protocol.
Object Storage with a public bucket renamed to “look like” a registry is not a Docker-compatible distribution endpoint; clients expect manifests, blobs, and auth flows that a raw bucket does not provide. Claiming containers can only use Compute custom images on OCI confuses VM custom images with container image distribution—OKE and Docker Engine pull from registries, not from Compute image catalogs. Insisting a third-party registry outside OCI is the only supported option for OKE pulls is false: OKE routinely pulls from OCIR in the same tenancy and region when IAM and network path are configured correctly.
Exam caveat: OCIR is regional—choose the registry domain that matches the region where you store and pull the GIS images. Operational check: from a workstation or CI runner with an auth token, docker login to the regional host, push a small test image under the tenancy namespace, then docker pull the same fully qualified name and confirm the digest matches.