
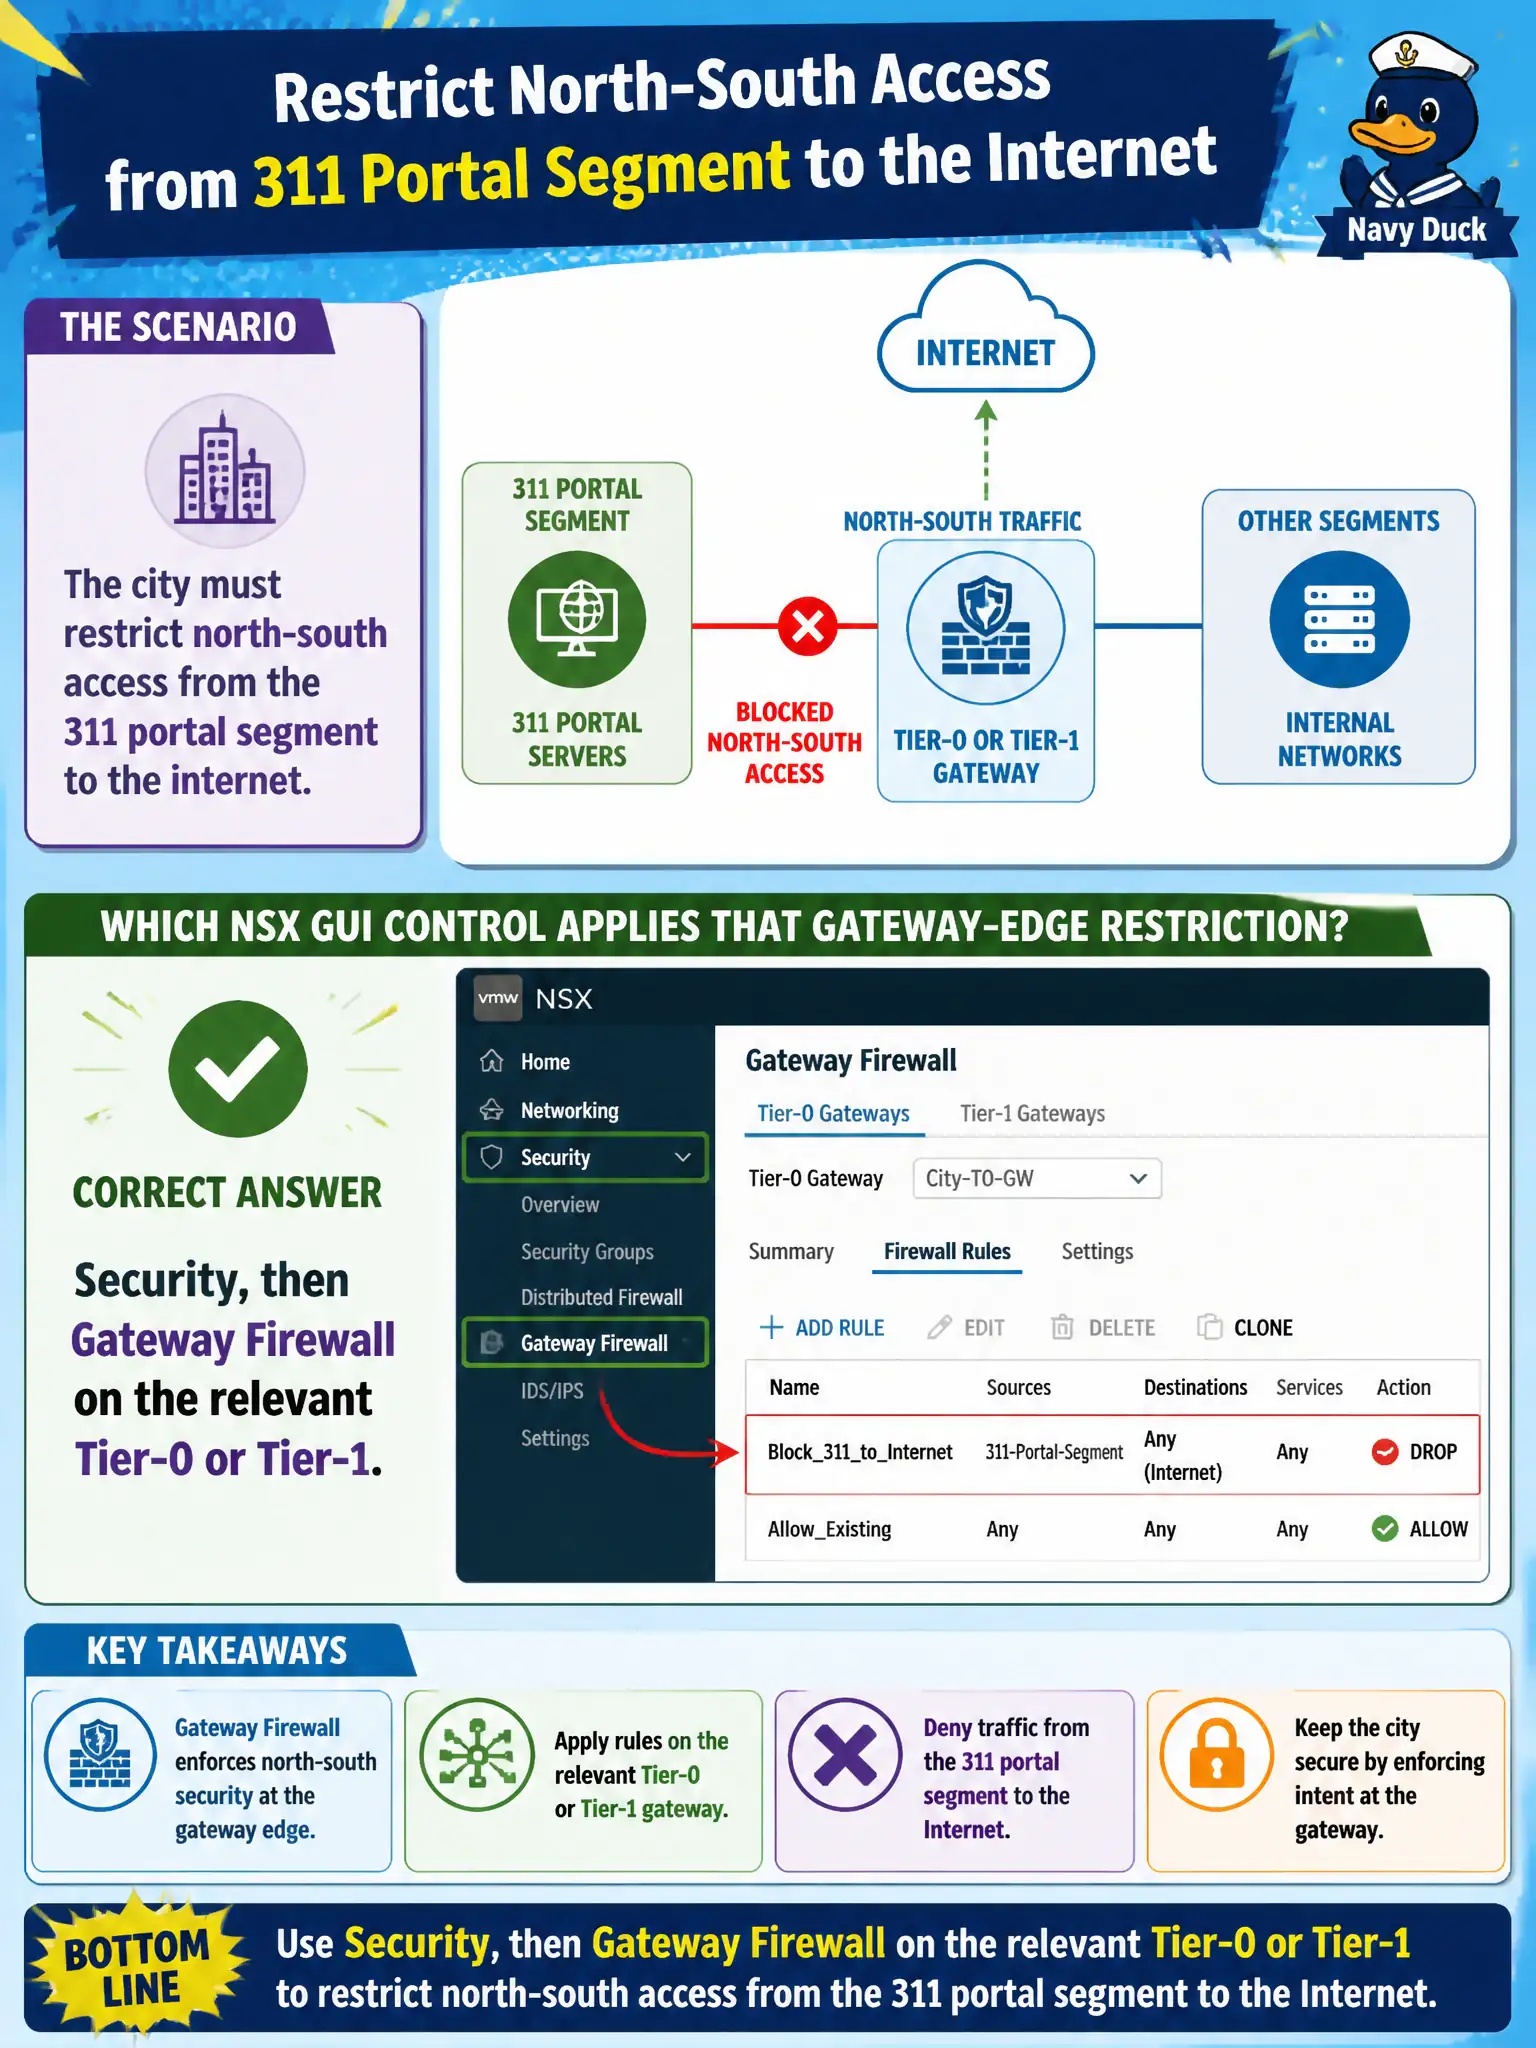
The city must restrict north-south access from the 311 portal segment to the internet. Which NSX GUI control applies that gateway-edge restriction?
Select an answer to reveal the explanation.
Short Explanation
311 talking to the internet is street traffic leaving city hall, not hallway talk between two cubicles. That edge filter is Gateway Firewall on the T0 or T1. DFW-only, Horizon Blast, and vSAN iSCSI are not that gate.
Full Explanation
North-south traffic that enters or leaves the overlay through an Edge is controlled by Gateway Firewall, configured under Security, then Gateway Firewall on the relevant Tier-0 or Tier-1. 311 talking to the internet is street traffic leaving city hall, not hallway talk between two cubicles—that edge filter is Gateway Firewall. Distributed Firewall is the east-west vNIC firewall and is not the GUI for this gateway-edge goal alone. Unified Access Gateway Blast policies are EUC display-protocol controls. vSAN iSCSI bindings do not implement NSX north-south filtering. Exam caveat: designs often combine DFW and gateway firewall; when the requirement is restrict north-south at the gateway edge, name Gateway Firewall. Operational check: create a gateway firewall rule on the Tier-0 or Tier-1 fronting 311, test internet access controls, and reject DFW-only, Horizon Blast, and vSAN iSCSI as the north-south control. Document the civic rationale in the change record so the next operator can restate why the correct control matches the agency outcome, why each distractor fails by concept, and which NSX Manager view confirms the result after publish. Document the civic rationale in the change record so the next operator can restate why the correct control matches the agency outcome, why each distractor fails by concept, and which NSX Manager view confirms the result after publish.