
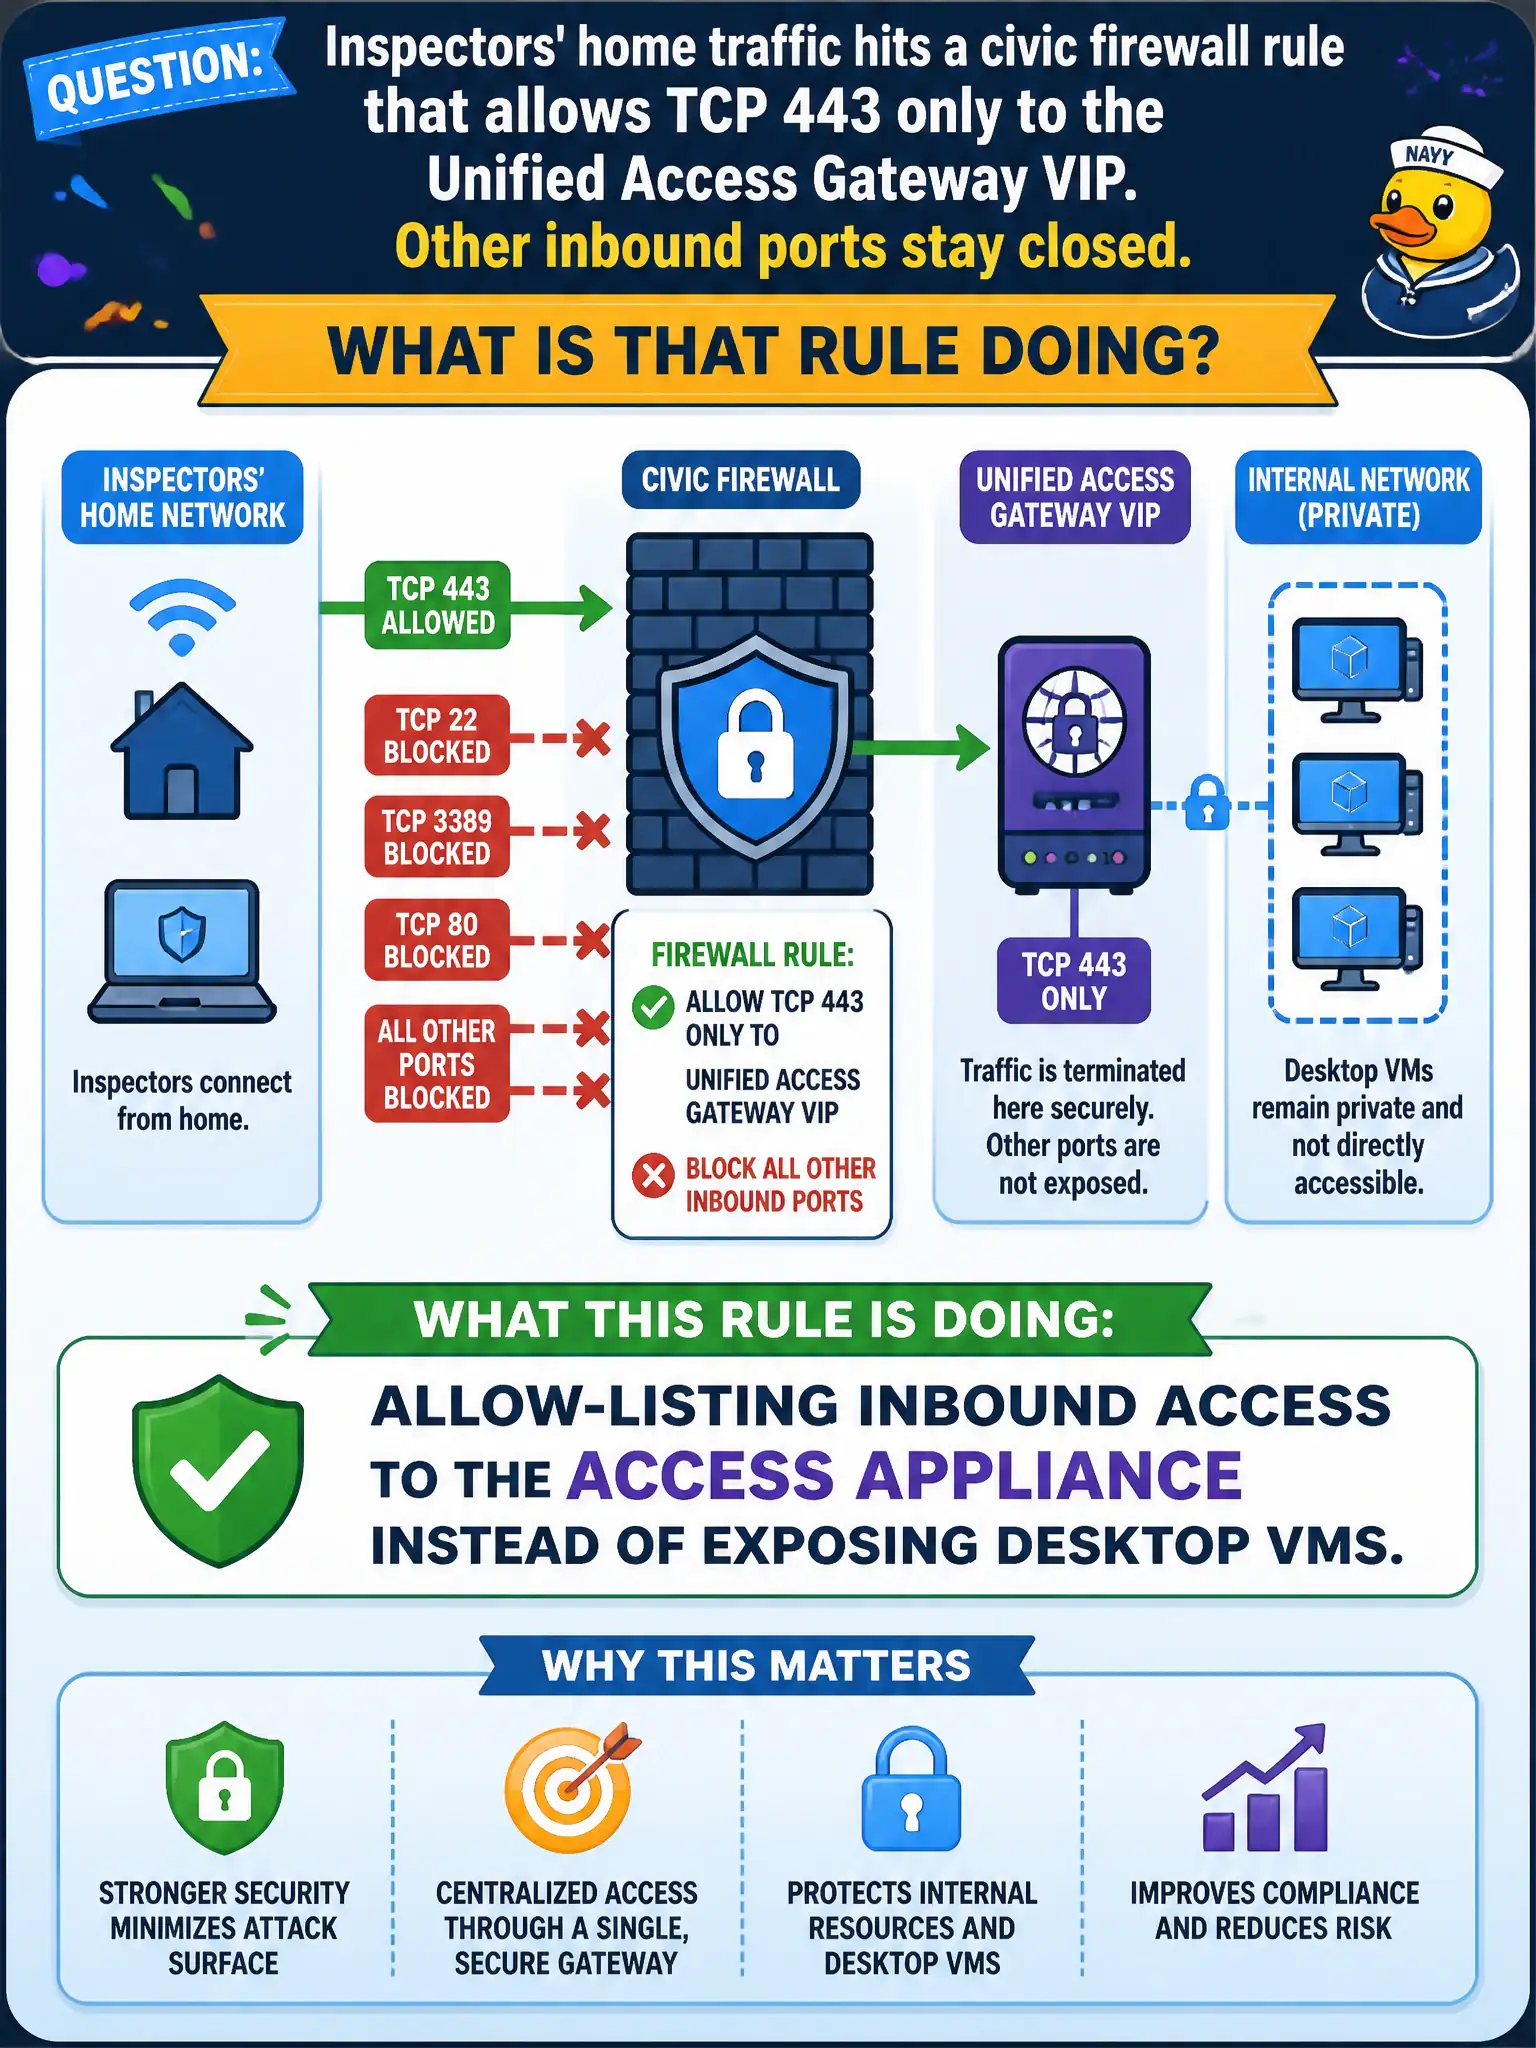
Inspectors' home traffic hits a civic firewall rule that allows TCP 443 only to the Unified Access Gateway VIP. Other inbound ports stay closed. What is that rule doing?
Select an answer to reveal the explanation.
Short Explanation
The firewall is a locked service window: 443 to the UAG address, nothing else inbound. Inspectors do not get raw RDP to desktop VMs. That allow-list is basic civic firewalling, not a vCenter publish.
Full Explanation
A firewall rule allowing TCP 443 only to the UAG VIP allow-lists inbound access to the access appliance instead of exposing desktop VMs. In municipal EUC terms, treat the endpoint as a window into city systems when the architecture says so, not as the system of record for the files or apps in the stem. Distractor concept: Opening RDP from the internet to every desktop VM is the anti-pattern. Distractor concept: The rule does not replace TLS with an unencrypted Horizon Client path. Distractor concept: Publishing vCenter on 443 to the internet is not the inspector access design. Exam caveat: Inbound allow-list to UAG only—never raw desktop RDP or public vCenter. Operational check: Review firewall hits to the UAG VIP on 443 and confirm no direct inbound to desktop VM management/RDP ports. Record the chosen control and the rejected failure modes in the civic change ticket or runbook so on-call staff and auditors share the same rationale after the next maintenance window. Re-validate after personnel or image changes that the same control still meets the city's continuity, security, and support expectations for this service. Helpdesk coaching tip aligned to the conversational brief: The firewall is a locked service window: 443 to the UAG address, nothing else inbound. Inspectors do not get raw RDP to desktop VMs. That allow-list is basic civic firewalling, not a vCenter publish.