
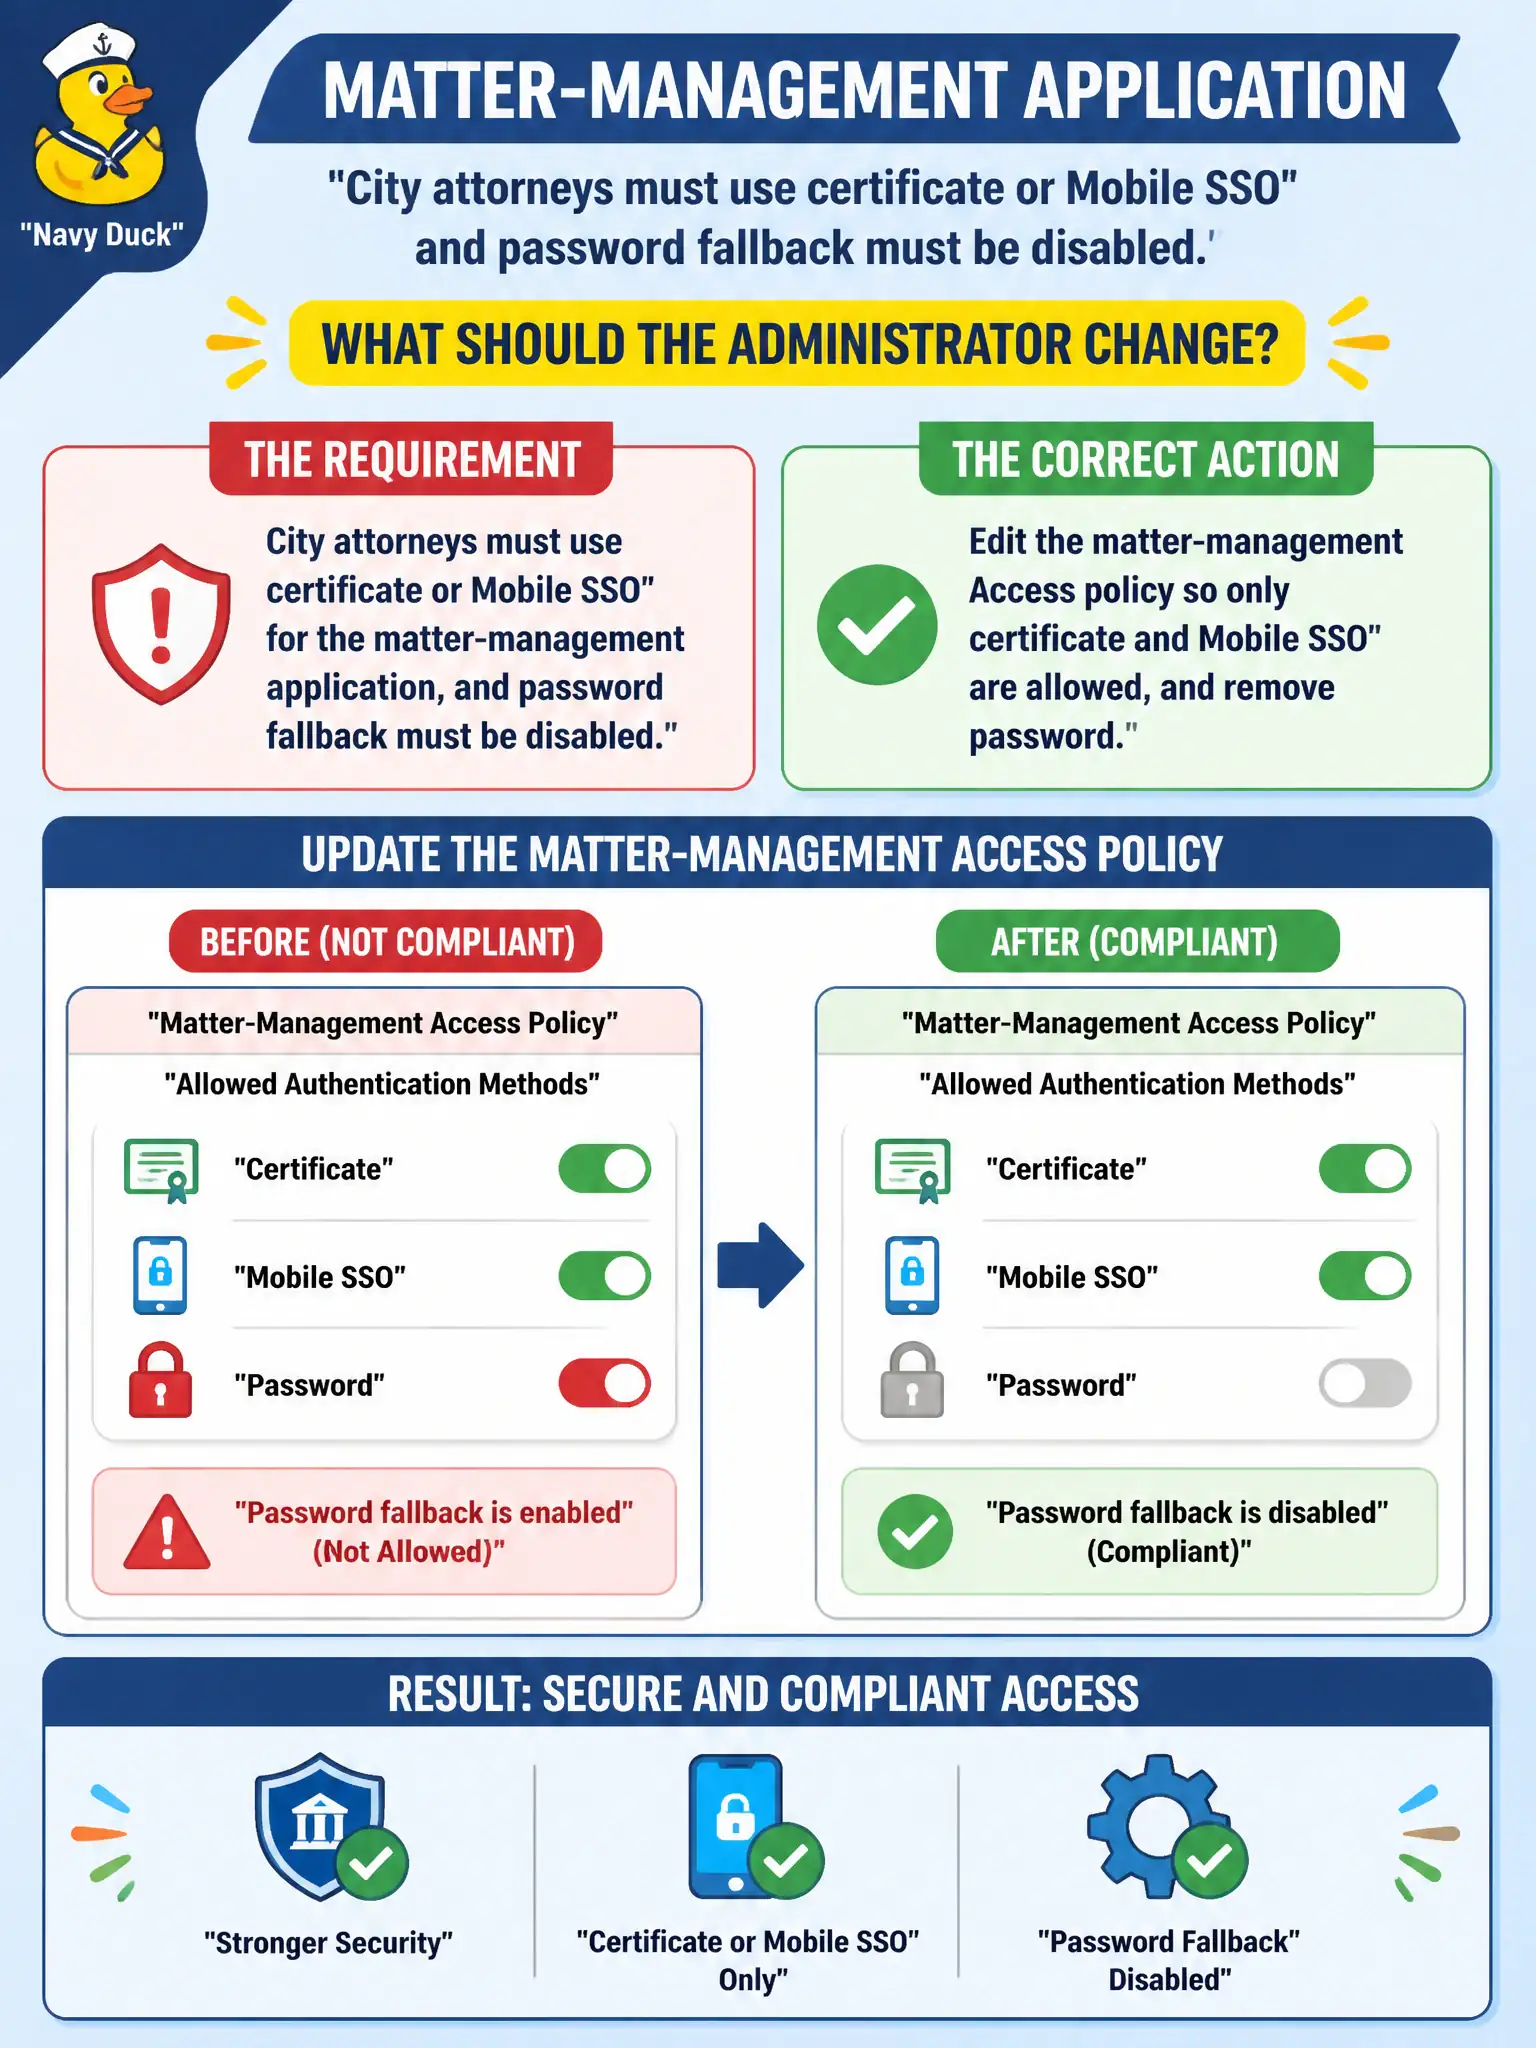
City attorneys must use certificate or Mobile SSO for the matter-management application, and password fallback must be disabled. What should the administrator change?
Select an answer to reveal the explanation.
Short Explanation
Allowed methods are a menu on that one app, not a citywide famine. Take password off the matter-management Access policy and leave certificate plus Mobile SSO. Killing password for the citizen portal just to harden attorneys is the wrong blast radius.
Full Explanation
City attorneys must use certificate or Mobile SSO for the matter-management application, and password fallback must be disabled. Edit the matter-management Access policy so only certificate and Mobile SSO are allowed, and remove password—allowed methods are a menu on that one app, not a citywide famine. Leaving password enabled as a fallback on that application’s Access policy fails by concept because fallback undoes the certificate/Mobile SSO requirement. Disabling password globally for every application in the Access tenant, including the public citizen portal, fails because hardening attorneys must not break the citizen portal’s authentication model. Configuring Carbon Black Cloud to block lsass.exe so passwords cannot be used fails because blocking LSASS is destructive and is not Access method configuration. Exam caveat: constrain authentication methods per Access application policy—remove password only where required; avoid global password kill and CBC process blocks as SSO controls. Operational check: authenticate to matter-management with certificate or Mobile SSO successfully, confirm password is rejected for that app, and verify the citizen portal still has its intended methods. Coordinate certificate issuance for attorney devices before the password removal change window.