
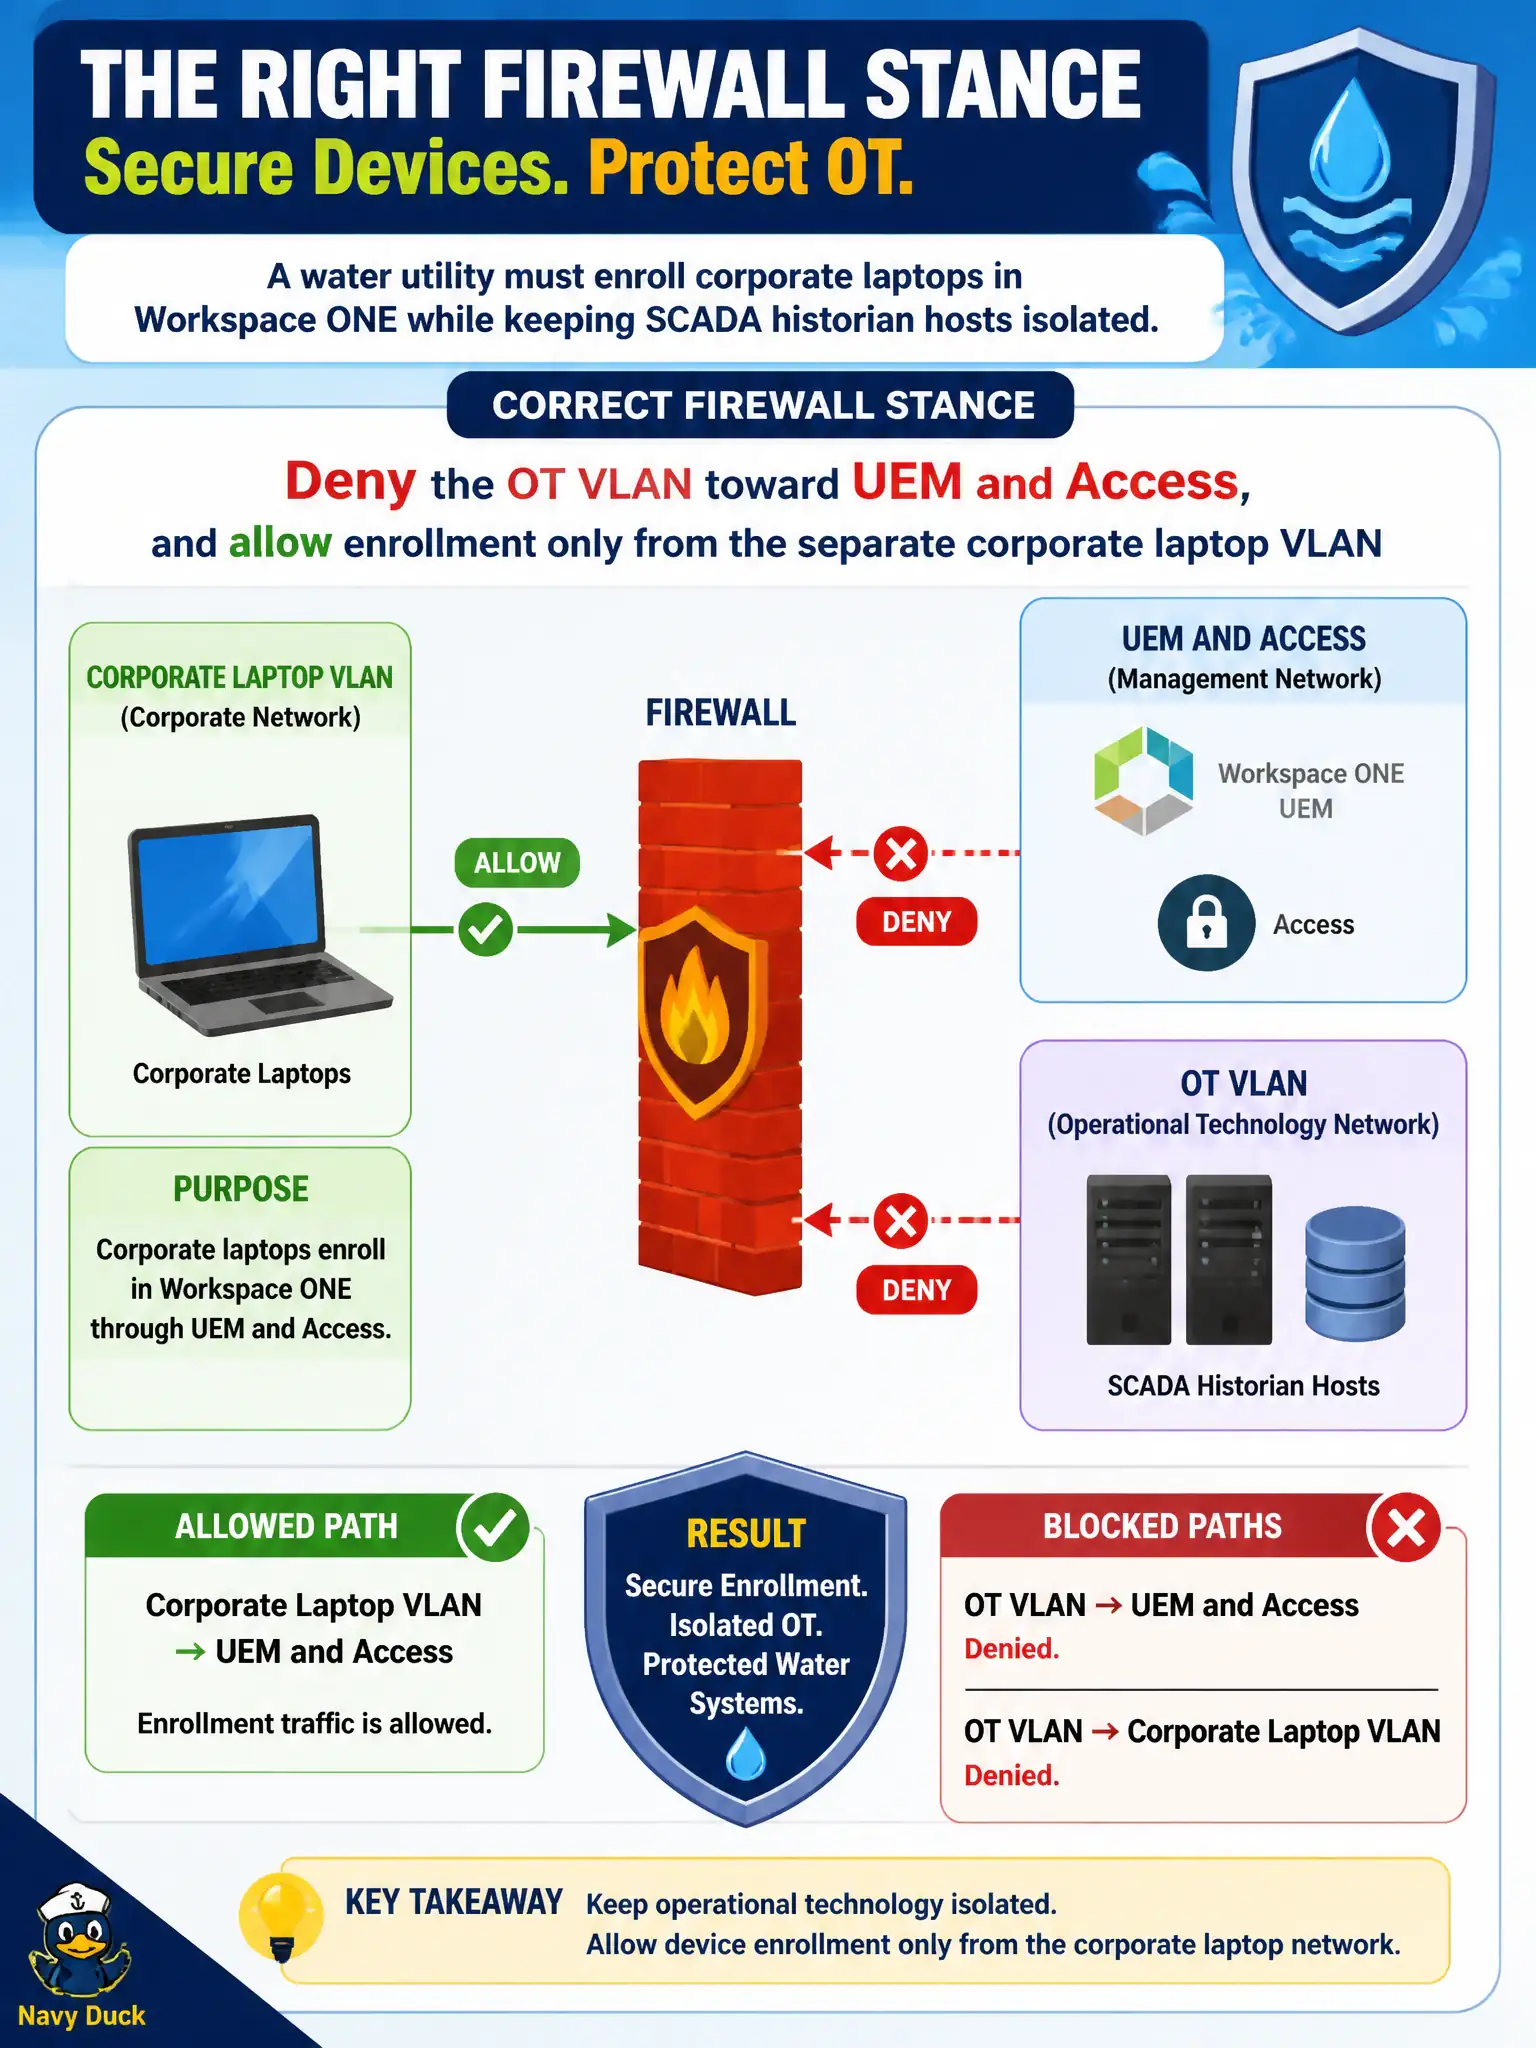
A water utility must enroll corporate laptops in Workspace ONE while keeping SCADA historian hosts isolated. What firewall stance should the security administrator take?
Select an answer to reveal the explanation.
Short Explanation
Enrolling office laptops is not a hall pass for the plant floor. Keep the OT VLAN away from UEM and Access, and enroll only the corporate laptop VLAN.
Full Explanation
A water utility enrolls corporate laptops in Workspace ONE while keeping SCADA historian hosts isolated by denying the OT VLAN toward UEM and Access and allowing enrollment only from the separate corporate laptop VLAN. Enrolling office laptops is not a hall pass for the plant floor. Allowing the OT VLAN the same UEM and Access destinations as laptops fails by concept because it extends the enterprise management plane into safety-critical OT. NATing SCADA historians onto the corporate enrollment VLAN fails because address translation into IT enrollment space breaks OT isolation and can inherit Hub paths historians should never have. Opening any-any from historians to Workspace ONE SaaS for patch telemetry fails because telemetry excuses do not justify OT-to-SaaS any-any and confuse MDM enablement with industrial security. Exam caveat: Workspace ONE enablement is scoped to enterprise endpoint VLANs; OT and SCADA stay denied toward UEM and Access. Operational check: enroll a corporate laptop successfully, attempt historian reachability to UEM/Access and confirm deny, and verify no NAT hairpin from OT into the enrollment segment. Document the OT deny in utility change control so future Hub rollouts do not temporarily open plant networks.