
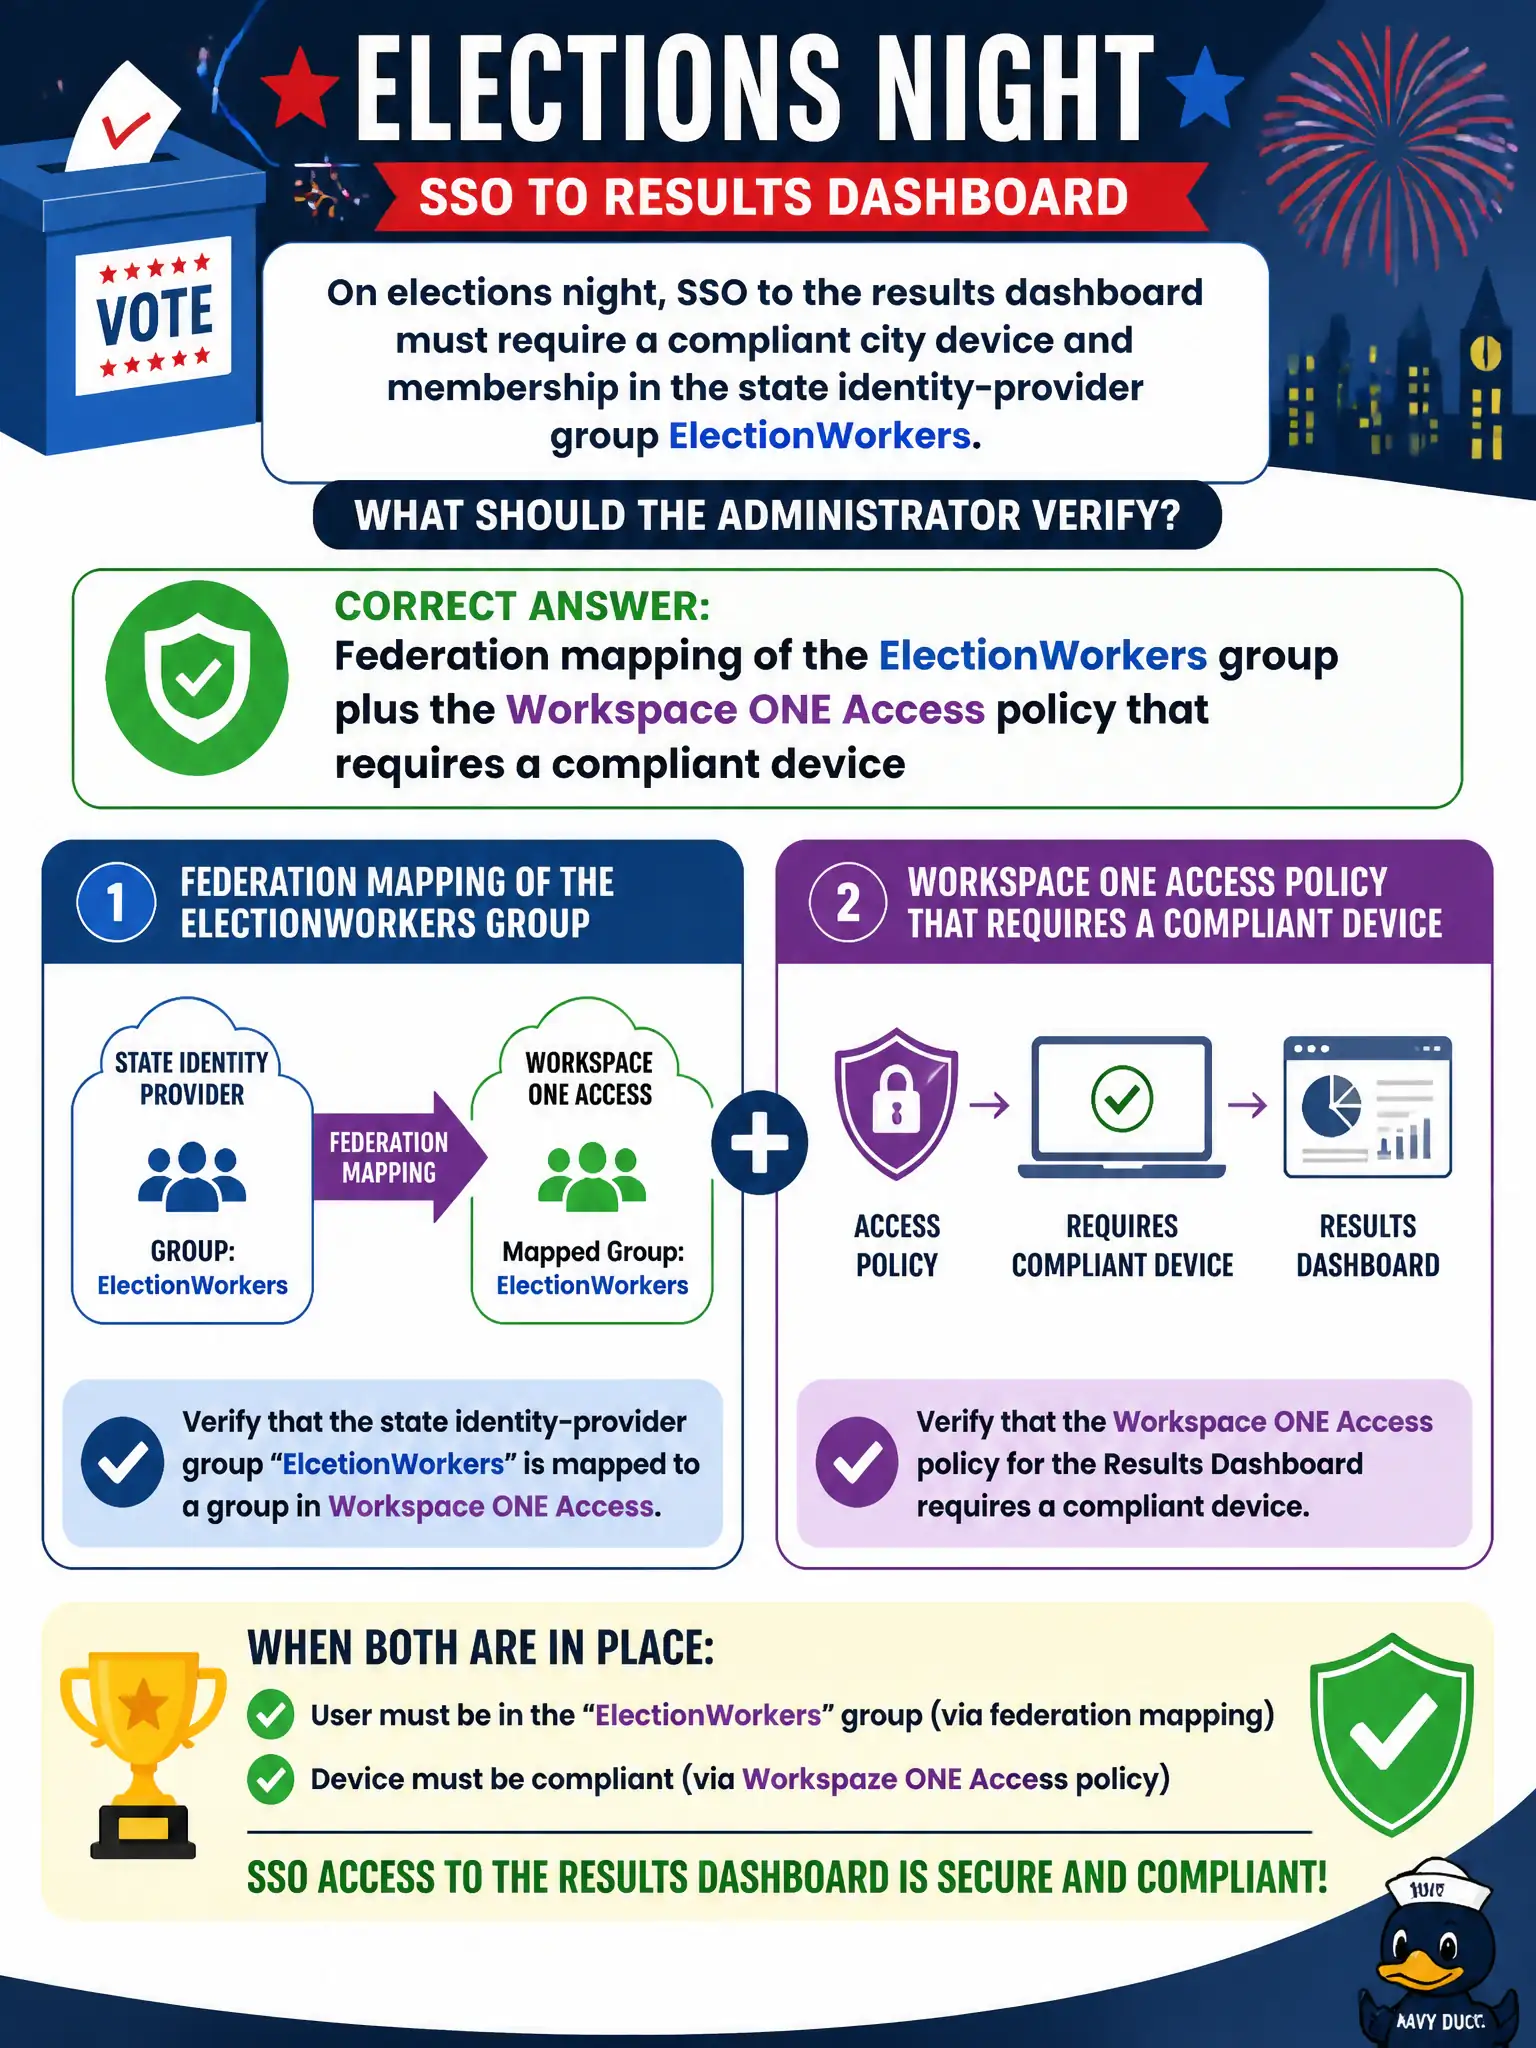
On elections night, SSO to the results dashboard must require a compliant city device and membership in the state identity-provider group ElectionWorkers. What should the administrator verify?
Select an answer to reveal the explanation.
Short Explanation
Election night is a two-check door: the state says you are an ElectionWorker, and Access says the laptop is a city device. Verify both—do not punch an any-any hole in NSX.
Full Explanation
On elections night, when SSO to the results dashboard must require a compliant city device and membership in the state identity-provider group ElectionWorkers, the administrator should verify federation mapping of the ElectionWorkers group plus the Workspace ONE Access policy that requires a compliant device. Treat that pair as both the election-worker roster claim and the city-device badge check before the results dashboard unlocks. A last-minute NSX-T Distributed Firewall any-any rule toward the results VIP fails by concept because network any-any does not implement identity-group and device-compliance SSO gates. Carbon Black Cloud deletion of sensors on election-night kiosks fails because removing sensors weakens endpoint defense and does not enforce Access group-and-compliance policy. Guest Introspection uninstall on the results cluster so identity is not evaluated fails because uninstalling GI breaks Identity Firewall capability and is the opposite of verifying identity-aware access. Exam caveat: end-to-end civic SSO is operated in Workspace ONE Access—verify federated ElectionWorkers mapping and compliant-device policy. Operational check: confirm ElectionWorkers group claim mapping, test Access policy with compliant and non-compliant devices, verify non-members are denied, and freeze the verified Access configuration for election night with a documented change freeze.