
Courts Identity Firewall rules depend on Guest Introspection. A disaster-recovery test recovers case-management VMs, but user-based rules never hit because Guest Introspection is not deployed on the DR cluster. What should be added to DR prep?
Select an answer to reveal the explanation.
Short Explanation
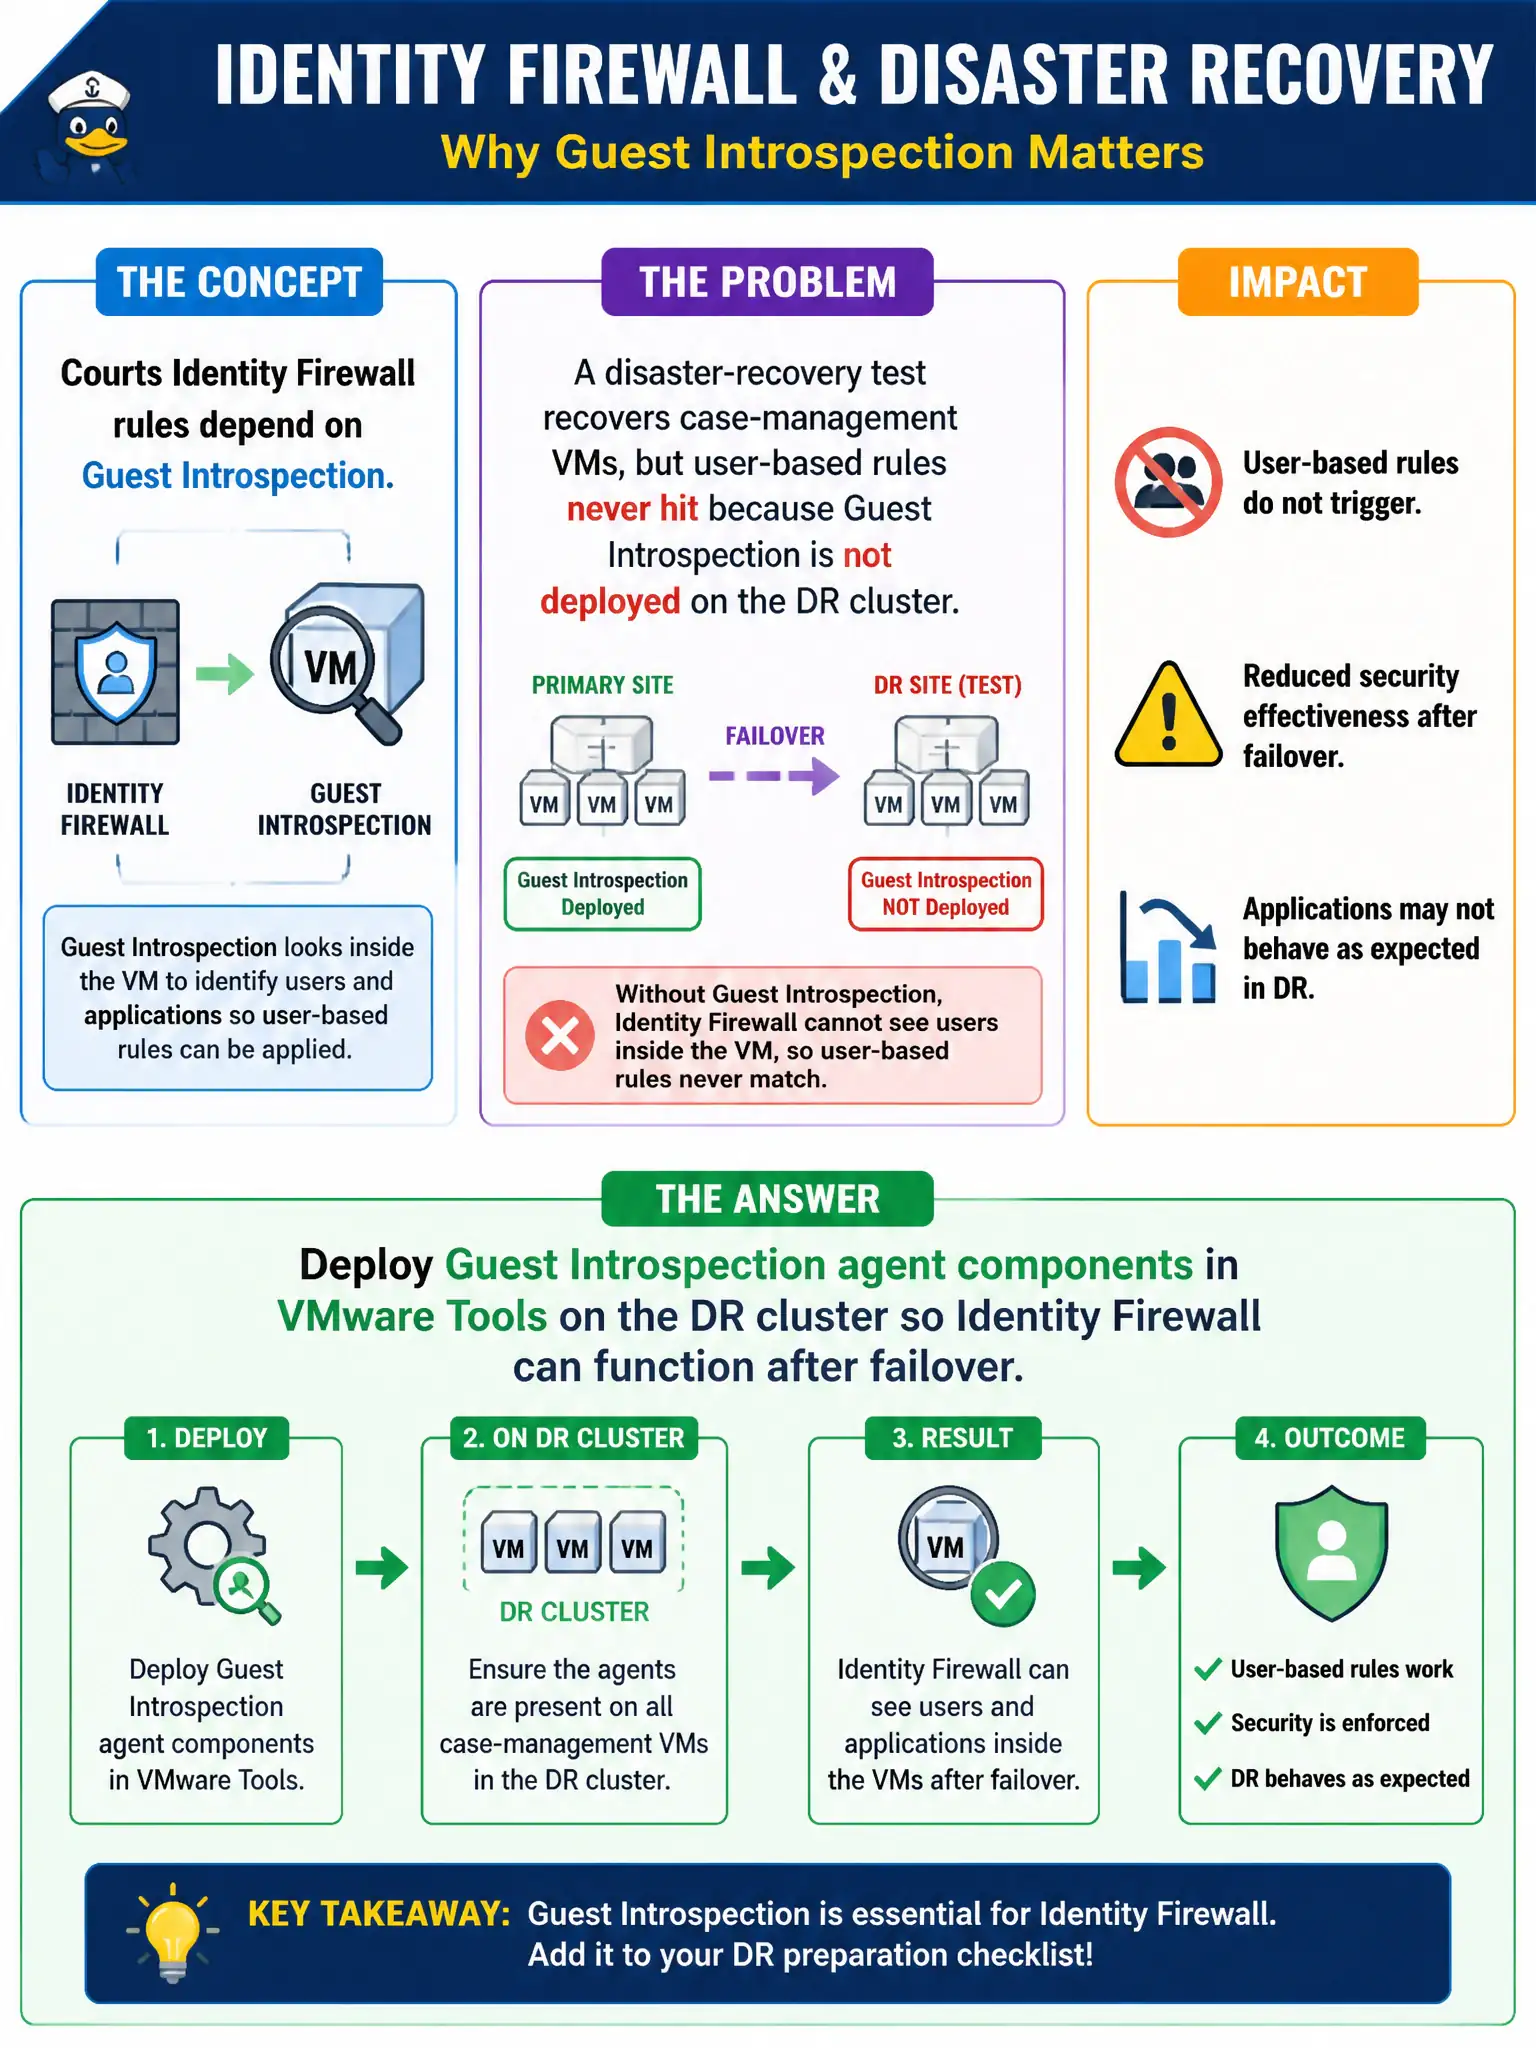
Identity Firewall is a name-tag reader, and Guest Introspection is the scanner in the doorway. If DR never got the scanner, user rules go blind. Put GI on the DR cluster before the next failover test.
Full Explanation
When courts Identity Firewall rules depend on Guest Introspection and a DR test recovers case-management VMs but user-based rules never hit because Guest Introspection is not deployed on the DR cluster, DR prep must deploy Guest Introspection agent components in VMware Tools on the DR cluster so Identity Firewall can function after failover. Treat Guest Introspection as the badge reader that Identity Firewall needs on every courthouse floor, including the warm site. Replacing Identity Firewall with Tier-0 static routes at DR fails by concept because static routes do not provide user-based firewall decisions. Disabling VMware Tools on recovered VMs to force IP-only Distributed Firewall fails because that removes the GI path Identity Firewall requires and abandons user-aware policy. Installing Horizon Connection Servers on the DR cluster as an Identity Firewall substitute fails because Horizon Connection Servers are not Guest Introspection for NSX Identity Firewall. Exam caveat: Identity Firewall at DR requires Guest Introspection readiness on the recovery cluster; routes, Tools disable, and Horizon are not substitutes. Operational check: deploy GI components on the DR cluster, recover a case-management VM, confirm Identity Firewall user hits, and add GI readiness to the courts DR checklist.